Security is most effective when it is both unobtrusive and robust. Currently, Physical Access Control Systems (PACS) have transformed into a critical component of enterprise risk management.
They serve as a data point for every door event and a control mechanism for every credential decision. This transition is driven by standards such as ISO/IEC 27001:2022, which necessitate physical security perimeters to safeguard unauthorised access to information and related assets through defined zones and controlled points of entry.
Physical access authorisation
NIST SP 800-53’s Physical and Environmental Protection (PE) controls further emphasise the importance of structured physical access authorisation and exit/entry access control. These controls underscore the need for identity-aligned access policies rather than mere ad-hoc badge exceptions.
Modern deployments rely on product and performance standards like UL 294, which tests access control system units, and IEC 60839-11-1, which provides minimum functionality requirements for electronic access control. When recognised controls and validated components form the basis of physical access control systems, operational compliance becomes streamlined, allowing teams to move fluidly and the security infrastructure to scale effectively without becoming a burden.
Industry standards focus
Transitioning to proactive enforcement from reactive monitoring is crucial for future-readiness
Transitioning to proactive enforcement from reactive monitoring is crucial for future-readiness. Industry standards focus on achieving three outcomes: ensuring only authorised entrants gain access to designated zones, maintaining a clear record of entries and exits, and ensuring systems adapt to evolving physical and cyber threats.
This aligns with ISO/IEC 27001's physical access control mandate and NIST SP 800-53's requirements for organisations managing sensitive assets.
Frictionless and secure authentication
The evolution of physical access control systems also addresses the authentication deficiencies of legacy systems. Modern solutions move away from RFID cards and PINs towards high-assurance credentials such as mobile NFC, fingerprints, and facial recognition, which offer security with minimal effort.
Intelligence-driven policies: Role, location, and time
To ensure structured governance, advanced physical access control systems anticipate enforcement across several dimensions: distinguishing entry permissions by role, restricting access based on temporal factors like shifts, and controlling zone management to limit visitor movement beyond designated areas.
These systems go beyond basic regulatory compliance to meet specialised industry needs. For example, manufacturing systems integrate with safety protocols to restrict access to high-risk machinery zones to only those with valid safety certifications.
Auditability: "If It Isn’t Logged, It Didn’t Happen"
Modern audit processes require systems that support instant report generation, including real-time alerts for tampering, immediate notification escalation, and comprehensive audit trails for incident traceability.
Infrastructure and integration
Matrix exemplifies how security evolves from standalone hardware to a cohesive IT system
Today's Physical Access Control Systems directly integrate into organisational IT frameworks via IP-based networking and PoE-powered devices. This facilitates easy expansion and enhances system uptime. Integration with fire alarms, video surveillance, and HR systems supports a comprehensive security approach, triggering automatic responses to incidents and verifying door events with video footage.
Matrix exemplifies how security evolves from standalone hardware to a cohesive IT system. Through seamless integration, Matrix enables features like automatic unlocks on fire alarms and video verification for door events, reinforcing a modern security posture.
In conclusion, adopting a modern physical security strategy signifies more than complying with technical requirements—it commits to excellence. With systems designed for security, driven by policy, and prepared for audits, they become integral to success. Matrix provides a fully integrated ecosystem, setting new standards in security and innovation and fostering a facility that is ready for the future.
Security is most effective when it is invisible yet invincible. Today, Physical Access Control Systems (PACS) have evolved into an auditable, policy-driven layer of enterprise risk management—where every door event is a data point, and every credential decision is a control.
Standards and frameworks increasingly expect this: ISO/IEC 27001:2022 explicitly calls for physical security perimeters to prevent unauthorised physical access to information and associated assets, pushing organisations toward defined zones, controlled entry points, and consistent enforcement.
Physical access authorisation
In parallel, NIST SP 800-53’s Physical and Environmental Protection (PE) control family formalises practices like physical access authorisation and access control at entry/exit points, reinforcing the need for identity-aligned access policies and review cycles—not ad-hoc badge exceptions. From a system assurance standpoint, modern deployments also lean on product and performance standards such as UL 294 (testing for access control system units) and IEC 60839-11-1 (minimum functionality and performance requirements for electronic access control).
Net-net: when Physical access control systems are built on recognised controls and validated components, teams move fluidly, compliance becomes operationalised, and security infrastructure scales cleanly with growth—without becoming a bottleneck.
Industry standards focus
Understanding what industry standards actually require
To remain future-ready, organisations must shift from reactive monitoring to proactive enforcement. Industry standards focus on three measurable outcomes:
- Authorised Access Only: Ensuring only verified individuals gain entry to specific zones.
- Auditable Activity: Maintaining a clear, provable record of every entry and exit.
- Evolutionary Security: Ensuring systems remain resilient as physical and cyber threats evolve.
This aligns with globally recognised frameworks such as ISO/IEC 27001, which mandates physical access control systems as part of information security governance, and NIST SP 800-53, which outlines requirements for organisations handling sensitive assets.
Frictionless and secure authentication
One of the largest compliance gaps in legacy systems is outdated authentication. Modern Physical Access Control Systems are moving away from easily shared or cloned RFID cards and PINs toward high-assurance credentials.
- Mobile & Biometric Solutions: Utilising mobile NFC, fingerprints, or face recognition ensures that security is as easy as a glance or a tap.
- Reducing Risk: These methods significantly reduce the likelihood of credential sharing and unauthorised entry.
Intelligence-driven policies: Role + location + time
Industry-grade physical access control systems are never "one user = one door". Standards expect enforcement across multiple dimensions to ensure structured governance:
- Role-Based Access: Allowing only authorised staff into sensitive areas like R&D zones or server rooms.
- Temporal Control: Restricting access based on shifts or business hours.
- Zone Management: Limiting visitor movement beyond reception areas.
Advanced features for regulated environments
For industries such as banking, healthcare, and pharmaceuticals, certain preventive features are now the expected baseline:
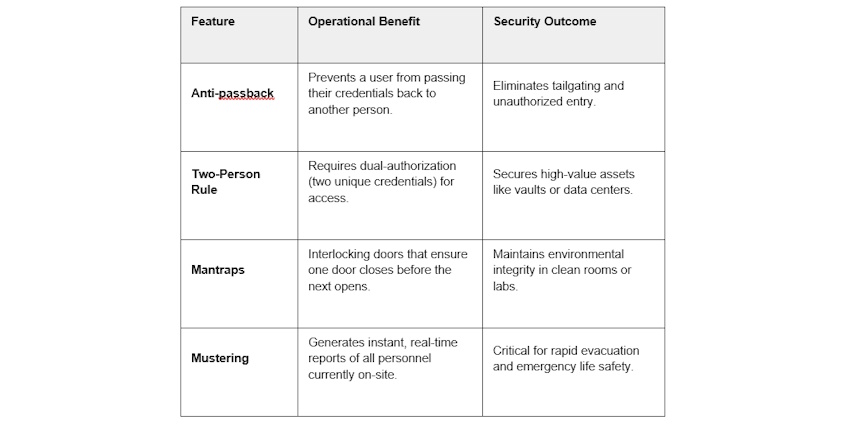 |
| Advanced features for regulated environments |
Beyond the Basics While general standards provide the framework, niche regulations demand specialised execution. For example, In Manufacturing, their systems integrate with safety protocols to ensure that high-risk machinery zones are only accessible to personnel with valid, up-to-date safety certifications, grounding digital policy in physical reality.
Auditability: If It Isn’t Logged, It Didn’t Happen
A major red flag in modern audits is the inability to generate reports instantly. The system must provide:
- Real-Time Alerts: Immediate notifications for tamper attempts or forced-open doors.
- Instant Escalation: Automated notifications via email or SMS.
- Audit Trails: Downloadable historical reporting and incident traceability.
The power of infrastructure and integration
Modern Physical Access Control Systems no longer operate in isolation. They integrate directly into the IT backbone using IP-based networking and PoE-powered devices, simplifying expansion and improving uptime. Furthermore, integrating with fire alarms, video surveillance, and HR systems ensures that the security posture is holistic—where a fire alarm triggers an automatic unlock policy and a door event is verified by video.
Matrix transforms the security from a standalone hardware setup into a unified IT backbone. By using IP-based networking and PoE-powered devices, they simplify the infrastructure while ensuring that a fire alarm can trigger an automatic unlock or a door event can be instantly verified by video.
Conclusion: The matrix standard
A modern physical security posture is more than a technical requirement; it is a commitment to excellence. When the Physical Access Control Systems are secure by design, policy-driven, and audit-ready, they become a silent partner in the business’s success.
In this landscape, Matrix stands as a beacon for organisations seeking more than just hardware. Matrix provides a holistic ecosystem where physical security meets cutting-edge innovation—offering everything from biometric door controllers to cloud-based multi-site management. With Matrix, users don’t just meet the industry standards of today; they define the standards of tomorrow. Experience a world where security is seamless, compliance is effortless, and the facility is truly future-ready with Matrix.





