Physical security

Allied Universal®, the security and facility services company, announces that Josh Ball has joined the company as vice president of field operations, quality control and special events for its Allied Universal Event Services business unit. Ball brings more than 20 years of experience leading security for professional sports, marquee events and critical infrastructure. In his new role, he will oversee operational quality assurance, including event quality control inspections, internal audits...

Critical national infrastructure encompasses sectors such as energy, utilities, healthcare, and data centers – environments that underpin economic stability and public safety. With so much at stake, the importance of effective security systems is that much higher. We asked our Expert Panel Roundtable: What are the unique aspects of the critical infrastructure market, and how should the security industry adapt?

Mercury Security, a pioneer in open architecture access control hardware and an HID brand, releases its 2026 Trends in Access Controllers Report, revealing how changing cybersecurity requirements, interoperability needs, cloud adoption and emerging technologies are putting greater emphasis on the role controllers play in long-term physical access control strategy. Based on a global survey of 561 physical security and cybersecurity professionals, including administrators responsible for access c...

There was a time when physical security and cybersecurity occupied two very different worlds. One was concerned with the nuts and bolts of locks, doors and perimeter protection. The other focused on networks, software and digital threats. Today’s modern access control systems – used in everything from offices and hotels to hospitals and data centres – combine the two, fusing mechanical engineering and cloud platforms. That means that a door is no longer simply a physical barri...

Chubbsafes, part of Gunnebo Safe Storage, has launched a new technical discussion guide examining when certified storage should be reviewed based on the value of jewellery and precious metals. Developed for jewellery retailers, manufacturers, bullion dealers and security professionals, When Asset Values Rise, Should Storage Be Reviewed? explores the relationship between certified storage, declared asset values and physical security. It considers the technical factors influencing safe storage, f...

As millions of people jet off for their summer holidays or make their way home, airports are under increased scrutiny. For many, their eagerly awaited trip begins and ends in the airport. Meeting passenger expectations with a seamless and secure journey from check-in to boarding is critical at a time when passenger numbers are rising, with almost 1.1 billion air passengers travelling through EU airports in 2025, an increase of 4.8% year-on-year. Increased complexity ahead But there are headwi...
News

Zygal, Cloud AI Surveillance Platform, has appointed Jason Bezuidenhout as Chief Revenue Officer (CRO), strengthening its leadership team as the company continues to expand its presence across international markets. Jason brings around two decades of experience in sales and business development, with a career spanning the rapidly evolving security technology landscape. His experience includes electronic surveillance, CCTV, cloud-connected security solutions, remote video monitoring and AI-driven security technologies, giving him a broad perspective on how technology is reshaping the way security is delivered. Autonomous security technologies Over the course of his career, Jason has worked across multiple territories and markets, with a particular focus on building distribution networks, partnerships and strategic alliances. His recent experience has been strongly focused on Remote Video Monitoring (RVM), with the North American market representing a significant part of his work over the past decade. Prior to joining Zygal, Jason held senior leadership positions with organisations such as Webeye and Robotic Assistance Devices. At Robotic Assistance Devices, he was involved in bringing AI and autonomous security technologies into monitoring centres and large-scale security operations. AI-enabled security operations Jason’s career has followed the evolution of the security industry from traditional CCTV and electronic surveillance towards remote monitoring, cloud-based platforms and AI-enabled security operations. His appointment comes at a time when organisations are increasingly looking to move beyond simply detecting security events towards faster verification, intelligent decision-making and coordinated response. Speaking about his approach to the industry, Jason said: “My approach has always been centred on understanding our clients’ businesses and challenges, and then helping them achieve their goals using the best technology available.” Commenting on the appointment, Sumanyu Vashistha, Founder & CEO, Zygal, said: “Jason brings a valuable combination of deep security industry experience, international market knowledge and a strong understanding of how technology can address real-world security challenges. His experience in building distribution networks, partnerships and alliances, particularly across the North American market, will be an important addition as we continue to strengthen our global presence. We are excited to have Jason join Zygal and look forward to the role he will play in accelerating our growth and taking our AI-powered security solutions to new markets.” Physical security operations As Chief Revenue Officer, Jason will focus on strengthening Zygal’s global commercial strategy, developing new markets and partnerships, and expanding the company’s reach among organisations looking to modernise their physical security operations. “Security technology is going through a significant transformation, and the opportunity is no longer simply about adding more technology to existing security systems,” said Jason. “It is about making security operations more intelligent, connected and responsive. I’m excited to be joining Zygal at this stage of its journey and to help take its technology to more organisations and markets globally.” With Zygal’s cloud-native platform bringing together video surveillance, AI-powered intelligence and security operations, Jason’s experience across RVM, technology partnerships and international business development will support the company’s next phase of growth.

XSponse, a provider of connected safety and emergency response technology, announces the appointment of Richie Perna as Chief Revenue Officer (CRO), effective September 19. Perna will lead XSponse’s national go-to-market strategy as the company moves into its next phase of growth and market expansion. Perna joins XSponse at a pivotal point in the company’s growth. Following a recent strategic investment from Armory Capital, XSponse is accelerating its national expansion and moving from a period of rapid product development into a more aggressive phase of market development, demand creation and commercial growth. Emergency response technology The appointment also reunites Perna with XSponse CEO Lee Mandel, with whom he spent nearly eight years building strategy, expanding into new markets and scaling a security business through a successful exit. “Richie is not a traditional CRO, and that is exactly why I wanted him in this role,” said Lee Mandel, CEO of XSponse. “He is a market maker. He understands customers and this industry, knows how to create demand where it doesn’t yet exist, and has the ability to build relationships and open doors that very few people can. I’ve already built a business alongside Richie, and I know what happens when we put the right product in front of him. Bringing him to XSponse full time is a major part of our plan to take this company nationwide.” Broad connected technology ecosystem As CRO, Perna’s role will extend well beyond traditional sales leadership, with broad responsibility for how XSponse is positioned, brought to market and expanded nationally. He will lead the company’s go-to-market strategy, strategic partnerships, channel development and demand creation, with K-12 as a core focus, while building the market presence and commercial momentum needed for XSponse’s next stage of growth. A major part of that strategy will be simplifying how XSponse goes to market. The company has developed a broad connected technology ecosystem in a relatively short period of time, and Perna will focus on bringing those capabilities to customers through clearly defined solutions built around specific operational and safety challenges. Life-safety technology “We have incredible technology, but great technology by itself doesn’t build a great company,” said Perna. “The market has to understand it, customers have to want it, and partners have to know how to bring it to their customers. That’s where I see the opportunity. My job is to help make XSponse a company that people across this industry know, create real demand for what we’ve built, and put us in the rooms and markets where we belong.” Perna most recently served as Chief Strategy Officer at Day Automation / Stark Tech, where his work centered on strategic growth, market development and large-scale school safety and security initiatives. His experience spans physical security, public address and intercom systems, emergency communications and mass notification, access control, video surveillance, lockdown systems and integrated life-safety technology. Public safety stakeholders Throughout his career, Perna has worked closely with school district leaders, technology and facilities professionals, public safety stakeholders, consultants, manufacturers, integrators and other industry partners. His approach has consistently centered on understanding the customer’s actual operational challenge first, then bringing together the technology, relationships and strategy needed to solve it. “Security and communications have become too fragmented,” Perna added. “Customers need technology that connects seamlessly with their operations, strengthens performance and delivers meaningful value. They need systems that work together and give people better information when something happens. XSponse has an opportunity to become the connective layer across that environment. That’s a much bigger story than any one product.”

Imagine, for a moment, sitting in parents’ or grandparents' living room. There’s a coffee table, and it’s cluttered with three or four different remotes, all controlling different systems. One for the TV, one for the set-top box, one for the DVD player (remember that?), and a fourth for the audio system. Simply tuning into the evening news involved a complex process of turning on the TV with one, switching the HDMI over with another, and adjusting the sound with yet another remote. One wrong button press, one wrong remote, and suddenly a blank screen or a “no signal” message. Poor user experience This complexity and poor user experience have long been mirrored in the security industry. Over time, many video management systems (VMS) evolved to resemble those old, button-heavy remotes. Every time a client requested a new feature, a new interface was rolled out with more buttons, more screens, and more toggling. That’s not how an operator is going to get their job done quickly and efficiently. It’s time to rethink the modern VMS. No longer is this system a way of viewing footage; instead, it has become the engine behind the security function. And to use it effectively, operators need a simple and intuitive interface. Preventing situations from escalating The number of digital interfaces that operators need to manage has increased in recent years, causing cognitive load and task switching to also rise. Research shows that workers take around 23 minutes to re-focus after switching tasks or systems, losing between 20 to 40% of productivity as they reorient. Preventing operators from jumping between disconnected applications and hidden menus allows them to focus on protecting assets, preventing situations from escalating, and responding to events. The most effective VMS is a consolidated system, divided into logical blocks and tabbed navigation, so operators understand where functions are and can see footage at a glance. Supporting future growth With the front-end experience improved, focus can shift to the infrastructure and hardware behind it. It can be easy to pick a VMS based on the cost of a single-channel licence and believe that this is the most cost-effective solution. However, licenses are usually the start of your costs, with hardware, server maintenance, infrastructure, and deployment time also impacting the total cost of ownership (TCO). As AI capabilities advance, organisations need infrastructure that can scale without driving up unnecessary costs. Traditional deployments often require additional servers to provide redundancy and support future growth, meaning hardware, rack space and power are allocated long before they are needed. This can leave valuable resources sitting idle while still adding to operational costs. Maintaining system resilience Choosing a VMS with active-active failover clustering helps eliminate this inefficiency. Instead of maintaining standby servers that sit idle until a failure occurs, multiple servers actively share the workload under normal operation. If one server fails, the remaining servers automatically take over, maximising available computing resources while maintaining system resilience. For designers of enterprise-scale systems, this provides a strong foundation. A single server can support up to 256 devices, while a clustered deployment scales to 12,800 channels. Organisations managing multiple locations can also connect sites through cloud federation, enabling centralised management without adding operational complexity. Integrating legacy infrastructure Just as importantly, modernising an existing deployment does not have to mean starting from scratch. Comprehensive support for established ONVIF standards, RTSP streams and a robust open API makes it straightforward to integrate legacy infrastructure, avoiding vendor lock-in while providing a future-ready platform that can adopt new protocols as they emerge. Even the licensing model becomes more straightforward. One license equals one camera. However, when connecting IP speakers or intercoms, a single license covers up to four devices. When integrating an NVR, one license covers eight channels. This hardware optimisation combined with a flexible licensing approach ultimately delivers a significantly more cost-effective and stable deployment. Improving operator performance Often, the biggest improvements to productivity come when an individual understands how to use a system effectively. The interface, as touched on before, is a significant influence on this. Advanced video analytics and AI-powered search features play a role too. For example, if an operator needs to search for an event, such as overcrowding in a busy car park, video analytics can help them search the footage quickly. Instead of hours of manual footage scrubbing, the operator can use an event histogram (a type of graphic that shows baseline and spikes in events) to quickly identify times when an anomaly occurred. They can jump directly to those events with a single click to investigate what happened. Unique visual characteristics If an operator needs to find a specific object, such as a vehicle of interest, they can use AI-powered search to sift through footage based on unique visual characteristics. For example, the vehicle type, make, model, and colour. Not only will they see relevant footage, but they can track this vehicle across different cameras to see where it travels across the car park. Taking this a step further, some VMS platforms now support semantic search powered by generative AI. Rather than relying on predefined metadata such as clothing colour or object type, operators can use natural language to describe what they are looking for. For example, they can search for "a woman holding a phone," and the system understands the context to locate relevant footage, making it easier to find events that may have been difficult to identify using traditional attribute-based searches. Overall cybersecurity posture Physical security systems are an integral part of IT infrastructure and are subject to stringent audit requirements. The NIS2 Directive and the Cyber Resilience Act (CRA) leave no room for compromise. Modern-day VMS need to address these challenges at every layer of the network. Look for features such as encrypted camera communications to tamper-resistant exported clips, and intelligent session management. Audit logs will record every user action, which helps spot unusual behaviour that could signal a breach; meanwhile, automatic HTTPS negotiation and JWT-based authentication ensure the VMS meets gold-standard IT security requirements. Some VMS are deployed within hardened, closed operating environments that prevent user access to the underlying operating system. This minimises the operating system as a potential attack surface and helps strengthen the overall cybersecurity posture. Advanced analytics and AI The VMS has come a long way since its invention in the early 1940s. Taking the time to understand the options available now can ensure the security function performs optimally, safely, and cost-effectively. The best VMS can be learned quickly, with intuitive interfaces that don’t require a thick manual or days of training. They unify different security features and systems, so operators don’t waste time switching between applications. And they have a robust infrastructure that supports advanced analytics and AI.

Accredit Solutions, the global accreditation and workforce management technology provider for major events, venues and high-security environments, today announced the launch of Accredit Induct, a workforce readiness and compliance enforcement product that connects induction, identity, accreditation and access control into one operational workflow. The launch comes as venues, stadiums, arenas, visitor attractions, public spaces and event operators prepare for the implementation of the Terrorism (Protection of Premises) Act 2025, commonly known as Martyn's Law, considered to be a major development in UK counter-terrorism and protective security legislation in the last 20 years. Protective security procedures The Act seeks to improve organisational preparedness and protective security across the UK’s venues and events, placing new statutory duties on private and public organisations to actively mitigate terror risks to the public. It places emphasis on staff preparedness, awareness, training and documented protective security procedures so that staff can respond effectively in the event of a terrorist incident. While organisations have traditionally relied on classroom briefings, PDFs, spreadsheets and standalone learning systems, Accredit Solutions believes the industry faces a more fundamental challenge: how can venues prove that the right people have completed the right requirements before credentials or access are granted? Accredit Induct has been developed to answer that question. Eliminating duplicate applications Built on the Accredit Platform and aligned to the Accredit OS operating model, Accredit Induct enables organisations to assign role-based training, deliver induction content digitally, track completion in real time, and crucially, enforce compliance before credentials or access permissions are issued. In simple terms, this means ‘no induction, no access’. The platform creates a single source of truth across accreditation, induction and operational readiness, streamlining processes by eliminating duplicate applications and fragmented systems with limited visibility. While a traditional learning management system (LMS) delivers training content, Accredit Induct goes further by connecting induction status to identity, accreditation and access permissions, so completion is not simply recorded, it can become a condition of credentialing and entry. Learning management system "Induction has too often been treated as a separate administrative exercise. In high-pressure venue and event environments, it should be part of the access decision. Accredit Induct connects identity, induction status and accreditation, giving organisations the visibility and control to ensure people are ready before credentials or access are granted.” said CEO, Peder Berg. The launch reflects a growing recognition across the venue and event sectors that workforce readiness is increasingly becoming part of the same operational control framework as physical security and access management. Organisations operating complex Accredit Induct has been specifically designed for organisations operating complex, rotating workforces, but unlike traditional learning management systems (LMS), Accredit Induct is designed around operational readiness rather than content delivery alone. The platform allows organisations to: Prevent credentials being issued until mandatory training has been completed: no induction, no access. Maintain a single identity record across accreditation, induction and access workflows. Assign training automatically based on role or accreditation type. Track completion status in real time. Manage expiry dates and refresher requirements. Create auditable records for health and safety, insurers and regulators. Deliver videos, documents, assessments and compliance content online. Complex accreditation operations The launch builds on Accredit Solutions' established presence within global sport, live entertainment, government and high-security, environments, where the company supports some of the world's most complex accreditation operations. As regulatory expectations increase and organisations seek greater visibility over workforce readiness, Accredit Solutions believes the future lies in connecting identity, training, compliance and access within a single operational framework. This allows organisations to make access decisions based not only on who someone is but whether they have completed the required training, met the necessary compliance requirements and are ready to enter. "Knowing who is on site is important," added Peder Berg. "Knowing they are trained, compliant and ready to perform their role has become just as critical."

Robox AI announced the Robox AI Video Intelligence Platform, a configurable AI-powered platform that transforms compatible existing camera infrastructure into real-time actionable intelligence for loss prevention, safety, security, compliance and business operations. Centralised intelligence layer Instead of requiring organisations to replace their existing camera infrastructure or deploy multiple single-purpose analytics products, Robox AI provides a centralised intelligence layer that supports multiple use cases across one location or an enterprise with many locations. Built on a flexible edge-cloud architecture that connects with compatible existing IP camera environments, Robox AI combines AI technology with real-world security, loss-prevention, and operational experience. Robox AI’s on-site edge processing supports low-latency AI analysis, while its centralised software provides configuration, alert management, evidence, reporting, and analytics across multiple locations. Enhancing video intelligence Robox AI believes effective video intelligence requires more than producing an alert. Organisations also need to determine who receives the information, what action should follow, how the event is documented, whether the issue was resolved, and what can be learned from the accumulated data. The Robox AI Video Intelligence Platform analyses configured video streams, identifies events based on defined criteria, delivers relevant alerts and supporting event evidence to authorised personnel based on customer-defined rules, and connects those events to response, resolution, reporting, and analytics. Advances with the organisation Robox AI goes beyond what a system detects on the day it is installed. As retail crime, criminal behavior, safety concerns, operational priorities, and customer requirements change, Robox AI works with customers to evaluate emerging problems, refine existing detection models and, where appropriate, develop or integrate additional capabilities, optimise workflows, and measure results through an AI intelligence platform that advances alongside the organisations using it. This continuous-improvement model is intended to reduce the risk of organisations becoming locked into a static set of capabilities while their operating environment continues to change. “We believe an AI platform should evolve, not be installed and then stand still while the problems around the customer continue to change,” said David Solomon, CEO of Robox AI. “Retail crime evolves. Safety risks evolve. Operational challenges evolve. Our responsibility should not end when the technology is deployed." “Robox AI is built around an ongoing relationship with the customer. We work to understand the problem, configure the intelligence around that environment, refine the models, measure the results, and evaluate new detection capabilities as needs change. The goal is not simply to give an organisation the AI it needs today. It is to provide an intelligence platform that can continue advancing with its business,” Solomon concluded. Connects video with business data Robox AI integrates video intelligence with transaction and other business-system data. For retail and grocery environments, POS integration can add context for use cases such as sweethearting, scan anomalies, voids, refunds, and other transaction-related events. Combining visual intelligence with relevant business data can provide additional context, improve event confidence, and help organisations better understand what is occurring within the operation. Robox AI is designed around a broader operational workflow. When a configured event is identified, authorised personnel receive relevant alerts and event evidence based on customer-defined rules. The platform can then support the process beyond the initial detection through incident review, escalation, response documentation, resolution, reporting, historical analysis, and management accountability. This allows organisations to move beyond using video simply to determine what happened after an incident. Instead, video can become a proactive source of operational intelligence. Robox AI markets and use cases Robox AI can be configured to support a range of use cases depending on the customer’s environment, camera coverage, available data, operational priorities, and deployment requirements, including: Retail and Grocery: Shoplifting and concealment, cart push-outs, employee theft and sweethearting, self-checkout and transaction anomalies, loitering, crowd activity, fights and confrontations, queue conditions, out-of-stock conditions, unauthorised access, propped doors, slip-and-fall events, visible weapons, smoke or fire indicators, license plate recognition, and additional customer-specific operational events. Restaurants and Quick-Service Operations: Queue and occupancy conditions, loitering, fights and confrontations, visible weapons, unauthorised access, propped doors, slip-and-fall events, PPE compliance, smoke or fire indicators, and selected operational-process deviations. Warehouses, Distribution Centers, and Manufacturing: PPE compliance, restricted-area activity, worker-down or fall events, forklift and vehicle-related safety conditions, propped doors, crowd conditions, asset or material removal, smoke or fire indicators, and selected operational-process deviations. Schools and Other Public Environments: Visible weapons, fights and aggressive behavior, loitering, crowd activity, unauthorised access, perimeter events, smoke or fire indicators and license plate recognition, subject to applicable policies, laws and deployment requirements. Additional detections and integrations are evaluated based on customer requirements, camera placement, operating environment, data availability, and agreed deployment scope. Configurable rather than one-size-fits-all Robox AI customers select and prioritise capabilities based on individual locations, risks, policies, and operating objectives. A typical deployment may include: An edge AI appliance connected to compatible camera streams. Configured AI detection models. Real-time event alerts. Mobile and management access. Event clips and supporting evidence. Dashboards and analytics. Incident history and reporting. Customer-defined notification and escalation workflows. POS or other authorised data integrations. Multi-location management. Deployment and technical support. Ongoing model refinement. Evaluation of new customer-specific detections and capabilities. Availability The Robox AI Video Intelligence Platform is now available for customer evaluations, proof-of-value deployments, and commercial deployment. Organisations interested in evaluating the platform work with Robox AI to assess existing camera infrastructure, identify priority use cases, define detection and response requirements, establish measurable objectives, and develop an appropriate deployment architecture.

Genetec Inc, the global pioneer in enterprise physical security software, is now inviting contributions for the 7th annual edition of its global State of Physical Security report. In 2025, Genetec’s survey received responses from over 7,300 participants across six continents, offering valuable insight into emerging trends within the industry. The report found that interest in adopting AI has more than doubled among end users since the previous year. Additionally, security is increasingly being used as a strategic enterprise function, with systems delivering valuable business intelligence alongside protection of people and premises. Strategic enterprise function Guy Rushworth, Enterprise Account Executive, Genetec, says “Our Physical Security report gives us a direct line to the people actually running security operations day to day – end users, integrators, and consultants. This feedback doesn't just shape our own thinking; it helps the whole industry understand where the real challenges are, and where physical security is headed next. We'd encourage as many people as possible to take part and add their voice." The survey takes approximately 10 minutes to complete, and all responses remain anonymous. Participants have until 21st September to take part, and will receive early access to the final report plus entry into a random draw for one of eight £500 Amazon gift cards.

Expert commentary
The eagerness to adopt AI in physical security is increasing as teams want to implement technology solutions for faster, smarter operations. At the same time, the conversations surrounding AI have changed. The focus now includes not only efficiency gains but also concerns about accountability and trust. According to the Genetec 2026 State of Physical Security report, AI ranked alongside access control and video surveillance as a key priority. However, approximately 40% of the over 7,000 physical security leaders surveyed expressed concern about how AI systems use their data. The potential for malicious purposes followed close behind at 36%. You may recognise this tension in your own organisation. There is an expectation that AI can help operations and an understanding that AI entails risks. Balancing the two includes careful deployment and policies. Higher stakes demand a higher standard AI can quickly spot the difference and elevate the event to the security team Most AI applications in physical security revolve around automation. Basic examples include triggering events, filtering and classifying alarms, and enabling faster searches across video and event data. These applications tackle the persistent security challenges of too much noise and too little context. AI takes on some of the lifting, cutting the false positives that overwhelm operators and adding context to the events that remain. For example, someone loitering near an entrance may not be a notable event. While someone loitering and trying door handles is a priority. AI can quickly spot the difference and elevate the event to the security team. From there, the human operator can confirm the issue and next steps. AI narrows the operator's focus rather than replacing their judgment. Higher standard of supervision While these uses improve operator efficiency, they need to be implemented responsibly. Irresponsible AI usage in physical security is more than a simple inconvenience. The outputs affect safety and security. AI applications within physical security demand a higher standard of supervision. This oversight is often referred to as “human in the loop,” but perhaps a better phrase is "expert in the loop." The person validating an output needs the knowledge to question it, contextualise it, and overrule it if needed. How to deploy responsible AI Deploying responsible AI starts by defining where AI can add value to your specific organisation Deploying responsible AI starts by defining where AI can add value to your specific organisation. AI works best as a tool with a defined job. What is the problem that needs to be solved? What challenges are holding back the team? Start by identifying the problems, then work backward to a solution. Otherwise, you may be implementing technology that doesn’t fully meet your needs. Next, define parameters around AI usage within your team. Document exactly what AI is permitted to do and not allowed to do within your operations. Information should include which use cases you've approved, what data the system can access, and how issues escalate. By defining these elements, your team has clear guidelines on when AI tools are part of your security procedures and for what purposes. Cross-functional monthly meetings Because AI can behave unpredictably, it’s good to prepare for when something does go wrong. Even a well-built model will eventually drift from its thresholds. This is where governance comes in. Governance is what keeps responsible AI holding up over time. It sets the review cycles that catch an issue before an incident does. Governance related to AI entails data privacy, liability, and regulation. Input from legal, compliance, cybersecurity, and IT teams is important. Getting these groups together starts with something as simple as cross-functional monthly meetings to review use cases and emerging challenges. Consider also working with other manufacturers, integrators, and end users across your ecosystem. In doing so, you create shared standards that make issues diagnosable. Responsible AI as a practice, not a project The goal is to protect individual rights and build trust without hampering technological advancement Responsible AI usage in security is not a box to check or a project to complete. It's an ongoing practice, especially as the compliance bar rises. As more AI security risks surface, governments are drafting legislation to regulate how organisations can develop and implement AI-enabled technology. The goal is to protect individual rights and build trust without hampering technological advancement. Identified risk category For example, the 2024 AI Act in the European Union (EU) sets obligations for various AI applications based on their identified risk category. These requirements include creating adequate risk assessments and mitigation practices, using high-quality training datasets to reduce bias, and sharing detailed documentation on models with governing authorities as needed. In the US, multiple states have implemented legislation on AI use, and national legislation has been discussed. Organisations can begin by implementing documented processes for guidelines and governance: Conduct risk assessments: Evaluate how automating a specific process may impact critical systems or safety protocols Identify non-critical applications: Start by implementing AI into processes that aren’t central to your most critical operations to curb major business disruptions Prioritise human-centred design: Ensure that AI applications always empower humans with the information they need to make the best decisions Design for explainability: Ensure AI decisions can be explained and traced, so the expert in the loop can question, verify, or overrule them when needed. Broaden data protection strategies: Apply cybersecurity measures and best practices to AI-enabled solutions, including regular audits and system updates Choose trusted vendors: Work with vendors who follow responsible AI principles, considering biases, data protection, and cybersecurity Core pillar of physical security The industry is slowly converging on shared standards for AI governance. This is good news for early adopters who wish to shape the industry rather than react to it. The potential applications of AI in security are exciting. But as this technology evolves, so do the risks. Strong governance builds trust, a core pillar of physical security. Responsible AI protects that trust and earns more of it. Start by defining your outcomes, building guardrails, and creating accountability structures to support your organisation’s responsible use of AI technology.
In logistics hubs, production facilities and distribution centres, the access control system is invisible—until it isn't. For decades, the 125 kHz card has been the workhorse of industrial credentialing: inexpensive, reliable and universally understood. It does exactly what it has always done. That consistency has served many organisations well, even as security needs and credential From authentication to smart buildings, gain expert insights about unified access. The same card technology that opened the warehouse gate in 2005 is opening it today. And while operations teams have upgraded conveyors, ERP systems and warehouse management platforms, the front door has often remained on technology selected for an earlier era. Major operational event Why? It is rarely about a lack of awareness. More often, organisations are balancing cost, time and operational risk. In a facility that never stops, a full systemwide upgrade can feel less like a routine project and more like a major operational event. The path forward is continuous modernisation: deploying an agile access layer that adapts to new security requirements and credential technologies over time, rather than replacing everything at once. Universal reader technology makes that possible, without the “Big Bang” shutdown. Why legacy systems can benefit from modernisation The 125 kHz card (also named proximity, prox or low-frequency) helped set a practical standard for convenience and broad compatibility, but many organisations are now evaluating where its security model can be improved by newer options: Increased cryptographic protection. Traditional low-frequency credentials transmit a fixed identifier, which can make them harder to align with today’s expectations for encrypted and dynamic authentication. Increased credential validation. Traditional proximity systems do not provide the kind of mutual authentication or challenge‑response mechanisms that are increasingly common in newer credential platforms. Better protection from duplication/cloning. Because the credential model is comparatively simple, 125 kHz cards present fewer barriers to duplication or cloning than modern encrypted credentials which are inherently designed to better distinguish authorised users from copied identifies. An opportunity to secure the full path. Many legacy deployments also rely on Wiegand communication between reader and controller, creating a strong case for modernisation to encrypted, supervised protocols that help protect credential data in transit. Keeping the interoperability benefit of Prox. Newer open standard provides the same interoperability benefits while addressing improved security. The opportunity for the front door At the same time, security teams face an expanding threat landscape and compliance requirements A traditional access control upgrade is not just a technology swap. It means new readers at every door, new credentials issued to every employee and contractor, platform reconfiguration and installation labor across a facility that cannot afford to stop. Against that backdrop, the rational choice is often to do nothing. At the same time, security teams face an expanding threat landscape and compliance requirements that increasingly demand encrypted credentials. And with Apple Wallet corporate badges and BLE mobile credentials moving into the mainstream, employees and contractors will soon expect to use their phone as their badge, at least as an option if not the primary means of credential presentation. Four specific friction points keep organisations locked in place long after they know they should move. The logistical bottleneck - Replacing a proximity-based system has traditionally meant doing everything at once: new readers, new credentials, new platform configuration, every employee and contractor rebadged before the cutover date. For a site running 24/7 with extensive staff and rotating contractors, that isn’t just an upgrade. It’s a logistical nightmare requiring a hard shutdown. The rebadging event alone, coordinating hundreds or thousands of people through a credential transition on a fixed timeline, can consume weeks of HR and security operations bandwidth. The Credential Soup - Most logistics organisations are not running one clean credential population. They are running three or four: legacy prox for permanent staff, a different format inherited from an acquisition, a contractor badge system managed by a third party, a mobile pilot that never fully rolled out. None of them talk to each other, and no single reader handles all of them. Frozen Infrastructure - Static readers support only the credential formats they shipped with or have limited format support for updates. When a new vulnerability is disclosed or a new mobile standard is released, the hardware has no path to adapt. The only option is physical replacement, which means another capital project, more installation labour, and the same shutdown risk all over again. The Cyber-Physical Gap - IT departments run zero-trust architectures and encrypt everything on the network. Then the same organisation unlocks its server room with a Wiegand-protocol reader transmitting credentials in plain text. The IT security perimeter ends at the network edge. The physical front door is a different conversation entirely, and often nobody's budget. The way forward: Continuous modernisation of access credentials A continuous modernisation plan is both easier and more cost-effective than a one-time “rip-and-replace” event The answer to the Big Bang problem is not a better-planned Big Bang. It is a fundamentally different approach to access infrastructure that treats modernisation as an ongoing capability rather than a one-time event. A continuous modernisation plan is both easier and more cost-effective than a one-time “rip-and-replace” event. It significantly lowers the labour and logistical costs of rebadging the entire organisation at once and eliminates the need for forced downtime entirely. Instead, organisations upgrade incrementally (by site, by department, or as credentials expire), keeping operations running and spreading costs over time. And with future-proof universal reader technology, the reader stops being a fixed asset and becomes a platform that continues to evolve as needs change. Start with a universal infrastructure The foundation of continuous modernisation is a universal reader that can handle whatever credentials are already in the building (legacy proximity, modern smart cards, mobile credentials) while remaining ready for whatever comes next. As access technologies continue to evolve, support for additional credential formats and security approaches can be added through firmware updates rather than hardware replacement, ensuring a secure and future-proof access system. The burden can further be eased by the use of a universal credential that can support existing formats along with new formats, enabling the credentials to work on existing readers as well as new readers. Let old and new credentials coexist Legacy 125 kHz cards continue to function in parallel until the organisation is ready to retire them With a multi-technology reader in place, the rebadging process becomes a rolling transition rather than a synchronised event. New employees get modern credentials from day one. Existing staff transition as badges are renewed or departments are prioritised. Legacy 125 kHz cards continue to function in parallel until the organisation is ready to retire them. Eventually, 125 kHz support or insecure credential support can be switched off, cleanly and deliberately, via a remote firmware update. That means no forced downtime, and no mass confusion at the turnstiles. This applies equally to secure migration to either modern symmetric credentials (such as HID Seos or LEAF) or emerging asymmetric credentials (such as PKOC, Aliro or LEAF Verified). Secure the whole chain, not just the card Upgrading credentials without addressing the communication layer is only half the job. Moving from Wiegand to OSDP Secure Channel (a bidirectional, AES-128 encrypted protocol) closes the replay attack vulnerability and adds tamper detection between reader and controller. Modern credentials and a secure communication layer together protect the entire authentication chain, from the card or smartphone all the way to the access control platform. This becomes critical when the reader is handling the decryption of a secure credential and then communicating to the panel in clear text. OSDP encrypts this last step of communication, while also offering industry best practices for managing reader devices. Choose infrastructure that doesn't choose for you Interoperability is not just a convenience feature. It is a strategic asset Interoperability is not just a convenience feature. It is a strategic asset. A facility running universal reader infrastructure compatible with most transponder technologies and credential formats (physical and mobile) is insulated from vendor lock-in and the next credential transition. Universal readers also act as merger-and-acquisition insurance: when a company acquires a facility running a different badge system or a contractor arrives with an unfamiliar card format, existing readers can be configured to accept the new credentials from day one. As access technologies and credential standards continue to evolve, organisations with adaptable reader infrastructure will absorb that shift as a firmware update. Those without it will face another capital project. A market in motion: beyond legacy credentials Emerging open standards (which reduce vendor dependency) and widely adopted proprietary platforms are both moving the market toward stronger cryptography. These credentials can be delivered on physical smart cards, mobile devices or both. Organisations selecting reader infrastructure today should ensure it is prepared to support this transition without requiring a hardware swap. Several initiatives are gaining significant traction: LEAF Identity: An interoperable credential framework built on strong symmetric encryption, already deployed across a meaningful number of installations and a proven replacement path for legacy proximity systems LEAF Verified: A next‑generation physical access credential platform built on NXP’s MIFARE DUOX that uses public‑key cryptography to eliminate traditional shared key management and enable interoperable, vendor‑neutral access control. PKOC (Public Key Open Credential): An open, vendor-agnostic credential specification from the Physical Security Interoperability Alliance using asymmetric public key cryptography, in which the private key never leaves the device and a derivative of the public key is the credential Aliro: An open mobile-first credential standard released in February 2026 by the Connectivity Standards Alliance (CSA), the organisation behind the Matter smart home standard. Backed by Apple, Google, Samsung, and 220+ industry members providing native wallet, offline device support and mailbox features on top of asymmetric public key cryptography. HID Seos: A widely deployed proprietary credential platform that continues to drive responsible, large-scale secure symmetric-based encrypted deployments across small to enterprise environments for both card and mobile deployment, including wallet. Security that scales The same principles apply equally to a single site or a logistics operator running 5,000 employees The same principles apply equally to a single site or a logistics operator running 5,000 employees across a dozen sites. Because no single cutover date is required, a large organisation can sequence the migration by site, by department or by credential expiry cycle. The operational risk that makes a traditional upgrade unthinkable at scale becomes manageable when the transition is invisible to the people walking through the doors. The pressure to act is reaching a tipping point. Apple Wallet corporate badges and BLE mobile credentials are arriving in earnest in 2026, as well as asymmetric smart card options. These technologies are rapidly moving from isolated pilots into mainstream enterprise deployment across logistics, manufacturing and production environments. Evolve security infrastructure Organisations that have already invested in universal reader and credential infrastructure that is firmware-updateable and mobile-ready will absorb that shift without a second thought. Those that haven't will face another rip-and-replace decision just as the mobile credential wave hits. Organisations that have already invested in universal reader and credential infrastructure Continuous modernisation is not a one-time project. It is a permanent capability: the ability to evolve security infrastructure at the organisation's own pace, without forced downtime, without mass rebadging events, and without being held hostage to the next credential transition. Organisations that build that capability today are not just solving a security problem. They are future-proofing the way their facilities move. Universal access from ELATEC ELATEC's TWN4 universal readers are built on an agnostic design strategy: multi-technology, multi-frequency, and software-configurable, so organisations are not locked into a single credential technology or vendor. Key capabilities across the TWN4 family: Support for 100+ physical and mobile credentials and 60+ transponder technologies RFID, NFC, and BLE in a single reader platform Software-configurable via the ELATEC DevPack: credential formats, encryption settings, and security protocols can be updated remotely without hardware replacement Supports backward and forward compatibility as new standards emerge Available in a range of form factors for door access, desktop enrollment, OEM integration, and industrial applications
For years, physical security and cybersecurity evolved on parallel tracks. One team managed doors, badges and cameras, while the other handled network access, authentication and logical assets. The systems rarely shared information and, in many organisations, they still do not. That separation is becoming harder to defend now that employees move continuously between physical and logical environments throughout the workday. A single person may badge into a building, access cloud applications, reserve workspaces, connect to operational systems and authenticate into sensitive applications within minutes. Disconnected identity systems Yet many organisations still treat each interaction as a separate identity event managed by different systems with different policies and different visibility. Attackers, with the help of AI, are becoming increasingly adept at exploiting those gaps. According to HID’s 2026 State of Security and Identity Report, identity management is now the top strategic priority for security leaders, with 73% identifying it as a trend shaping their security planning. The report also found that managing multiple disconnected identity systems is now the primary operational challenge for more than half of respondents. This shows that identity is becoming the link between physical security, cybersecurity and operational resilience. Fragmented identity creates operational and security risk The growing convergence between physical and logical environments has raised the stakes considerably Many organisations accumulated identity systems over time rather than designing them as a unified architecture. Access control platforms, visitor management systems, HR provisioning tools, multifactor authentication systems and workplace applications were often deployed independently to solve specific operational needs. Individually, these systems may function well. Together, they often create administrative duplication, overhead and blind spots. A terminated contractor may lose network access immediately while retaining physical access to facilities for days. An employee may require multiple credentials to navigate a single workday. Security teams may need to reconcile disconnected logs across several systems during an investigation. These inefficiencies slow response times and increase operational risk. The growing convergence between physical and logical environments has raised the stakes considerably. Modern attacks increasingly target the connections between systems, particularly where identity validation is inconsistent. HID’s research highlights growing concern around AI-driven credential attacks, biometric spoofing and phishing campaigns designed to exploit fragmented identity environments. This is one reason organisations are reevaluating identity management from the ground up. Converged credentials reduce complexity One of the clearest developments in this evolution is the growing adoption of converged credentials One of the clearest developments in this evolution is the growing adoption of converged credentials, where a single trusted identity is used across both physical and logical environments. This allows one credential to securely support access to buildings, workstations, cloud applications and other enterprise systems. The operational advantages are substantial since security teams gain more consistent governance across environments and IT and facilities teams reduce administrative duplication. Organisations simplify onboarding and offboarding workflows while improving auditability and compliance visibility. Users benefit from a more seamless experience that supports how modern workplaces actually operate. Importantly, converged identity strategies also reduce the number of credentials employees must manage. They are no longer forced to manage separate badges, passwords, tokens and access workflows across disconnected systems. That simplification means employees are less likely to seek workarounds. HID’s 2026 State of Security and Identity Report found that 75% of organisations have either deployed or are actively evaluating physical-logical identity convergence solutions. Mobile credentials are changing expectations Mobile credentials are also reshaping how organisations think about identity management. What began primarily as a convenience initiative has matured into a broader security and operational strategy. HID’s research found that 74% of organisations have already deployed or are actively planning to deploy mobile credentials. Security improvement now ranks ahead of convenience as the primary driver for adoption. Mobile credentials support encrypted communication, biometric authentication and real-time credential lifecycle management. Administrators can issue, revoke or update credentials remotely without requiring physical card replacement. Organisations also gain stronger visibility into credential usage and access patterns. Credential lifecycle management Equally important, mobile identity aligns with broader expectations of the workforce Equally important, mobile identity aligns with broader expectations of the workforce. Employees increasingly expect workplace access experiences to mirror the simplicity of consumer technology, whether they are accessing offices, applications or services. The future is unlikely to be entirely mobile, however. Most organisations are expected to maintain hybrid credential environments for the foreseeable future, combining mobile credentials with physical cards and other identity technologies based on operational needs and user requirements. Biometrics expands beyond MFA Biometric technologies are becoming more central to identity strategies across industries. Historically, biometric technologies were primarily deployed for multifactor authentication and to protect highly secure environments. HID’s research shows that organisations are increasingly adopting biometrics as part of core access control and identity verification workflows. This trend is particularly visible in sectors where identity assurance and operational efficiency are both critical. Healthcare organisations are using biometrics to strengthen patient identification, secure sensitive areas and streamline staff authentication workflows. Higher education institutions are exploring biometric-enabled mobile experiences that support campus access, workspace login and digital services. Transportation operators are deploying facial recognition to accelerate passenger processing while improving identity verification. With broader adoption comes greater scrutiny around privacy, transparency and governance. Organisations are paying closer attention to how biometric data are collected, protected and managed. HID’s report found that privacy and ethical concerns surrounding biometrics rose sharply year over year, reinforcing the importance of encryption, secure architecture and privacy-first design approaches. Physical access is now part of cybersecurity As physical and logical systems converge, every access decision carries more weight As physical and logical systems converge, every access decision carries more weight. The credential used at the door may also support workstation login, cloud application access and other enterprise workflows. That makes the integrity of the entire identity chain more important, from the credential and reader to the systems that manage permissions, events and audits. This is where older access infrastructure becomes a real liability. Legacy cards, weak reader-to-controller communication and disconnected credential systems can undermine even a strong cybersecurity program. If an organisation cannot prove who entered a facility, whether the credential was valid and how that event relates to logical access activity, it is working with partial visibility. Common governance model Converged identity helps close that gap by linking physical and logical access under a common governance model. Organisations can apply more consistent policies, reduce credential fragmentation and accelerate investigations. IT gains stronger assurance that the person accessing systems is tied to the same trusted identity used to enter the building. Security teams gain better context when reviewing access events, anomalies or incidents. This does not require an organisation to replace everything at once. The practical path is phased modernisation: moving away from easily cloned cards, strengthening reader and credential security, improving integration with identity systems and choosing architectures that can evolve as requirements change. Identity is becoming core to enterprise infrastructure. It now supports access control, cybersecurity, compliance, workplace experience and operational continuity. Organisations that treat identity as an infrastructure will be better positioned to reduce risk without adding unnecessary friction for users.
Security beat
Deploying artificial intelligence (AI) tools should be seen as a business initiative rather than a technology initiative, says Martin Soukup, CTO of Solink, a cloud-based video security and data intelligence platform. The approach makes a difference that plays out in practical terms. A technology initiative is tactical and solution-oriented, often solving an isolated problem within a single department's silo. In other words, it might solve just a security problem. In contrast, a business initiative is cross-disciplinary, driven by executive leadership to impact the entire organisation in a measurable way. “Viewing AI tools as a business initiative ensures they adapt to multiple departmental needs and drive high-level strategic growth rather than just fixing a localised technical issue,” says Soukup. AI platform combines video and business systems Demonstrating the value of embracing AI as a business initiative is Solink’s new video intelligence platform Demonstrating the value of embracing AI as a business initiative is Solink’s new video intelligence platform that combines video with business systems to detect threats and send real-time alerts. The capabilities are designed to help security teams operate smarter and more efficiently, supporting the next generation of lean, intelligence-driven security operations centers (SOCs). And benefits of the platform extend beyond security to include other parts of the business. “At the end of the day, video cameras only tell part of the story, much like looking at a 2D shape,” says Soukup. “They capture dimensions and colors, but only from a single perspective, even with powerful AI analysis providing traffic metrics, wait times, product interaction, and compliance logs. The addition of operational data, such as inventory, shipping, labor, and sales data, fills out that shape into 3D, adding critical context.” For example, while a camera simply shows three people standing in a line, and AI data flags that those individuals have been waiting for over five minutes, operational data lets you know also that a cashier has not checked into their shift yet. Combining these data streams gives businesses full situational awareness, turning passive observation into immediate, contextual intervention. AI agents handle repetitive tasks The Solink platform uses AI Agents, which are software that operates autonomously to handle manual, repetitive, or high-volume tasks based on specific instructions and tools. For Solink users, AI Agents unify their existing camera and data source investments into a single automated workflow. “AI Agents transform Solink from a security tool into an operational investment that benefits all departments,” says Soukup. “Modern operational leaders are turning to AI to scale productivity without increasing overhead.” Integrating business intelligence Operations checks compliance, loss prevention investigates theft, and security assesses threats Customers already use Solink to centralise video, integrate business intelligence, and trigger real-world responses like real-world alerts, two-way communication, or smart locks. AI Agents tie these pieces together, analyse the data and identify what matters most, and then take action either without human intervention or with humans in the loop. Businesses currently watch video manually across separate workflows. Operations checks compliance, loss prevention investigates theft, and security assesses threats. However, a human must always watch the footage to get results. Solink AI Agents automate this entire workflow. If an operational event can be seen on camera and matters to the business, a Solink Agent can be integrated to automatically review, assess, and trigger the next step in the workflow across hundreds or thousands of locations simultaneously. Calling all stakeholders to the discussion When discussing applications, stakeholders should include revenue and marketing officers, compliance officers, and line-of-business executives. Agents leverage existing infrastructure by adding an intelligent automation layer that drives efficiency and grows revenue across the entire organisation without large capital investment. Solink AI Agents will not replace employees; they empower lean teams to maximise their existing resources. Job descriptions will shift toward human-in-the-loop workflows where humans and machines collaborate. The AI Agent handles the high volume, filtering out noise and processing data at scale. Human employees set up and guide the Agents, give feedback to improve performance over time, and step in to make final decisions, managing the nuanced situations that require critical thinking, empathy, and deep context. Passive data visualisation In contrast, a Solink AI Agent is deployed with a clear mandate for a specific task, deliverable, or outcome Given the convergence of physical and digital security, AI Agents, not dashboards, are the right unit of enterprise AI deployment. Dashboards typically aggregate data without evaluating the context or importance of the source. Data looks identical whether it comes from 10 sources or 100. In contrast, a Solink AI Agent is deployed with a clear mandate for a specific task, deliverable, or outcome. This approach shifts the focus from passive data visualisation to active intent, creating a direct path of accountability and clear attribution for business results. With dashboards, everyone can see the problem, but nobody owns it. An agent with a mandate either did the job or it did not, and you can audit exactly what it saw and why it acted or did not. Overcoming obstacles to deploy AI agents The primary obstacles to integrating AI Agents into the physical security workflow are change management, building trust, and system interoperability. Physical security requires absolute reliability, which demands rigorous initial configuration to establish trust. Furthermore, Agents are only as effective as the data they can access. Overcoming these hurdles requires comprehensive team training, shifting organisational mindsets, and ensuring seamless integration with existing tools so the Agents have the full context needed to execute tasks accurately and integrate with human workflows seamlessly. Addressing common security challenges Several use cases are driving the deployment of AI Agents among Solink's customers Several use cases are driving the deployment of AI Agents among Solink's customers. Overnight guarding, loss prevention, and store readiness will be the first wave of use cases. These are proven, high-frequency scenarios in which Solink provides pre-built template Agents to address common security challenges out of the box. The second wave of use cases will include highly customisable occupancy tracking, health and safety, and food quality. Pre-built template Agents are coming for these next. In addition, custom, niche operational use cases can be tailored to a specific business environment. Just like hiring a specialised contractor, companies can deploy custom Agents to tackle unique operational challenges rapidly across all locations. Measuring the effectiveness of AI agents The effectiveness of AI Agents can be measured by multiple factors. Core Accuracy, and consistency and accuracy of detections and automated outputs. Business Outcomes delivered, such as reduced inventory loss, reduced fraud, and faster incident resolution. Financial Impact, measured through recovered budget, reduced operational overhead, and increased per-store conversion. There is a perception that AI Agents possess predictive or flawless capabilities, like stopping crime before it happens or operating perfectly in dark, chaotic environments. Not true, says Soukup. AI cannot understand ambiguous requests like "look for suspicious activity." Success requires explicit parameters, tools, and skills, defining what is acceptable, what is unauthorised, and how to handle the gray areas. Another misconception is that Agents need a fundamentally different security model than people. “I run security for this company as well as engineering, and I hold our own Agents to the same standard I would hold a third-party vendor,” says Soukup. “That means least privilege, full audit trails, anomaly detection, random audits, and no action they can't explain after the fact.”
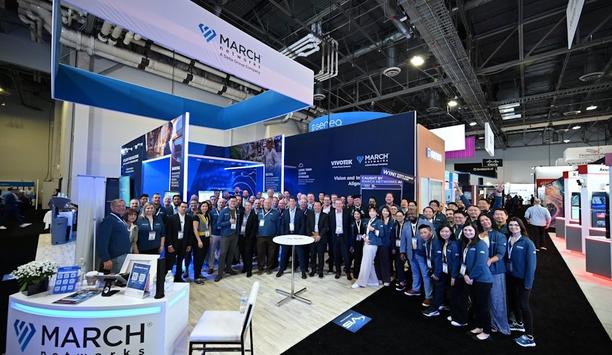
Combining VIVOTEK’s branded video security business with March Networks paves the way for the combined brands to meet customers’ increasing appetite for integrated solutions rather than individual components. The merger brings VIVOTEK's branded video security business together under one operating structure with March Networks’ enterprise-grade video surveillance, AI analytics, and cloud-managed security solutions. Customers now have access to a broader, more integrated portfolio spanning enterprise video management, advanced cameras, edge artificial intelligence (AI), cloud services, recording platforms, and business intelligence, says Net Payne, Chief Sales & Marketing Officer at March Networks and VIVOTEK. Distinct product strategies Given the combined companies, product development, sales, marketing, and customer support can move in step rather than in parallel. March Networks and VIVOTEK were already both part of the Delta Electronics family, but they previously operated as separate businesses with distinct product strategies, teams, and routes to market. March Networks and VIVOTEK announced the merger of their branded video security businesses last spring following Delta Electronics' acquisition of remaining VIVOTEK shares. “Aligning our complementary capabilities lets us innovate faster, simplify engagement, and respond more quickly to a market moving toward AI, cloud and intelligent video,” says Payne. This merger reflects a broader shift across the physical security industry, adds Payne. “Customers no longer see video purely as a tool for reviewing incidents after the fact,” he says. “They expect it to help identify risks earlier, simplify investigations, improve operations, and support better decisions across the organisation.” Cloud video management Meeting customer expectations requires more than bolting AI features onto existing systems Meeting customer expectations requires more than bolting AI features onto existing systems. Rather, it requires cameras, edge intelligence, recording, software, cloud services, and business data working together as one coordinated platform. “By bringing March Networks and VIVOTEK together, we combine deep expertise across the full video technology stack while preserving the relationships, sector knowledge and customer focus both companies have built over many years,” says Payne. “Our goal is to make intelligent video more integrated, scalable, and practical for customers and partners worldwide.” Both entities bring strengths to the combined companies. March Networks brings experience in enterprise software, cloud video management and large-scale deployments; while VIVOTEK brings strength in imaging, camera technology and edge intelligence. Together they seek to ensure more choice when designing systems, a clearer path for future expansion, and technologies that work together more effectively without compromising the reliability, cybersecurity, and support customers expect from both companies. Advantages for channel partners Channel partners gain a broader portfolio to address a wider range of customer requirements, combining components as each deployment demands. Channel partners also benefit from expanded geographic reach, deeper technical expertise, and greater investment in training and enablement. “Importantly, this is designed to be a seamless transition,” says Payne. “Partners keep working with the teams and relationships they already know, while gaining access to new capabilities and certification opportunities. Over time, that alignment should make it easier to design, deploy and support complete solutions.” Because they are established and respected brands, March Networks and VIVOTEK branding will continue to be used. Rebranding is not a goal, and neither identity is being replaced by the other. Coordinated decision-making “The immediate priority is organisational alignment by making it easier for customers and partners to benefit from the combined portfolio,” says Payne. Product branding will continue to reflect the relevant portfolio and market context. As product roadmaps become more closely coordinated, customers can expect greater interoperability and a more cohesive experience, says Payne. Any future branding changes will be managed carefully and communicated clearly. Combining the businesses reduces duplication and enables coordinated decision-making across product strategy, engineering, sales, marketing, operations, and customer support. “Instead of developing capabilities independently, teams can share their expertise, align roadmaps, and direct investment to where it has the greatest customer impact,” says Payne. Combining specialised knowledge globally The combined organisation operates across six continents and more than 75 countries The combined organisation includes more than 300 research and development (R&D) engineers across four Centres of Excellence in Canada, Taiwan, Italy and Poland, thus bringing together a substantial base of specialist knowledge. The unified network also sharpens the ability to prioritise global opportunities, respond to regional needs and bring innovations to market faster. The combined organisation operates across six continents and more than 75 countries, supported by more than 1,100 certified channel partners. That footprint provides greater capacity to support multinational customers while staying responsive to local market needs. Looking ahead, future growth will increasingly come from helping customers turn video into useful, actionable intelligence. “The market is moving beyond conventional surveillance toward solutions combining AI, cloud services, edge processing, video management and operational data — and our new structure brings these together as one connected solution rather than several isolated technologies,” says Payne. Broader technical expertise There will also be closer collaboration among specialists in imaging, hardware, software, analytics, and cloud, which is important given how much customer infrastructure, regulatory, and deployment requirements vary. The companies can support cloud, hybrid, and on-premise environments, giving organisations a practical path toward more intelligent video. More choice comes from bringing together complementary technologies across product groups. Greater scale is achieved through a larger engineering organisation, broader technical expertise and more capacity to invest in innovation. Challenges for the industry at large Looking to the future for the industry at large, the greatest challenge will be managing the rapid growth of AI Looking to the future for the industry at large, the greatest challenge will be managing the rapid growth of AI responsibly, securely and at scale, says Payne. Video systems will generate more data and automate more decisions, but organisations must be able to trust how that intelligence is created, protected, and applied, he adds. “Cybersecurity, privacy, data sovereignty, system interoperability and AI accuracy are more important than ever,” says Payne. Addressing these elements requires expertise across the entire technology stack: from camera and edge processing to recording, cloud infrastructure, video management and analytics. “Together, March Networks and VIVOTEK can coordinate development across all these layers, giving customers flexible architectures that balance innovation with security, transparency and operational control,” says Payne.
The security landscape is undergoing a profound transformation, as evidenced by the innovations showcased at the ISC West Expo 2026. From dismantling of silos between physical and digital security to the ongoing transition to cloud and hybrid platforms, much of the discussion on the show floor was familiar, if somehow more urgent than ever. Clearly the industry is moving toward unified, cloud-native, and highly automated ecosystems. In a series of deep-dive meetings and demonstrations at the recent show, I got a first-hand glimpse of the future of the physical security marketplace. Spoiler alert: The future is now! HID Global: Tearing down the silos HID Global is addressing the long-requested convergence of physical and digital security. Recognising that the industry has historically operated in silos, HID is now leading with a combined implementation team to leverage the power of both sides. HID is supporting the transition by combining its logical and physical security teams to help end users design secure, end-to-end journeys for their employees. By leveraging its massive existing footprint in physical access, HID is uniquely positioned to help organisations upgrade their cybersecurity posture without a total "rip and replace" of their hardware. HID is seeing a surge in demand for converged credentials that unite building access with digital identity. On the digital front, HID has implemented FIDO (Fast Identity Online) and passkeys to replace traditional passwords with more secure, biometric-backed authentication methods. Acre Security: Bridging the gap to the cloud Acre Security previewed a cloud-native video solution, reinforcing its cloud-first security strategyAcre Security is currently consolidating brands, bringing established names like Feenics and AccessIt under a single corporate umbrella. A primary theme for the company at ISC West is the migration of legacy systems to modern infrastructure. To facilitate the transition, they are launching "The Bridge," a technology designed to help on-premise customers transition to the cloud at a pace that suits their operational needs. The company is also expanding its portfolio into video. Attendees at the show received a preview of a new cloud-native video solution slated for release later this year, signaling Acre’s commitment to a holistic, cloud-first security suite. Acoem: Real-time acoustic threat detection With a 35-year foundation in vibration and acoustics—including military sniper detection—Acoem is providing gunshot detection through edge processing. Unlike systems that rely on the cloud and may suffer from latency, Acoem’s technology processes data at the sensor level for instant alerts. Their sensors are engineered for massive outdoor spaces, covering a 500-foot radius (roughly 11 football fields) and can detect high-powered rifle shots from up to half a mile away. The system provides critical intelligence by distinguishing between muzzle blasts and "mach noise" from bullet travel, delivering an audio file to the end-user that maps the location and direction of the threat. They use AI to filter out environmental false positives, such as skateboards hitting metal rails. Alarm.com: The all-in-one dealer ecosystem Beyond hardware, Alarm.com is leveraging AI to streamline the sales process Alarm.com is doubling down on "giving tools to dealers to help them be successful," with a focus on unified commercial solutions. A highlight at ISC West is their new fire communicator, which integrates fire monitoring into their single app, completing what they call the "fourth leg of the stool." The product allows fire systems to benefit from the same real-time customer engagement and push notifications that have long been available for intrusion and video. The key products, such as commercial-grade hardware, are now available for immediate purchase. Beyond hardware, Alarm.com is leveraging AI to streamline the sales process. Their new AI Proposal Builder uses customer meeting notes to automatically generate customised, value-driven sales proposals for dealers. Allegion: A global shift in credentialing Following the acquisition of ELATEC, Allegion is adopting a more global market approach and expanding its OEM business. The company is involved in the development of Aliro, the newly unveiled mobile credentialing standard. Allegion’s strategy is built on versatility: While Aliro serves the burgeoning mobile market, they also offer PKOC for plastic cards, allowing them to provide solutions regardless of the user's preferred credential type. The ELATEC acquisition has effectively filled previous gaps in their use-case portfolio, positioning them as a comprehensive provider for both physical and digital access needs. AtlasIED: Engineering for life safety Transitioning from audio to a fully automated threat detection company, AtlasIED showcased its new IPX line at ISC West. This modular platform uses a single PoE++ port to power various "plug-and-play" modules, allowing for easy system upgrades. Their gun detection technology achieves a 99% confidence rating by "stacking" AI models; it cross-references audio data with infrared signatures to detect muzzle flashes and air quality sensors for particulates. With systems already running in 80% of U.S. international airports, the company maintains 24/7 domestic engineering support to manage these "life-safety adjacent" environments. Axis Communications: Unifying connectivity Axis Communications is advancing network video with 4G/5G surveillance, reducing cabling needs Axis Communications continues to lead in network video, with a new focus on offering surveillance through 4G and 5G networks to eliminate the need for extensive cabling in long-range applications. Axis also introduced several specialised hardware pieces, including the P1486-LE global shutter camera for high-speed traffic monitoring and the Q2802-TE, which integrates thermal and visual monitoring into a single unit. To assist technicians, they launched a new installer app that uses Bluetooth for easier camera pairing and management directly from a mobile device. Axon: De-escalation through enterprise wearables Focusing on frontline safety, Axon is expanding from law enforcement into the enterprise sector with its retail and healthcare-focused body camera. Weighing only 0.25 lb, these cameras are designed to be less intimidating, using colorful designs and acting as a primary de-escalator for aggressive behavior. A clear front display signals when recording is active, striking a balance between safety and a non-intimidating appearance. These devices feature live-streaming and panic alarms that connect workers to a Global Security Operations Center (GSOC). To ensure the footage is legally viable, Axon maintains a rigorous audit trail that authenticates every action recorded. Genetec: The value of the unified platform Genetec is advocating for unified platforms that reduce the time between incident detection and resolution. They argue that AI is becoming a commodity and that the true value lies in unified platforms that reduce the time from incident to resolution. Their approach emphasises the "outcomes" customers need, such as allowing security teams to coalesce around an investigation quickly. Genetec remains a strong supporter of open systems for enterprise customers, ensuring they have the choice to integrate diverse technologies rather than being locked into a manufacturer’s “walled garden.” This flexibility is critical for high-end security environments that require tailored, responsive systems. Johnson Controls: Large-scale enterprise solutions Johnson Controls has made a significant push into the enterprise video market with C-Cure IQ, a standalone VMS designed for major hubs like airports and large campuses. Through a partnership with Scylla, they have integrated 11 advanced analytics—including facial recognition and weapons detection—directly into their cameras. They also showcased new multi-sensor panoramic cameras capable of "stitching" multiple images into a single 360-degree view. While innovating in video, Johnson Controls also confirmed modern upgrades to their intrusion line, including their legacy DSC Neo line. The new DSC PowerSeries Neo 5, a high-end residential and commercial platform, features an all-new user interface and built-in PowerG+. They have also begun shipping the IQ5 family lineup, which is powered by a Qualcomm DragonWing processor. ONVIF: Standardising the future of AI and cloud ONVIF continues to lead the charge in establishing common languages for the security industry. A major focus is their new "Cloud Profile," which enables cameras to connect directly to the cloud through a standardised protocol. They are also expanding into audio standards to ensure IP-based speakers can seamlessly connect to Video Management Systems (VMS). To combat the rise of sophisticated digital manipulation, ONVIF is developing "video signing" standards. ONVIF is actively seeking more diverse enterprise participation to help shape these emerging AI standardsThis feature protects the integrity of video for evidentiary purposes by embedding a digital signature and timestamp directly into the footage at the camera level. Additionally, the organisation has formed an AI Working Group to develop common communication methods for "AI agents" within physical security systems. ONVIF is actively seeking more diverse enterprise participation to help shape these emerging AI standards. Roberto Licari is the new ONVIF Ambassador, seeking to attract new companies (even outside the security sector) to ONVIF as they look to expand their offerings. SwiftConnect: Bridging digital and physical identity SwiftConnect is redefining access control by shifting the focus from physical cards to digital identity. As a cloud-based "connected access network," the platform bridges the gap between IT identity providers (like Okta or Azure AD) and legacy physical access control systems. At the show's Security Experience Center demonstrations, SwiftConnect showcased its ability to integrate mobile credentials within Apple and Google Wallets across multiple technology platforms. By aligning physical security with Zero Trust principles, they ensure that access is governed by the same rigorous standards as digital networks. Their software-centric approach allows for a more seamless employee experience while simplifying the management of complex, multi-site building security. This emphasises a future where the mobile device becomes the primary tool for navigating the physical workspace. Wasabi Technologies: Redefining cloud storage economics With cloud technology becoming a baseline requirement at every booth, Wasabi Technologies highlighted its "hot cloud storage" as a cost-effective alternative to major hyperscalers. Their model claims to be 80% less expensive than competitors, notably removing hidden fees. Wasabi is increasingly bundled at the "back end" of security solutions through partnerships with integrators and end users. A key feature for law enforcement and high-security sectors is their "Object Lock" capability, which ensures that video evidence remains untampered with and immutable during defined retention periods. By providing high-performance storage without the unpredictable costs typically associated with the cloud, Wasabi is positioning itself as the foundational layer for data-heavy video surveillance applications that require long-term, secure retention. Wasabi is positioning itself as the foundational layer for data-heavy video surveillance applications ZKTeco USA: Versatile and integrated access ZKTeco USA showcased a range of integrated solutions, including turnstiles, visitor management, and access control. Their Atlas access control series offers versatility, supporting everything from traditional readers and keypads to QR codes and fingerprint scanning, with the flexibility to operate on-premise or in the cloud. For tight environments, they introduced the Mars 100 turnstile, which features a compact 2x3-foot footprint. They also highlighted the Omni series, an all-in-one standalone reader-controller that manages access, intercom, and visitor functions in a single device. Innovation in portability was evident in their new walk-through metal detectors, which consist of two poles with an 8-hour battery life—ideal for schools and temporary events. While they offer their own Armatura readers, ZKTeco emphasised that their solutions can integrate with other industry leaders to fit diverse customer needs.
Case studies

At the Toronto Zoo, every person on site – whether that’s a keeper, security officer, scientist, or volunteer - shares one vision: create a world where people, wildlife, and wild spaces thrive. Thirty minutes from downtown Toronto lies a 500-acre campus that is home to over 2000 animals across 200 species. Welcoming 1.3 million guests each year, Toronto Zoo is a world-class operation on a mission to connect people, animals, conservation science, and traditional knowledge to fight extinction. When Toronto Zoo Supervisor of Health & Safety Services, Graham Birtles, set out to modernise the Zoo’s legacy access and alarm infrastructure, he discovered that the partner he already trusted for animal enclosure fencing was the same one now leading the way in physical security and access control. World-class operation The Toronto Zoo opened in 1974 with a goal that extended well beyond exhibition. Today, its work spans conservation science, breeding programs for endangered species, community education, and climate advocacy. Its Guardians of Wild program extends that belief outward, inviting staff, guests, and partner organisations to champion wildlife beyond the Zoo’s borders: in policy, community relations, and corporate engagement. “My everyday is somebody else’s once-in-a-lifetime experience,” says Graham. “We want every person who comes through these gates to leave understanding what the Toronto Zoo is about, and what they can personally do to make a change.” Delivering that experience safely for guests, staff, and the animals themselves demanded a security platform fit for the job. Rapid emergency response Before Gallagher Security, the Zoo’s access control and alarm infrastructure had not kept pace with the scale of operations. Mobile alerting was unavailable to officers in the field, credentialling hundreds of seasonal staff required plastic cards that were slow to issue and difficult to track, and there was no integration with the Zoo’s video management system to support rapid emergency response. There was also a unique challenge facing the Zoo team: the electric perimeter fencing around animal enclosures - the secondary layer of protection between the animals and the wider Zoo environment - operated as an entirely separate system, disconnected from the broader infrastructure. Following an animal containment incident that was escalated to security leadership, the need to bridge those two systems became urgent. Graham found the solution at a security trade show, when his integrator walked him toward a familiar orange booth. Higher voltage requirements “I said, I already know Gallagher. They’re my fence people. They’ve been taking care of our fencing systems for over 50 years at the Toronto Zoo.” What Graham didn’t yet know was that Gallagher also delivered enterprise-grade physical security, making Toronto Zoo’s path to world-class operations clear. Working together, Gallagher Security and Gallagher Animal Management designed and implemented an integration between Gallagher Command Centre and the Zoo’s Animal Management energiser systems, enabling real-time communication between animal fencing infrastructure and the security platform for the first time. Higher voltage requirements The implementation required calibration for significantly higher voltage requirements than traditional smaller animal environments, ensuring safe and effective management across large species habitats. The Zoo team worked closely with Gallagher’s experts to configure their setup, and the solution is now fully operational within the orangutan habitat. “Now we can see the voltage of our fences at all times,” says Graham. “We can send alerts to our wildlife care team the moment something touches the hot wire so we can make sure the animals are safe.” When an alert is triggered, integrated CCTV allows the wildlife care team to immediately verify the event and assess the situation before responding; a critical functionality for animal safety. The Zoo’s security needs extend well beyond its animal habitats, and the Gallagher platform has delivered. Persistent administrative challenges Mobile Credentials have addressed one of the most persistent administrative challenges on site. With hundreds of contractors and seasonal catering staff requiring access at any given time, the previous reliance on plastic cards was slow and difficult to manage. Now, time-limited mobile credentials are issued on sign-in and revoked automatically on sign-out, removing the risk of residual access. For officers in the field, Gallagher Mobile Connect removed the need to return to base to manage alarms. Officers maintain full situational awareness from their vehicles around the clock, long after the central control center closes. Further integration with 27 Axis intercoms in high-risk spaces - housing venomous snakes, spiders, and other dangerous species - ensure staff working alone in those environments are never out of reach. Restricting workshop equipment “We can monitor alarms throughout the Zoo; not just for traditional break-and-enter or door-open scenarios. We are monitoring life-safety systems, fire systems, animal conditions, and more,” says Graham. What has distinguished the Toronto Zoo’s deployment is not any single feature, but the broad range of problems the Gallagher platform has been called on to solve. New challenges from across the organisation are allowing Graham and his team to unlock more value from their security system. Whether it is monitoring environmental conditions within animal habitats, restricting workshop equipment to trained operators, or ensuring staff cannot access sensitive areas until their training is verified, the answer has consistently been found within the same platform. Conventional vendor relationship “I like that I can call on the Gallagher team and they will work with us to find a solution,” says Graham. “Gallagher has become a house brand here at the Toronto Zoo. It’s integrated with everything we do,” Graham Birtles, Supervisor of Health & Safety Service. The Zoo’s collaboration with Gallagher has not been a conventional vendor relationship. Graham describes it as a convergence of purpose. “When we partner with organisations such as Gallagher, they become Guardians of Wild,” he says. “Because they help me and the Toronto Zoo accomplish our mission.” The Gallagher platform will play a central role in the Zoo’s next chapter. A new Community Conservation Centre, developed with a local university, will soon bring classrooms, laboratories, and a new otter river habitat into a shared community space; with Command Centre managing access for students, professors, and visiting groups. “Gallagher understands our mission,” says Graham. “They are very helpful, and everything they have put in place for us has worked. The flexibility has been fantastic.” This installation was deployed in partnership with Met-Scan Canada Ltd

Genetec Inc, the pioneer in enterprise physical security software, announces Cairo Bank has successfully deployed the Genetec Security Center platform transforming how the financial institution monitors, manages, and optimises operations across one of Egypt’s largest branch networks. Cairo Bank is one of the largest and oldest financial institutions in Egypt, serving over three million customers through more than 230 branches. The security advancement was driven by new regulatory requirements from the Central Bank of Egypt, alongside Cairo Bank’s broader digital transformation agenda aligned with Egypt Vision 2030. Beyond compliance, the bank needed a scalable operational intelligence foundation to strengthen oversight, improve customer experience, and support long-term expansion and financial inclusion. Necessary operational foundation The implementation unifies video surveillance, access control, and intrusion detection into a single platform, allowing operators to centrally manage more than 6,000 cameras across 122 active branches, with deployment across the full network nearing completion. The platform provides the necessary operational foundation for a centralised Command and Control Room, where operators can monitor branch activity, coordinate response, and support decision-making across the institution. The system also separates operational responsibilities. IT and security teams can monitor device health and system status without accessing sensitive video feeds, supporting strict data governance and privacy requirements. “Unification and scalability were just the starting points. From day one, I knew we wanted functionalities that add value to all aspects of our operations. Security Center delivered everything we wanted in one easy-to-use solution,” said Major General Hesham Tawfiq, Head of Security at Cairo Bank. Enhancing operational consistency Beyond traditional surveillance, the platform introduces automation and analytics capabilities that support both security and operational decision-making across its branch network. These capabilities are now embedded across the entire branch network, helping Cairo Bank strengthen compliance reporting, improve risk detection, and enhance operational consistency at scale. The platform also provides insights into branch activity patterns, customer flow, and operational trends, extending the value of security data beyond incident monitoring while keeping governance and operational control central to the deployment. Existing infrastructure investments Security Center’s open architecture allowed Cairo Bank to integrate best-of-breed hardware while preserving existing infrastructure investments. It also enables the bank to add technologies and expand the deployment over time without standardising on a single hardware provider. “We are honoured to work with a forward-thinking institution like Cairo Bank that continuously seeks new ways to leverage technology,” said Firas Jadalla, Regional Director, Middle East & Africa at Genetec Inc. “By unifying systems, the bank is building a consistent operational foundation for its branch network, allowing it to respond to changing regulatory and operational requirements while retaining control over how its environment evolves.” Providing technical support Integrated Technics, the systems integrator responsible for delivering the project, led the proof of concept, system design and implementation. The company continues to provide technical support and system optimisation as the deployment expands. “The Command and Control Room gives Cairo Bank a real-time operational hub built on Security Center, bringing video surveillance, access control and intrusion detection into a single interface. This enables operators to monitor activity across the branch network, coordinate responses and make faster, more informed decisions,” said Walid Alagamy, CEO of Integrated Technics.

Genetec Inc., the global pioneer in enterprise physical security software, announces that TEPCO Power Grid has deployed Genetec™ Security Center as the foundation for a next-generation physical security platform that supports its broader digital transformation strategy and scales with its growing operational requirements. The platform will centralise management of more than 30,000 cameras and support future innovation across the TEPCO Power Grid network of 1,600 substations and service centers. TEPCO Power Grid manages and operates the transmission and distribution network that delivers electricity from power plants to homes and businesses across the Tokyo metropolitan area. The company is using advanced technologies to improve operational efficiency, strengthen disaster response, and modernise critical infrastructure. Modernising critical infrastructure As its camera network expanded over the years, TEPCO Power Grid needed a platform capable of supporting large-scale camera management, integrating with image analysis technologies, and expanding access to video across a broader range of devices. After evaluating several options, the company selected Genetec Security Center for its functionality, scalability, proven track record, and customisation capabilities through its software development kit. “The response from users has been very positive, and we're already seeing new ideas emerge for how the system can be used across the organisation. Beyond supporting our current operations, we see an opportunity to leverage accumulated video data alongside AI technologies to support future operational and technology initiatives, and we look forward to continuing our collaboration with Genetec,” said Tomoyuki Soma, Group Manager, System Development General Affairs Group, System Development Center, DX Promotion Department, TEPCO Power Grid. Improving operational efficiency TEPCO Power Grid selected Security Center for its scalability and open architecture. The platforms broad camera support allowed the company to bring together camera models from multiple manufacturers into a unified environment, helping preserve existing hardware investments while giving teams room to evolve. The Security Center software development kit also enables the company to customise the system and integrate additional technologies as requirements evolve. Security Center gives TEPCO Power Grid a unified view of its camera network while allowing teams across the region to support sites in their respective areas. Activities such as adding cameras and updating maps, which were previously managed centrally, can now be performed by individual workplaces, helping improve operational efficiency. Digital transformation strategy Authorised personnel can also use the Security Center web app to view video from computers and mobile devices. During an incident or emergency, managers and field teams can remotely assess the situation and coordinate their response. The platform also helps teams identify camera malfunctions across the network, making it easier to locate and address issues TEPCO’s 1,600 geographically dispersed sites. In addition to video management, the company sees potential opportunities to leverage accumulated video data and integrate emerging technologies as operational requirements evolve. The company is also evaluating additional capabilities available within the Security Center platform as part of its longer-term digital transformation strategy.

In a sector where budgets are always a focus of attention, delivering concrete returns to every investment is crucial. By digitalising access, healthcare premises – whether large hospitals or small clinics – can benefit from day one. They can improve staff and patient safety; quickly implement more efficient, time-saving workflows; and painlessly meet compliance demands. Healthcare sites always present complex access challenges. They must be welcoming, accessible public spaces. They often occupy large, sprawling areas; unfamiliar faces and first-time visitors are around every single day. At the same time, these premises inevitably have valuable and/or sensitive assets, including confidential data and medicines, which must be secured. Patients, doctors, nurses and support staff must feel safe. In labs and treatment suites, restricted materials and valuable equipment need both security and a compliant system for logging every access event. This has always been healthcare’s ‘business-as-usual’: it is a complex environment for any security manager. Meeting compliance demands Modern hospitals and clinics, however, now face an extra level of challenges – and opportunities. Their access system may benefit from integration with fire detection, CCTV and other building solutions, for example. With so many temporary and contract workers employed on-site, access is in constant motion. It needs to be tailored to specific and very different needs and, equally, revoked when any time-limited tasks are complete. In case of a security breach, rapid investigation is essential. Tracing and logging access to specific areas may also be a legal requirement, especially with new NIS2 regulations introduced for critical infrastructure, which demand proactive “hybrid” cyber/physical security frameworks for many healthcare premises. Relying on manual or siloed systems to complete these tasks could eat up hours or even days for security and even medical staff. Happily, there is a better way to work. Digital access devices The solution is access digitalisation. Digital access devices and credentials help to keep every hospital user safe. Unauthorised access is minimised because unapproved key copies rarely circulate and lost credentials are cancelled with a click. Employees and equipment are safer because more access points may be digitally secured. Issuing contractors and temporary staff with digital or even mobile credentials can further simplify the granting, amending and revoking of site access. Security teams waste less time handing out and collecting keys. Intelligent, intuitive software helps facilities managers stay in control even while they are off-site. Logging access to specific assets or areas becomes quick and simple: a few clicks rather than the laborious process of keeping manual logs up to date. “Access is such an important part of any holistic approach to safety,” says David Moser, SVP and Head of Digital Access Solutions at ASSA ABLOY Opening Solutions EMEIA. “Digitalising access immediately puts powerful tools in the hands of hospital management, delivering tangible daily benefits to meet security challenges head-on, improving efficiency and regulatory compliance at the same time.” Implementing digital access “There’s now a device to extend existing systems with digital control at almost any access point, whatever building solution is in place. Alternatively, we can equip customers with whole solutions to implement digital access from scratch, without invasive installation. So many efficiency and security benefits are within reach.” Below are three of many real-life examples which illustrate the ways healthcare premises have benefited from digital access beyond the most obvious security and safety aspects. By choosing ASSA ABLOY’s Aperio® wireless locks, integrated natively with an ARD access management solution, Centre Hospitalier Métropole Savoie (CHMS) could issue access rights tailored to individual staff and contractors and implement real-time control, helping to boost site safety. Because Aperio locks are wireless, the hospital introduced more layers of security without incurring excessive installation or operating costs, including for sensitive offices and drug stores. Access point functionality at CHMS now includes real-time management logs and remote door opening. Real-time management logs For convenience, staff now carry one credential programmed with their individual tailored permissions. “Having just a single badge, and not having to carry around heavy keys, has been a major advantage for us,” explains Béatrice Dequidt, Health Executive at CHMS. “We have implemented internal HR management procedures, creating badges that are automatically integrated into ARD's operating software,” adds Alain Gestin, CHMS’s IT Systems Architect. Aperio and ARD maintain compatibility of credentials with the French government’s electronic Health Professional Card (CPS), for added staff and management convenience. Personalised access permissions Hospital MAZ, in Zaragoza, also implemented a new ASSA ABLOY digital solution, SMARTair®, with real-time access functionality. Their online wireless access management system saves security managers’ time because they can implement all changes via the central system in real time, without needing to waste time walking through the hospital. Staff convenience is further enhanced: they now carry a smartcard programmed with their personalised access permissions. Custom-made cards double as employee IDs, so 625 staff and approximately 100 contractors only need to carry one. Their ASSA ABLOY system is also mobile access ready, making it easy for the hospital to issue and manage mobile keys in the future without hardware changes. “Digitalisation presents opportunities for healthcare organisations of every size and type to improve security while they also reduce costs ‘hidden’ in daily workflows,” explains David Moser. Convenient secure access Managing physical keys can impact nursing care, as pharmacy managers at Queen Elizabeth Hospital, Birmingham discovered. An older, mechanical system made it difficult for them to keep track of who held the right key. Searching for that person wasted time. They identified a better solution for convenient secure access to controlled medicines: programmable keys. With their CLIQ programmable key access solution, power to digital and electromechanical locks is supplied by a standard battery inside every key, so no wires are required – making it an ideal retrofit solution for hospital doors, cabinets and mobile drug trolleys. Audit trails for locks and padlocks are available on demand: nurse managers can quickly see who has accessed cabinets or drug trolleys. Key access solution “The message from all nursing staff is that patients are getting medicines much easier and in a more timely fashion,” says Inderjit Singh, Chief Pharmacist at QE Birmingham. “For us, the key return on investment is the quality of service we’re providing.” “Our expertise in access, established over decades, enables us to work with customers to get their access ready for what’s ahead,” adds David Moser. “With ASSA ABLOY, they digitalise with confidence.”

PPLD serves El Paso County across multiple branches — from busy urban libraries to new rural buildings. Its security program, built on systems dating back to the late 1980s, had to keep pace with a fast-growing footprint. “I don’t know that we would have been able to get to the point where we had everything we wanted deployed if we didn’t have tech like this,” said Michael Brantner, Chief Facilities & Security Officer, Pikes Peak Library District. Pikes Peak Library District (PPLD) is one of Colorado Springs’ most-used public institutions, serving the El Paso County community across multiple branches with 780 cameras and more than 150 doors under active monitoring. Their physical security program had been trying to keep pace. Legacy systems dating back to the late 1980s. Cameras and access control systems that didn’t talk to each other. A small team buried under too many alarms. The model was reactive, and it was overdue for a rethink. Legacy security technology The challenge - PPLD’s footprint was growing in a few ways, through new construction and the addition of more rural buildings under its umbrella – and Chief Facilities & Security Officer Michael Brantner needed more visibility across all of the buildings. Combining the systems in place to protect these locations, plus the new ones, required a new approach: bring decades of legacy security technology into a unified, modern operation that could scale alongside the district’s growth. PPLD wanted to centralise the management of the district’s security function, which led Michael to explore the creation of a new security operations center (SOC). “We had a lot of technology that didn’t talk to each other,” Michael said. “We wanted to be able to consolidate it into one place where we can manage what’s happening across our sites.” Consolidate disconnected systems When he started building PPLD’s SOC, the mandate was clear: bring decades of legacy security technology into a unified, modern operation that could scale alongside the district’s growth. But he also needed to consolidate disconnected systems, prove ROI to the C-suite, and staff and train a team that could actually move the program forward. At the time, PPLD’s setup was a patchwork: Cloud-based cameras and access control sitting next to legacy equipment, with no shared view across them Operators who were refreshing screens to see new alarms Panic alerts, door alarms, and intercom calls each requiring a different screen, a different workflow, and a different response Notifications were inconsistent Response times couldn’t be measured No centralised SOC to manage alarms cohesively Residents experiencing homelessness Most incoming alarms generated by PPLD’s ACS were false: held-open doors, cleaning crews, and after-hours trip alarms. But every single alarm still demanded a response from someone on the team, even if there was no safety issue. The complexity was real. PPLD’s branches serve a diverse community that includes families, students, and residents experiencing homelessness across locations with very different security profiles. Some deal with routine access events. Others face behavioural incidents, policy enforcement issues, and higher alarm volumes. Across all of them, public spaces had to stay public, and private staff areas had to stay private. Those boundaries need to be enforced, all day, every day. Access control systems The solution - As Michael stood up PPLD’s new SOC, HiveWatch stood out as a way to centralise the security program and allowed the growing team a single, active view of every incident across every system. The platform connected directly to PPLD’s existing cameras and access control systems. This meant operators were able to view door alarms, access events, video clips, panic alerts, and environmental sensors (including vape and smoke detection) in one single incident list in a web-based browser. Instead of refreshing screens and guessing at what they might have missed, operators could see every active incident and incoming alarm the moment it surfaced and respond from the same place. Killing redundant alerts Alarm deduplication cut volume on day one, killing redundant alerts before they hit an operator. Noisy doors became easy to spot and fix. When specific issues surfaced, like a flood of DHO alarms, for instance, the system helped the SOC adjust alarm timing. That adaptability, tuned to actual door and user behaviour without loosening security, kept the program compliant and cut the alarm load the SOC had to manage. Operators, along with field officers, made use of the mobile app, too. The team’s ability to acknowledge, investigate, and resolve incidents from anywhere in the building was a huge benefit. Security triage stopped being tied to a desk. Response became coordinated, in real time, across every location. Standard operating procedure But the shift went beyond operations. For the first time, PPLD’s leadership had detailed data on its security program: response times, alarm volumes, and incident trends. Michael could walk into a leadership meeting with numbers that proved the program’s value. He could spot which operators were hitting targets, which branches were generating outliers, and where more operator or officer training was needed. “We aren’t just operators staring at cameras anymore. HiveWatch lets us cut through the noise, focus on what matters, and actually expand what our team can do,” said Joe Vickous, SOC Supervisor, Pikes Peak Library District. Single active queue Every shift, PPLD’s operators manage a single active queue. Door forced at a branch. Vape detection in a restroom. Held-open back door after a cleaning crew shift change. An intercom call from a side entrance. All surfaced in one view without screen-refreshing or system-hopping. When an access control alert comes in, the response is immediate. The operator sees the alert with the connected camera feed in the same view, follows the built-in standard operating procedure (SOP), and, if warranted, dispatches the field officer with full context from within the platform. Audible alerts mean the SOC can run HiveWatch in a single tab without sacrificing a full monitor, freeing operators to handle more important work like footage pulls, door testing, and badge creation between incidents. Badge creation between incidents “HiveWatch makes the operators more flexible and makes them more versatile, as well,” Michael said. “They’re able to focus on something else and it will prompt them and say, hey, pay attention. We have to interact. They can check it out, dispatch somebody, and then go back to what they’re doing.” And when something crosses the public-private line, such as a patron drifting into a staff-only corridor, the platform surfaces it in real time. The operator sees it, the field officer responds, and the boundary holds. Public stays public. Private stays private. No guessing. No discovery after the fact. Incidents are caught early, handled according to protocol, and documented with a full record attached. “The biggest benefit for us is having the tool that sorts through the noise and focuses the operators on the notifications that are actually coming in that need attention,” Branter said. Standard operating procedure The results: Median time to acknowledge incidents of 21 seconds and median time to resolve of 28 seconds using HiveWatch. Scaled the SOC from 2 operators to 6 plus a manager, with the platform absorbing the workload increase. Extended the SOC beyond the control room with mobile triage and response for field officers and operators. Equipped leadership with real-time data on acknowledgement and response times, and alarm trends, turning a reactive program into a proactive, measurable one. Positioned the program to absorb 800 additional cameras and access points without proportional headcount growth.

Verkada, a pioneer in physical security and operations, announces that the Miami Dolphins and Hard Rock Stadium adopted its platform to enhance fan safety and security. Hard Rock Stadium's new Verkada deployment unifies video security, access control, guest management, intercoms and alarms into a single, cloud-based platform that enables its team to streamline security operations at the scale and speed that the 65,585-seat venue demands. "As a world-class venue hosting global events year-round, we prioritise solutions that align with the scale and pace of our operations," said Sameer Istafa, Chief Technology Officer for the Miami Dolphins and Hard Rock Stadium. "Verkada's unified platform provides a seamless, connected operating environment that supports our focus on delivering a consistent, elevated experience for our fans at every event." Resource-intensive maintenance costs Verkada's unified platform gives Hard Rock Stadium's team: Faster response during high-pressure moments. Activity-based detection and intelligent alerts provide teams with greater visibility into activity across Hard Rock Stadium, enabling faster, more informed responses when needed. Proactive perimeter coverage. Advanced detection tools enable Hard Rock Stadium to take a proactive approach to monitoring the stadium's exterior and surrounding areas, flagging unusual activity before it escalates. Streamlined access across a large campus. Verkada's cloud-managed access credentials replace physical keys and disconnected badge systems. With all door events logged, Verkada's platform can flag anomalies. Flexibility across a wide range of events. In addition to the Miami Dolphins, Hard Rock Stadium hosts college football games, concerts, and other global events – and each event has a different footprint and different security needs. Verkada enables the Hard Rock Stadium team to tailor protocols event-by-event without new infrastructure. Lower infrastructure costs. Moving onto Verkada's cloud-based platform is expected to save Hard Rock Stadium on time- and resource-intensive maintenance costs, with new features delivered automatically through software updates. Insight into operational efficiency. Visual intelligence from Verkada's platform provides insight into occupancy trends that can enable operations teams to reduce bottlenecks and adjust staffing in real-time. World-class experience "Hard Rock Stadium can swing from hundreds of employees and vendors on a weekday to more than 65,000 fans in a matter of hours," said Filip Kaliszan, co-founder and CEO of Verkada. "Verkada is built to handle this kind of complexity, with one unified platform that keeps pace with an operation that never stays still. We're proud to provide solutions that help keep fans, athletes and entertainers who visit Hard Rock Stadium safe – and to give the team behind these legendary events the tools they need to keep delivering a world-class experience." Video security infrastructure Hard Rock Stadium worked with Castaway Technology and Security (CTS) to support its Verkada deployment and implementation across the campus. CTS used Verkada's Command Connector to bring Hard Rock Stadium's existing video security infrastructure into the new platform during the migration period, ensuring a smooth transition and letting security teams work from Verkada's platform from day one. "Hard Rock Stadium is a marquee venue that demands a security infrastructure to match. Our goal was to help them transition to a more agile and integrated ecosystem. With Verkada, we were able to deliver a truly end-to-end solution that eliminates technical friction, allowing the security team to focus entirely on maintaining a safe, premier experience for every fan," said Craig Bruce, co-founder at CTS.
Round table discussion
Casinos are tasked with monitoring vast gaming floors, cashier cages, and access points. The market for casino security and surveillance demands software and hardware that provide high-definition, multi-angle visual coverage to ensure the integrity of the games and to protect players, staff, and the public. Like other vertical markets for physical security technology, the casino market is undergoing change and facing challenges. We asked our Expert Panel Roundtable: How are new technologies impacting the casino surveillance and security market?
Like other disciplines in the world of corporate security, executive protection is evolving from reactive to proactive. Unlike reactive bodyguards, modern executive protection professionals use a proactive approach focused on risk mitigation, advance planning, and threat intelligence to prevent incidents before they happen. What is the role of technology? We asked our Expert Panel Roundtable: How can physical security technology promote better executive protection?

If AI is the dominant buzzword in the physical security industry, it is the second letter (I for intelligence) that is having the biggest impact. Simply put, intelligence transforms computer systems, including those used for physical security, from rigid, rule-following calculators into adaptable, problem-solving partners to human operators. We asked our Expert Panel Roundtable: What is the changing role of intelligence in physical security?
Products





White papers

Integrated systems enable critical and compliant security for transportation
Download
Access. Intrusion. One estate.
Download
An end user's guide to physical security for data centres
Download
Combining security and networking technologies for a unified solution
Download
What is a universal RFID reader?
Download
Maximising enterprise security systems in the cloud
Download
The power of integration in physical security systems
Download
Preventing loss, securing assets
Download
Using artificial intelligence (AI) to automate physical security systems
Download
Integrating IT & physical security teams
Download
Verkada workplace safety survey
Download
How to create a successful physical security roadmap
Download
5 easy steps to an upgraded video surveillance system
Download
Improving city mobility using connected video technology
Download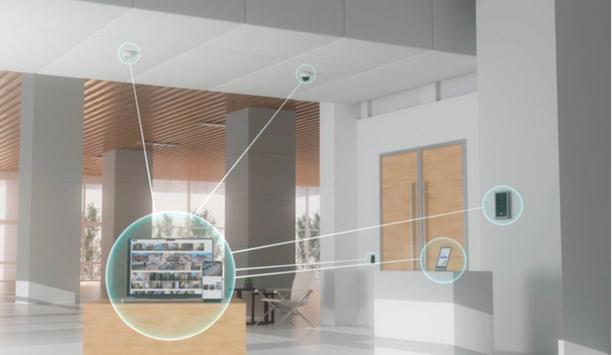
5 ways to strengthen physical security with an integrated system
DownloadVideos


Physical security: Manufacturers & Suppliers

Technology's role in securing banks and financial institutions
Download
Security technologies promote real-time awareness in K-12 schools
Download
Integrated systems enable critical and compliant security for transportation
Download
Modernising physical access control
Download
Access. Intrusion. One estate.
Download