Intrusion detection




News

Inovonics, a foremost provider of wireless solutions for life safety and security applications, is displaying its expanded portfolio of wireless security solutions at GSX 2026 in Expo Suite #28 on the show floor. Featured solutions include the upcoming Inovonics Intrusion Detection System and the sleek, lightweight Duress Card, along with the company’s comprehensive portfolio of wireless transmitters and sensors. Wireless solutions “Inovonics wireless-first solutions deliver higher levels of performance, speed, accuracy, and cost-efficiency for daily security applications and operations,” said Tom Chittenden, President of Inovonics. “Our new Intrusion Detection System and Duress Card being demonstrated here at GSX 2026 are next-generation solutions that combine the best of Inovonics’ proven technologies with new and evolving platforms and capabilities that users and resellers can effectively scale into the future.” Next-generation solutions GSX 2026 attendees can explore Inovonics’ comprehensive portfolio of wireless transmitters and sensors for intrusion detection, environmental monitoring, and panic notification. Built on proven EchoStream® 900 MHz wireless technology, Inovonics’ products provide reliable, long-range communications with the flexibility to support new installations, system expansions, and upgrades. The new Inovonics Duress Card combines a sleek, lightweight design with enhanced panic notification capabilities. Users can activate up to three different alarm conditions from a single device. When paired with integrated security systems leveraging Inovonics’ cloud-based Advanced Location services, the Duress Card also provides location and real-time tracking capabilities to help pinpoint where an emergency is taking place. The Duress Card provides seamless one-to-one integration with most existing systems. Inovonics is also showcasing its upcoming Intrusion Detection System, a wireless-first solution built around the new EN6091 Gateway Mark II panel. Supporting up to 256 zones, the hybrid system combines EchoStream® wireless with cellular, Ethernet, and Wi-Fi communications, cloud-based administration, over-the-air programming and updates, and mobile management. It is designed to simplify installation and ongoing management for new systems, expansions, and takeovers. Visit Inovonics in Expo Suite #28 at GSX 2026 to experience its latest wireless security solutions.
From AI-powered hazard detection and connected factories to fire prevention, smart buildings, and robot demonstrations, Secutech Vietnam 2026 opens today in Hanoi with a focus on technologies that help protect, manage, and operate urban environments and production facilities more effectively. Taking place from 9 – 12 September 2026 at the Friendship Cultural Palace alongside Fire & Safety Vietnam and SMABuilding, the 19th edition will host 480 exhibiting brands from 16 countries and regions across 13,000 sqm of exhibition space. Representing Bulgaria, China, Germany, Hong Kong, India, Japan, Korea, Malaysia, Singapore, Spain, Switzerland, Taiwan, Türkiye, the UAE, the US, and Vietnam, exhibitors will present solutions spanning safety, security, emergency response, industrial automation, ICT infrastructure, and smart building technologies. Digital facility management Commenting on the fair, Ms Regina Tsai, General Manager of Messe Frankfurt (HK) Ltd – Taiwan Branch, said: “This year’s edition reflects how safety and security needs are becoming more closely connected with digital transformation, facility management, and industrial modernisation. Across factories, commercial buildings, public facilities and infrastructure projects, end users are looking for solutions that can improve risk prevention, response efficiency, and daily operations at the same time. By bringing these different technology fields together, Secutech Vietnam gives visitors a clearer view of how systems can be planned and applied in real project settings. It also helps suppliers present their solutions in a way that matches the practical needs of Vietnam’s fast-developing market.” This year’s exhibition will feature a broad mix of international and local suppliers across video surveillance, AI analytics, access control, intrusion detection, network transmission, fire protection, hazard detection, voice evacuation, testing and certification, and digital facility management. Mobile facility management Featured brands include Ajax Systems, AMG Systems, Dahua Wisualarm, Dräger, Hanwha Vision, Hikvision, NAFFCO, Network Optix, Nittan, Securiton, Sony, TOA, TVT, UL and VdS. Software and AI solution providers such as Advancis, Bien Ba, Certis, CSA International, emCT, HTI Group, JAON Inc, Sunggeon Engineering and Ventionex Innovations will also present applications covering hazardous zone monitoring, C2 platforms, identity management, system integration, VMS, AI orchestration, forensic video analytics, construction safety, IoT monitoring and mobile facility management. International participation will be further supported by country and regional showcases, including the Japan Pavilion and Korea Pavilion, which will present fire safety, inspection, emergency response, rescue, PPE and smart safety technologies. Together with specialist exhibitors and certification bodies, these showcases will help visitors compare solutions for local project requirements and safety standards. Supporting digital transformation The 2026 fringe programme will place practical application at the forefront, with forums, workshops, and product presentations covering AI and software, factory automation, hands-on sessions for installers, fire prevention, emergency response, and live technology displays. Key highlights include: AI & Software for Intelligent Industries: Accelerating Vietnam’s Digital Transformation - This business-focused forum will examine how AI, software, cloud, networking, IoT, and intelligent platforms are supporting digital transformation across industrial facilities, commercial buildings and smart cities. The sessions will connect technology providers with end users through discussions on video intelligence, AI data infrastructure, hazard detection, intelligent manufacturing, IT network optimisation, and smart city platforms. SPS Stage Vietnam – Building the Next-Generation Factory: AI, Robotics and Connected Industrial Automation - Co-organised by the Ho Chi Minh City Automation Association, this forum will focus on how AI, robotics, industrial automation, and connected factory technologies are transforming Vietnam’s manufacturing sector. Topics will include AI and robotics in modern manufacturing, the transition from industrial automation to smart manufacturing, and the development of connected factory ecosystems. Tech Stage - Exhibitors will present their latest products, technologies, and solutions through product presentations and live showcases. The platform will give distributors, system integrators, installers, consultants, engineers, project owners, and end users a closer look at new applications across security, fire safety, smart building, AI, and IoT technologies. Industry Installer Workshop - Focused on practical learning, the workshop hosted by Nhà An Toàn will offer product knowledge and skills-based training for installers and industry professionals. Sessions will cover AI-powered video surveillance, intelligent object search, AI-managed switch solutions, fire alarm systems, and robot applications for Vietnamese enterprises, helping participants apply new knowledge in installation and project environments. Fire seminar organised by the Fire Association - Industry representatives will examine the development of Vietnam’s fire prevention, firefighting, rescue, and emergency response sector, with attention to its role in public safety, national security, and social order. The seminar will also consider how fire safety capabilities can support the continued growth of the wider safety and security industries. Dialogue with enterprises and business associations on fire prevention and firefighting - This session will address implementation challenges, regulatory requirements, and emergency preparedness, while encouraging closer public-private communication on improving safety practices across workplaces and facilities. AI & Robotic Display Demo Time - Live demonstrations will give visitors a closer look at intelligent machines, automation equipment, and AI-enabled tools in operation. The area is intended to reveal how these technologies can support tasks such as monitoring, inspection, response, and facility management, while allowing direct exchange with solution providers.

As the pace of progress quickens, organisations face a growing volume of alerts and increasingly sophisticated attacks. Security teams are expected to detect and respond to threats quickly, often with limited resources. This is where an AI-native Security Operations Centre (SOC) becomes essential to improve visibility, detection accuracy, and response times. Alerts rain down, attackers adapt in real time, and defenders are expected to see patterns in the chaos. A SOC is fuelled not just by algorithms but by something far more fundamental: data. In this article, users will learn what kinds of data power an AI-driven SOC, including telemetry, security signals, and contextual intelligence. They will explore how these data streams are processed and enriched, how large language models elevate detection and response, and why the quality of the data can determine whether the SOC hums like a precision engine or sputters under pressure. We will also walk through best practices for building strong data foundations and conclude with how organisations can take the next step. Endpoint detection tools An AI SOC does not rely on a single stream of information. Instead, it thrives on a layered ecosystem of data that, when combined, creates clarity out of noise. Telemetry is the raw pulse of your environment. It includes logs, network flows, endpoint activity, cloud events, and user behaviour data. Every login, file access, process execution, and API call leaves a trace. Telemetry is abundant, continuous, and often overwhelming in its volume. Security signals are what emerge when telemetry is analysed. These include alerts from intrusion detection systems, endpoint detection tools, SIEM correlations, and anomaly detections. Signals are essentially telemetry that has been interpreted through a security lens. Human-readable explanations Contextual data adds meaning to both telemetry and signals. It answers critical questions: Who is the user? What is the asset’s value? Is this behaviour normal for this system? Context includes asset inventories, identity and access information, threat intelligence feeds, vulnerability data, and even business risk profiles. Individually, each layer tells a partial story. Together, they form a narrative that AI can understand, reason about, and act upon. If telemetry is the raw orchestra and signals are the sheet music, large language models are the conductor bringing it all together. AI-driven SOCs increasingly use LLMs to interpret complex, multi-source data in ways that traditional rule-based systems cannot. Instead of relying solely on predefined signatures or rigid correlations, LLMs can understand relationships between events, infer intent, and even generate human-readable explanations. Accessing sensitive data For example, rather than flagging three separate alerts for unusual login activity, file access, and privilege escalation, an AI SOC can stitch these together into a single, coherent incident narrative. It can explain that a compromised account was used to move laterally and access sensitive data, reducing both noise and response time. LLMs also enhance threat hunting by allowing analysts to query systems in natural language. A question like “Show me unusual login patterns for privileged users in the last 24 hours” becomes actionable without complex query syntax. This bridges the gap between human intuition and machine precision. Perhaps most importantly, LLMs enable adaptive learning. They continuously refine detection logic based on new data, emerging threats, and organisational context. This transforms the SOC from a reactive function into a proactive, learning system. Isolated data points The journey from raw data to actionable defence is not magic. It is a carefully orchestrated pipeline where each step adds clarity and value. It begins with data collection, where telemetry is ingested from across endpoints, networks, cloud platforms, and applications. Modern AI SOCs rely on scalable data lakes and streaming architectures to handle this volume without bottlenecks. Next comes normalisation and enrichment. Data from different sources is standardised into a common format and enriched with contextual information such as user roles, asset criticality, and threat intelligence. This step transforms isolated data points into something meaningful. Then comes analysis and correlation. Machine learning models and LLMs analyse patterns, identify anomalies, and correlate events across time and systems. This is where signals are refined and prioritised. Effectiveness of automation Following this is decision-making and automation. AI systems assess the severity and likelihood of threats, triggering automated responses where appropriate. This could include isolating an endpoint, revoking access, or escalating to an analyst with a detailed incident summary. Finally, there is feedback and learning. Every incident, whether a true positive or false alarm, feeds back into the system. This continuous loop improves detection accuracy over time. At every stage, the quality and completeness of data determine the effectiveness of the outcome. An AI SOC is only as intelligent as the data it consumes. Poor data is like feeding distorted notes into that orchestral performance. The result is confusion rather than clarity. Incomplete telemetry can create blind spots where attackers move undetected. Noisy or unfiltered data can overwhelm models, leading to false positives and alert fatigue. Inconsistent data formats can break correlations and reduce the effectiveness of automation. More accurate prioritisation On the other hand, high-quality data enables precision. It allows AI systems to distinguish between benign anomalies and genuine threats. It supports faster investigations, more accurate prioritisation, and more confident decision-making. Consider this question: if your SOC had perfect visibility but imperfect context, would it truly understand what it is seeing? Building strong data foundations is not a one-time task. It is an ongoing discipline that requires both technical and organisational commitment. Start by ensuring comprehensive visibility across the environment. This means integrating telemetry from endpoints, networks, cloud services, and identity systems. Gaps in visibility often become entry points for attackers. Improving model performance Focus on data normalisation and standardisation. Use consistent schemas and formats so that data from different sources can be easily correlated. This reduces friction in analysis and improves model performance. Invest in context enrichment. Maintain accurate asset inventories, classify data sensitivity, and integrate threat intelligence feeds. Context turns raw data into actionable insight. Prioritise data quality management. Regularly audit your data sources for accuracy, completeness, and relevance. Remove redundant or low-value data that adds noise without insight. Implement feedback loops between analysts and AI systems. Human expertise remains essential for refining models, validating detections, and improving outcomes over time. Finally, ensure governance and security of data itself. Sensitive telemetry and contextual information must be protected, with clear policies for access, retention, and compliance. Large language models An AI SOC is not just a security function. It is a data-driven capability that reflects the maturity of an organisation’s digital ecosystem. When data is treated as a strategic asset, security becomes more than defence. It becomes intelligence. Organisations that invest in high-quality data pipelines, contextual enrichment, and AI-driven analysis gain a significant advantage. They move faster, see clearer, and respond smarter. AI-native SOCs are reshaping how organisations defend against cyber threats, but their effectiveness depends on the data that powers them. Telemetry provides the raw inputs, security signals highlight potential issues, and contextual data adds meaning and direction. Together, they enable AI systems, particularly those powered by large language models, to detect, understand, and respond to threats with unprecedented speed and accuracy. Modern security powerhouse The journey from data to defence involves careful collection, enrichment, analysis, and continuous learning. Along the way, the importance of high-quality data cannot be overstated. Without it, even the most advanced AI will struggle to deliver value. If users are looking to transform their SOC into an intelligent, adaptive defence system, the question is not whether to adopt AI, but whether the data is ready. To explore how expert-led, AI-driven approaches can elevate the security operations, consider partnering with Rewterz. Their specialists can help you build the data foundations, integrate advanced AI capabilities, and turn the SOC into a truly modern security powerhouse.
Cyber threats are evolving at a pace that bewilder even seasoned security analysts. Attackers used to be easy to detect; with their reliance on phishing emails riddled with spelling mistakes or predictable malware signatures. Today’s threat actors are harnessing artificial intelligence to automate reconnaissance, generate convincing social engineering campaigns, evade detection, and adapt their attacks in real time. Against this backdrop, many traditional Security Operations Centre, or SOC, are struggling to keep up. Legacy SOC models were designed for a very different threat landscape. They were built around manual investigations, siloed tools, and reactive workflows. While these models once provided a strong defensive foundation, they now resemble medieval castle walls facing a swarm of autonomous drones. Endpoint protection systems In this article, readers will learn how traditional SOCs are structured, why they fall short against AI-driven threats, and how AI-powered SOCs are reshaping modern cyber defence. We will also explore why high-quality data is essential for effective AI security operations and outline best practices for building the kind of data environment that allows AI-driven SOCs to thrive. Traditional SOC is typically built around a layered operational model designed to monitor, detect, investigate, and respond to security incidents. Analysts are often divided into tiers based on skill level and responsibilities. Tier 1 analysts monitor alerts generated by security tools such as SIEM platforms, firewalls, endpoint protection systems, and intrusion detection systems. Their role is to triage alerts, dismiss false positives, and escalate suspicious activity. Tier 2 analysts conduct deeper investigations into escalated incidents, while Tier 3 analysts handle threat hunting, advanced investigations, and incident response. AI-powered cyber threats At first glance, this structure appears logical and organised. However, it has several structural weaknesses that become obvious when facing AI-powered cyber threats. One of the biggest limitations of legacy SOCs is their dependence on manual processes. Human analysts are expected to sift through thousands, sometimes millions, of alerts each day. This creates a dangerous environment where alert fatigue becomes inevitable. Imagine a smoke alarm that goes off every few minutes, but for a non-critical fire. Eventually, people stop reacting with urgency. The same phenomenon occurs in SOC environments. Analysts become overwhelmed by false positives, causing genuine threats to slip through unnoticed. AI-generated phishing campaigns AI-driven attackers exploit this weakness masterfully. Modern malware can generate behaviour that blends into normal activity, avoiding traditional detection methods that rely on static rules or known indicators of compromise. AI-generated phishing campaigns can create highly personalised messages that mimic writing styles, business terminology, and communication patterns with uncanny accuracy. Traditional SOCs also struggle with response speed. Many legacy environments still depend on analysts manually correlating events across multiple disconnected systems. By the time an investigation begins, the attacker may already have escalated privileges, exfiltrated sensitive data, or moved laterally across the network. Probing cloud infrastructure The problem becomes even more severe when attackers use AI to automate their operations. AI-powered threats can rapidly test defences, adapt their behaviour, and exploit vulnerabilities faster than human-led teams can respond. Consider this hypothetical scenario: what happens when an AI-driven attack can rewrite its own malware behaviour every few minutes while simultaneously launching personalised phishing campaigns against employees and probing cloud infrastructure for weaknesses? A traditional SOC would likely spend more time chasing alerts than stopping the actual intrusion. Legacy SOCs also lack contextual awareness. Most conventional detection systems focus on isolated events rather than broader behavioural patterns. An employee logging in from a new location may trigger an alert, but the system may fail to connect that event with unusual data access patterns, suspicious endpoint activity, and abnormal cloud API requests occurring simultaneously. Without context, security teams are left trying to assemble a jigsaw puzzle while pieces keep changing shape. Suspicious activity patterns To defend against AI-driven threats, organisations need to match an attacker’s arsenal and turn to AI. Modern AI-native SOC do not simply bolt machine learning onto existing workflows. They fundamentally transform security operations. AI-powered SOC ingest enormous volumes of telemetry data from endpoints, networks, cloud environments, identity systems, applications, and threat intelligence feeds. Instead of relying solely on predefined rules, they use machine learning models and behavioural analytics to identify anomalies and suspicious activity patterns. These systems continuously learn from the environment, improving their ability to distinguish normal behaviour from malicious activity. This dramatically reduces false positives and allows analysts to focus on genuine threats rather than drowning in alert noise. Threat hunting capabilities Automation also plays a major role. AI-driven SOC can automatically investigate alerts, enrich incidents with contextual data, prioritise risks, and even initiate containment actions without waiting for human intervention. For example, if an endpoint begins exhibiting ransomware-like behaviour, an AI-powered SOC can isolate the device, block malicious processes, revoke compromised credentials, and alert analysts within seconds. Traditional SOC workflows might require multiple manual approvals before taking action. AI-powered SOC also improve threat hunting capabilities. Large Language Models and advanced analytics tools can analyse vast datasets to identify subtle attack patterns that human analysts might overlook. These systems can detect low-and-slow attacks, insider threats, and novel attack techniques that do not match known signatures. Importantly, AI-powered SOC still require skilled analysts. AI is not replacing security professionals. Instead, it acts like an extraordinarily caffeinated research assistant that never sleeps, never blinks, and can process millions of events simultaneously. Abnormal behaviour patterns Modern AI-powered SOC combine several technologies to deliver stronger protection against advanced attackers. SIEM platforms remain important, but they are increasingly enhanced with AI-driven analytics and orchestration capabilities. Security Orchestration, Automation, and Response, or SOAR, platforms automate repetitive tasks and coordinate responses across security tools. Extended Detection and Response, or XDR, platforms unify telemetry from endpoints, networks, email systems, cloud environments, and identity providers to provide broader visibility into threats. Threat intelligence platforms feed AI systems with up-to-date indicators, adversary tactics, and contextual threat information. User and Entity Behaviour Analytics, or UEBA, tools help detect abnormal behaviour patterns that may indicate compromised accounts or insider threats. Generating investigation recommendations Large Language Models are also becoming valuable SOC assistants. They can summarise incidents, generate investigation recommendations, correlate threat intelligence, and assist analysts with faster decision-making. However, even the most advanced AI security tools are only as effective as the data they receive. Data is the oxygen of AI-powered security operations. Poor-quality data leads to inaccurate detections, ineffective models, and dangerous blind spots. AI systems depend on clean, complete, and well-structured telemetry to identify threats accurately. If logs are inconsistent, incomplete, duplicated, or missing key contextual information, the AI models may struggle to distinguish malicious activity from legitimate behaviour. For example, if endpoint telemetry is missing process execution details or cloud logs lack identity context, the SOC may fail to identify lateral movement or credential abuse. Disconnected business systems High-quality data also improves model training. AI systems learn from historical patterns, meaning that inaccurate or poorly labelled data can create biased or unreliable detections. In many organisations, data fragmentation is a major challenge. Security data is often scattered across legacy infrastructure, cloud services, third-party tools, and disconnected business systems. This fragmentation creates visibility gaps that attackers can exploit. Building a strong data foundation requires careful planning and governance. Organisations should begin by centralising telemetry from across the environment into unified data platforms wherever possible. Standardising log formats and ensuring consistent timestamp synchronisation helps improve correlation accuracy. Normalised data allows AI systems to analyse events more effectively across multiple systems. Data enrichment is equally important. Adding contextual information such as asset criticality, user roles, geolocation data, and threat intelligence helps AI models make more informed decisions. Relatively predictable techniques Organisations should also continuously validate data quality. Missing logs, duplicate entries, and ingestion failures can quietly undermine detection capabilities if left unchecked. Retention policies matter as well. AI-powered threat hunting often relies on historical behavioural analysis, meaning organisations need sufficient long-term data storage to identify patterns over time. Finally, collaboration between security, IT, cloud, and data teams is essential. Building an effective AI-driven SOC is not simply a technology upgrade. It is an operational transformation that requires alignment across the organisation. Traditional SOC models were built for an era when cyber threats moved more slowly and attackers relied on relatively predictable techniques. Today’s AI-driven threat landscape is vastly different. Attackers can automate reconnaissance, personalise phishing campaigns, evade traditional detection methods, and adapt attacks in real time. Reducing operational risk Legacy SOC struggle under the weight of manual investigations, alert fatigue, fragmented visibility, and slow response times. In contrast, AI-powered SOC use automation, behavioural analytics, machine learning, and contextual intelligence to detect and respond to threats at machine speed. Yet technology alone is not enough. The effectiveness of an AI-driven SOC depends heavily on the quality of the underlying data. Clean, enriched, and well-governed telemetry enables AI systems to deliver meaningful security insights and reduce operational risk. As cyber threats continue evolving, organisations must rethink how their SOC operate. The future of cyber defence belongs to security operations that can learn, adapt, and respond as quickly as the threats they face. To discover how Rewterz experts can help modernise the SOC capabilities, strengthen the data foundations, and prepare the organisation for AI-driven cyber threats, explore our advanced security operations solutions today.
Expert commentary
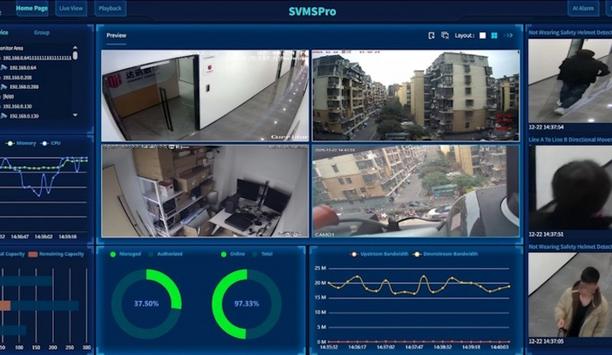
In the modern world of intelligent security, AI cameras and processing units (often called "AI boxes" or "AI servers") are transforming surveillance. They can detect specific behaviours — like someone entering a restricted area, loitering, or a vehicle parking illegally — and send immediate alerts. This represents a significant leap from older systems that merely recorded video for later review. However, a common challenge arises when organisations use devices from multiple manufacturers. Each brand often comes with its own proprietary software, creating a fragmented ecosystem. Unified video management software (VMS) platform Security personnel might need to switch between several different programs to monitor all their cameras. Furthermore, critical evidence — such as video clips triggered by an alarm — is typically stored locally on each device. If that device's storage fills up, new footage can overwrite the old, potentially erasing vital evidence before anyone has a chance to review it. Security personnel might need to switch between several different programs to monitor all their cameras This is where a Unified Video Management Software (VMS) platform becomes indispensable. Acting as a central nervous system, it integrates disparate devices into a cohesive operational framework. Solutions like SVMSPro exemplify this approach, seamlessly merging feeds from diverse AI hardware into a single, intuitive interface. Using SVMSPro as a case study, we can outline the core capabilities of a modern unified AI management platform: Simplified multi-brand management Eliminate the complexity of managing multiple software applications. A unified platform provides a single dashboard to view, control, and manage all AI devices — regardless of manufacturer. This consolidation dramatically streamlines daily operations, reduces training overhead, and provides a holistic view of the entire security infrastructure. Unifying AI surveillance application. Centralised & secure evidence storage Relying on the limited local storage of edge devices is a liability. Critical evidence from alarms is vulnerable to being overwritten and lost. SVMSPro solves this at the source. The moment any connected AI device detects an event — whether it’s intrusion, loitering, or object removal — SVMSPro receives the alert in real time and immediately triggers intelligent actions: Start high-quality alarm-triggered recording, Capture detailed snapshots, Activate PTZ tracking to track the subject automatically, And securely store everything on the centralised SVMSPro platform — not on fragmented front-end devices. This ensures evidence is permanently preserved and readily accessible. Users can swiftly search, review, and retrieve any alarm-related video or image via the web client or desktop application — anytime, anywhere. Illegal parking snapshot. Organised access & smart alerting Effective security is a team effort with tiered responsibilities. A unified platform enables precise, role-based access control. With SVMSPro, administrators can define user roles, create custom accounts, and assign specific video channels — even from different brands — to each operator. A guard may only access parking lot feeds, while a manager receives alerts for perimeter breaches. This granular control enhances operational efficiency, safeguards data privacy, and ensures team focus. Furthermore, real-time alerts can be pushed to mobile apps, guaranteeing immediate notification for the relevant personnel. User management. Integrated data analysis By aggregating data across all connected devices, a unified platform unlocks powerful analytics. It transforms scattered data points into actionable intelligence, generating comprehensive reports on event trends — from peak intrusion times in retail to occupancy heatmaps in large facilities. For instance, by ingesting people-counting data from AI cameras, SVMSPro can produce detailed daily, weekly, monthly, and annual traffic flow reports, supporting informed business and operational decisions. People flow statistics. Conclusion: From fragmented data to cohesive insight A unified management platform is the critical backbone for any multi-brand AI security deployment. It transforms a collection of isolated smart devices into a synchronised, intelligent network. The practical applications are vast: Retail: Combines loss prevention with customer behaviour analytics. Transportation Hubs: Manages vehicle flow and enhances passenger safety. Manufacturing: Monitors compliance in restricted hazardous areas. Smart Cities: Correlates events across districts to provide a unified operational picture for public safety. By centralising control, securing evidence, and delivering intelligent, role-specific alerts, platforms like SVMSPro empower organisations to evolve from simply observing events to understanding and acting upon them with unprecedented speed and clarity.

It took just seven minutes to steal more than $100 million in jewels from the Louvre, in an operation so swift and precise it exposed a deeper flaw in how even the most secure institutions protect what matters most. It's reignited global scrutiny of both physical and digital security, revealing how gaps in coordination can turn sophisticated systems into operational failures. Video intelligence and integrated monitoring Across museums, government facilities, and corporate campuses, video security, analytics, and access control often operate in isolation. In the Louvre’s case, investigators later discovered that the only exterior camera near the Apollo Gallery was pointed west, leaving a point of entry completely unseen. Emerging video intelligence and integrated monitoring technologies show how unified systems could have changed the outcome by preventing the breach altogether or dramatically accelerating the investigation that followed. As threats grow more sophisticated, so must the systems that defend against them. Disciplined system design, measurable performance standards, and continuous validation are what close security gaps. The Louvre incident highlights the industry’s shift toward a new expectation: security systems must not only capture video but understand context, anticipate failure points and maintain reliable performance under real-world conditions. From blind spots to comprehensive awareness Modern systems combine wide dynamic range, infrared and low-light capabilities, and flexible mounting designs Fragmented visibility and weak system governance often create the very conditions that allow sophisticated breaches to occur, where technology can exist, but coordination, oversight, and accountability often fall short. A high-performing perimeter begins with quantifiable coverage targets — field of view, redundancy thresholds, and camera utilisation rates — rather than assumptions about what “should” be visible. Modern systems combine wide dynamic range, infrared and low-light capabilities, and flexible mounting designs to ensure 24-hour situational awareness, even in visually complex environments like the Louvre. When combined with redundant recording and cross-camera correlation, these features ensure that even if one device is compromised or obstructed, others maintain continuous visibility. The result is a perimeter with resilient coverage. Systems should be engineered to maintain visibility under failure conditions, measure performance against predefined KPIs, and surface anomalies automatically. Intelligent detection and real-time response Advanced analytics would have recognised the Louvre intrusion sequence as it unfolded. For instance, detecting the window breach, identifying unauthorised movement, and immediately notifying on-site security. What became a seven-minute heist could instead have been a single, automated alert cycle. These systems interpret what’s happening by reading patterns of movement, environmental cues, and timing. They learn to tell the difference between ordinary activity and something that’s off. Here’s how that works in practice: Unauthorised Access Detection: Spots break-ins or forced entry by recognising sudden motion or environmental changes that don’t match normal use, like a window opening when it shouldn’t. Loitering and Suspicious Behaviour Recognition: Flags individuals lingering too long near restricted areas, giving security teams an early signal to check in before a situation escalates. Abnormal Motion Tracking: Picks up on unusual movements like running, erratic pacing, or carrying hidden objects. Object and Intrusion Differentiation: Knows the difference between a person and a passing shadow, cutting down on false alarms triggered by lighting shifts or reflections. Real-Time Alerts and Escalation: Sends instant notifications to control rooms or mobile devices so teams can coordinate a response within seconds. Together, these capabilities shift security from passive recording to active interpretation, enabling faster decision-making that can be measured, refined, and validated over time. Cybersecurity: The overlooked layer of physical security The foundation of strong digital power lies in protecting the technology that protects everything else Investigators later discovered that the Louvre’s security system was protected by the password: “Louvre.” It’s a reminder that even the most sophisticated physical security system can be undone by the weakest digital link. A state-of-the-art camera system or motion sensor grid can underperform if the software is exposed or improperly managed. The foundation of strong digital governance lies in protecting the technology that protects everything else. Cybersecurity: Defences and system access controls Protection of the security system itself. One of the most fundamental defences is enforcing robust credentials and multi-factor authentication for every user. Many organisations still rely on static passwords or shared logins for convenience, leaving systems vulnerable to both external intrusion and insider misuse. Multi-factor authentication ensures that even if a password is stolen, attackers can’t gain access without a verified secondary factor. Whether that’s a physical token, mobile verification, or biometric check. For security operations centres, where access often extends across multiple facilities or cloud environments, this extra layer can mean the difference between a minor attempt and a full-scale breach. Vetted system administration management. Another equally important defense is the establishment of tiered administrative privileges. Not every user needs full access to system configurations, live feeds, or stored recordings. Limiting permissions based on role and responsibility not only reduces the potential impact of human error but also minimises the damage if an account is compromised. Tiered access also introduces operational accountability, ensuring that sensitive functions, such as disabling cameras or altering detection zones, are limited to authorised personnel and subject to approval of workflows. Secure audit trails. Comprehensive audit logging is what brings digital oversight and accountability full circle. Every access attempt, system change, and data export should be recorded, timestamped, and monitored for anomalies. When properly implemented, audit trails not only support investigations after an incident but can also serve as early warning systems for suspicious behaviour. Automated alerts tied to unusual access patterns or repeated failed login attempts can prevent breaches before they escalate. Integrating these principles aligns physical security with modern cybersecurity standards, ensuring resilience against both external and insider threats. Future designs for resilient security High-profile cases like this year’s security breach at the Louvre rarely stem from a single flaw. They arise from the absence of integrated oversight and collaboration between physical, digital, and operational layers. The path forward lies in a unified model of security that blends comprehensive coverage, intelligent analytics, and secure system governance into a continuous, adaptive framework. When these elements work together, institutions can evolve from reacting to incidents toward anticipating and preventing them. Again, as threats grow more sophisticated, so must the systems that defend against them. Whether protecting cultural landmarks, critical infrastructure, or enterprise environments, the future of video security must anticipate, protect, and build trust by design.
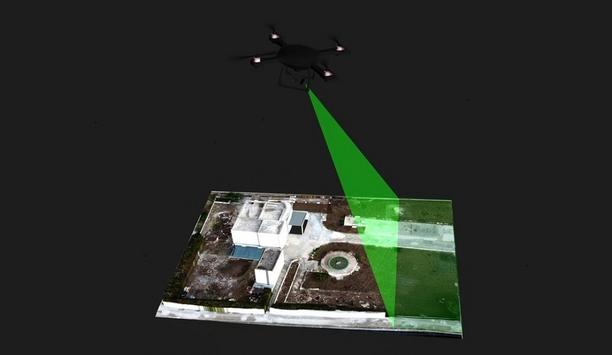
Seven minutes. That’s how long the recent Louvre heist took. In broad daylight, a group of thieves rode up on a construction platform, smashed display cases, stole several historical jewels tied to the Napoleonic dynasty and escaped on scooters before anyone in the control room even realised what was happening. It sounds like a scene straight out of “Mission: Impossible.” Only this time, Tom Cruise wasn’t there. In movies, we often see tight webs of red laser beams guarding treasures, with the hero gracefully sliding between them. Reality, however, is far less cinematic. Most museums still rely on mechanical sensors, simple infrared barriers, cameras and the most fallible component of all: the human eye. But the human eye doesn’t measure space. A camera records an image, but it doesn’t know that a display case has shifted by three centimetres, or that a visitor’s hand just crossed an invisible boundary. That’s where a new kind of perception comes in — LiDAR. From Hollywood fantasy to real-world security Forget the tangled maze of laser beams you’ve seen in films. A modern 128-channel rotating LiDAR fires hundreds of thousands of laser pulses per rotation — and it does this up to 10 times per second. That’s millions of spatial measurements every second, creating an invisible web of light that maps the scene in 3D, without anyone ever noticing. What LiDAR builds is called a point cloud — a live three-dimensional model of the environment. The system constantly compares this “snapshot” with the current scene. If anything changes — a hand moves closer to an artefact, a case is displaced or an object disappears — LiDAR detects it instantly. When technology sees in 3D Pan-tilt-zoom (PTZ) cameras automatically turn to the exact spot and start recording LiDAR technology (such as LidarVision, developed by Hexagon), brings true 3D situational awareness into museums and galleries. It doesn’t just see that someone is moving; it knows where, how fast and in what trajectory. Each detected object is tracked with its precise dimensions, velocity and spatial position. If a visitor steps too close to a protected exhibit, the system triggers an alarm. Pan-tilt-zoom (PTZ) cameras automatically turn to the exact spot and start recording. The operator no longer has to stare at dozens of screens, hoping to catch the right moment. LiDAR data also serves as forensic evidence — allowing investigators to replay the incident as a full 3D reconstruction. They can see exactly how intruders moved, from entry to exit, with centimeter precision. Beyond thieves: Everyday situational awareness LiDAR isn’t just a tool against master criminals. It helps with daily operations, too — recognising when someone lingers suspiciously near a sensitive exhibit, when an unauthorised object enters the room or even when a visitor collapses. The system can trigger a silent alert, notify security staff or automatically redirect nearby cameras. History that never comes back 13 paintings worth more than half a billion dollars vanished from Boston’s Isabella Stewart Gardner Museum Art theft is not a cinematic rarity — it’s a recurring tragedy. In 1990, 13 paintings worth more than half a billion dollars vanished from Boston’s Isabella Stewart Gardner Museum. None have ever been recovered. Even Leonardo da Vinci’s Mona Lisa was stolen from the Louvre in 1911 — though it was miraculously found two years later. That case, however, remains the exception. Thieves often fail to realise that cultural artefacts are not commodities. When they melt them down for gold or strip them for gems, they don’t just destroy value — they erase history. Spatial understanding is the future of security No security system is flawless. But while cameras merely watch, LiDAR understands space. From a single compact device, it monitors the 3D environment in real time, detects anomalies and reacts immediately. Modern security is no longer about higher fences or better cameras. It’s about spatial understanding — knowing what is happening in the room right now. And that’s something even Tom Cruise wouldn’t be able to slip through.
Security beat
2025 was another impactful year for mergers and acquisitions (M&As) in the security industry, which is undergoing an enormous transformation as global pioneers prioritise specialised technology to drive future growth. The year 2025 has been defined by massive corporate reorganisations, most notably Honeywell and Resideo spinning off core divisions to unlock shareholder value. Simultaneously, an aggressive wave of mergers and acquisitions is reshaping the landscape, with giants like ASSA ABLOY and Motorola Solutions absorbing innovators in AI-driven surveillance, cloud-native access control, and identity management. From residential security shifts to critical infrastructure enhancements, this article will summarise how these strategic moves signal a decisive industry pivot toward integrated and intelligent security ecosystems. Resideo to spin off ADI business Resideo Technologies, Inc. announced its intention to separate its ADI Global Distribution business from its Products & Solutions (P&S) business via a tax-free spin-off to shareholders. The separation is expected to be completed in the second half of 2026. P&S will continue as Resideo, a building products manufacturer of residential controls The goal is to unlock value, enhance operational performance, and improve strategic flexibility for both entities. After the separation, P&S will continue as Resideo, a building products manufacturer of residential controls and sensing solutions. ADI will become an independent public company and remain a global wholesale distributor of low-voltage products, including security and audio-visual solutions. Honeywell separates into three companies There are big changes pending at Honeywell, another global security industry company. Honeywell announced plans to separate its Automation and Aerospace businesses into two independent, publicly traded companies following a comprehensive portfolio evaluation. Combined with the previously announced spin-off of Advanced Materials, this strategy will create three distinct industry pioneers. The Automation and Aerospace separation is targeted for completion in the second half of 2026 as a tax-free transaction for shareholders. The largest portion of Honeywell’s traditional security business (cameras, access control, and fire safety) sits within the Building Automation segment of the new Honeywell Automation company. This unit includes products from recent major acquisitions, such as LenelS2. SimpliSafe’s new chapter SimpliSafe has agreed to be acquired by private equity firm GTCR from Hellman & Friedman SimpliSafe has agreed to be acquired by private equity firm GTCR from Hellman & Friedman, another private equity firm. As the third largest U.S. residential security provider, SimpliSafe will continue under the leadership of the current CEO, while its founders remain significant investors. GTCR, an experienced security industry investor, intends to support the company’s expansion and continued innovation in AI-powered, DIY home protection. This marks a new chapter in SimpliSafe’s mission to provide professional monitoring without long-term contracts. SimpliSafe is GTCR’s fifth investment in the security alarm industry, including prior investments in residential-focused security companies SecurityLink and Protection1, along with commercial-focused security companies HSM and Everon. Motorola grows technology portfolio Motorola Solutions grew its portfolio through acquisitions in 2025. The industry giant strategically expanded its safety and security ecosystem through the acquisition of four specialised technology firms. The company acquired Blue Eye to integrate AI-driven remote video monitoring and 24/7 security operations into its threat detection workflows. To support frontline workers, Motorola added Theatro’s voice-powered communication platform, which complements existing mobile and video technologies. Motorola further bolster its public safety capabilities with the acquisition of RapidDeploy, a cloud-native Next Generation 911 provider that offers real-time caller mapping and data analytics to accelerate emergency responses. Motorola also agreed to acquire InVisit to enhance its Avigilon Alta suite with cloud-based visitor management, streamlining guest registration and blocklist screening for enterprise security. These acquisitions aim to unify detection, communication, and response across various sectors, including retail, healthcare, and critical infrastructure. Allied sells majority stake in AMAG Allied Universal sold a majority stake in AMAG Technology to Shore Rock Partners In December, Allied Universal sold a majority stake in AMAG Technology to Shore Rock Partners. Shore Rock is a growth investor focused on critical infrastructure, with strategic backing from BellTower Partners. Allied Universal will retain a significant minority share. The sale is intended to allow 54-year-old AMAG, which provides integrated access control, identity, guest, and video management solutions, to operate independently from Allied Universal's services-based model for long-term growth. Shore Rock's plan is to invest in advancing AMAG's product line and customer relationships. With this transaction, David Sullivan, AMAG's President, will become CEO. Everon acquires ADT multifamily segment Commercial security provider Everon announced in September that it had entered into a definitive agreement to acquire the business-to-business (B2B) multifamily segment from ADT. This acquisition is a strategic extension that expands Everon's reach in the valuable multifamily market. It will allow the company to offer a more comprehensive portfolio of tailored solutions, including access control, video surveillance, and self-guided tour capabilities. Everon's CEO states that the deal enables them to help property owners and managers increase net operating income and improve operational efficiency. Dormakaba acquires TANlock and Avant-Garde Dormakaba, a global provider of access solutions, acquired TANlock GmbH in July Dormakaba, a global provider of access solutions, acquired TANlock GmbH in July. TANlock is a German firm specialising in innovative high-security access solutions for data centers and other critical infrastructure. The acquisition strengthens Dormakaba’s presence in the data center market. TANlock's intelligent system provides enhanced server cabinet security using electromechanical rack locks and various authentication modules. This solution is scalable, future-proof, and can be integrated into existing IT infrastructures for both retrofits and new installations. Dormakaba also agreed to acquire Indiana-based Avant-Garde Systems Inc. to strengthen its North American entrance control portfolio. This move bolsters Dormakaba’s presence in high-growth sectors like airports and data centers. Acre acquires REKS for AI Recent M&A activity also reflects the growing importance of artificial intelligence. For example, Acre Security acquired REKS, a purpose-built generative AI solution designed to transform access control, allowing professionals to use natural language queries for instant data insights. Integrated into Acre’s cloud-native ecosystem, this AI-powered platform prioritises data privacy while streamlining operations. Led by a new AI Development Team, Acre plans to expand these capabilities into intrusion detection and visitor management. Two acquisitions for Allegion Global security provider Allegion, through one of its subsidiaries, completed the acquisition of ELATEC Global security provider Allegion, through one of its subsidiaries, completed the acquisition of ELATEC, a manufacturer of security and access technology, specialising in RFID credentials and readers solutions designed in Germany and sold globally. ELATEC’s portfolio of readers leverages their internally developed software stack and ensures compatibility with nearly 100 credential types, making the company a pioneer in interoperability, which aligns well with Allegion’s partner-of-choice strategy. Allegion, also through one of its subsidiaries, acquired Brisant Secure Limited, a security hardware provider in the United Kingdom. Senstar acquires Blickfeld for LiDAR sensors Senstar Technologies Corporation has agreed to acquire Blickfeld, a specialist in 3D LiDAR sensors and software. Expected to close in Q1 2026, the acquisition integrates Blickfeld’s hardware into Senstar’s advanced security ecosystem. This strategic move expands Senstar’s addressable market into volume monitoring and traffic applications while enhancing its AI-powered situational awareness capabilities. Following the transaction, Blickfeld will operate largely independently as a subsidiary. ASSA ABLOY continues acquisition spree Global giant ASSA ABLOY was probably the most active company in the M&A market in 2025 Global giant ASSA ABLOY was probably the most active company in the M&A market in 2025, demonstrating aggressive market growth, strategically reinforcing its core business, and expanding its technological footprint across the global security marketplace. The acquisitions delivered on the company's strategy to strengthen its position in mature markets by integrating complementary products and solutions. A major theme for ASSA ABLOY was the enhancement of the door and perimeter security portfolio, particularly in the Americas. This effort included acquiring US-based Metal Products Inc. (MPI) for custom-made hollow metal doors and frames and International Door Products (IDP) for fire-rated steel door frames, both in the fall. Earlier in the year, ASSA ABLOY gained a stronger presence in Central Canada with the addition of Wallace & Wallace and Wallace Perimeter Security, a manufacturer, distributor, and installer of perimeter fencing, door, and gate solutions. The Entrance Systems Division also saw expansion with the acquisition of Belgium’s Kingspan Door Components, a manufacturer of sectional door panels. Furthermore, Door System, a Danish manufacturer of high-quality fire-rated doors, was signed for acquisition in the spring. Cloud-based platform ASSA ABLOY also made significant moves in electronic and access control solutions. Early 2025 saw two key acquisitions: Uhlmann & Zacher, a German supplier of access control handles and knobs, and InVue, a US-based provider of connected asset protection and access control solutions. Reinforcing this segment, SiteOwl, a pioneering cloud-based platform for physical security lifecycle management, was acquired in the summer. The spring acquisition of Pedestal PRO, a US manufacturer of access control pedestals and mounting solutions, further strengthens the electromechanical offerings in the Americas. ASSA ABLOY bolstered its capabilities in remote care technology with Germany’s TeleAlarm Group in late spring. HID Global expands in 2025 HID Global, a subsidiary of ASSA ABLOY, was also active on the M&A front in 2025 HID Global, a subsidiary of ASSA ABLOY, was also active on the M&A front in 2025, aggressively driving the convergence of physical and digital identity solutions and signaling a clear roadmap for security professionals. HID's move to purchase Vancouver-based IDmelon, announced in the autumn of 2025, targets the critical need for robust logical access control. IDmelon’s proprietary software platform transforms everyday identifiers, including existing physical credentials, smartphones, or biometrics, directly into enterprise-level FIDO (Fast IDentity Online) security keys. This approach streamlines an organisation’s transition to phishing-resistant, passwordless multi-factor authentication (MFA) and minimises the need for disruptive changes by integrating physical and digital access into a single, cohesive solution. Safer patient experience Separate from its focus on digital access, HID also bolstered its Identification Technologies Business Area by acquiring the Calmell Group. Calmell is a long-established manufacturer specialising in smart cards, smart paper, and magnetic tickets for the public transportation sector. This addition is expected to expand HID’s footprint and relevance in global public transportation ecosystems, allowing the Barcelona-headquartered firm to leverage HID’s core expertise in digital credentials to drive future-proof solutions for seamless mobility. Also, HID acquired Intelligent Observation to expand its Healthcare Real-Time Location Systems (RTLS) portfolio. Intelligent Observation provides a platform to reduce hospital-acquired infections (HAIs) by tracking hand hygiene compliance. The system uses wearable Near-Field Magnetic Induction (NFMI) devices and a cloud-based SaaS dashboard. This technology records and reports if healthcare workers sanitize appropriately, providing granular compliance data to administrators to enable a safer patient experience.
AI has the potential to enhance the usability of traditionally complex access control and physical security systems. The application of AI (artificial intelligence) within access control is still relatively new, but rapid advancements in generative AI are already transforming how security systems operate. acre security is driving the deployment of generative AI in access control through its acquisition of REKS earlier this year. REKS is a purpose-built generative AI solution designed specifically for acre’s access control platform. Unlike generic AI tools, REKS understands both system and security-specific terminology, allowing users to ask natural-language questions like, “Show me all access denied events at a specific location,” and receive instant results. AI workflows and AI agents “We're starting to see how AI workflows and AI agents, that leverage language models, can potentially be used in conjunction with access control to create new, automated processes around false alarm reduction, system configuration, report generation, data analysis, threat detection, and in-system customer support,” says Adam Groom, Director of Business Development, AI Development Team, acre security. “We expect AI-driven capabilities to evolve rapidly, but the full range of benefits will depend on continued development and real-world application,” he adds. Integrate AI-driven capabilities acre’s ability to integrate AI-driven capabilities across the company’s product portfolio positions The best way to think of REKS is as an acre access control expert you can talk to, says Groom. “As AI adoption grows in security, REKS will expand its capabilities, making access control more usable and more efficient.” Groom says acre’s ability to integrate AI-driven capabilities across the company’s product portfolio positions the company as a pioneer in next-generation physical security. “These features will add long-term value by enhancing usability and operational insights across various segments,” says Groom. “Work is already under way to incorporate REKS into acre access control, and we’ll evaluate other integration opportunities in the future.” REKS' AI capabilities According to acre, REKS simplifies daily operations, automating routine tasks, and delivering real-time, actionable intelligence. With REKS' AI capabilities, users can interact with the system to retrieve more detailed insights and actionable information from their acre access control system. “This eliminates the need for complex reports, navigating drop-down menus, or manually reviewing logs,” says Groom. “It significantly enhances efficiency and usability for security professionals.” Enhancing productivity and customer satisfaction Key concern is ensuring that system configuration, enactment, and servicing remain within their scope For integrators, the key concern is ensuring that system configuration, implementation, and servicing remain within their scope of expertise. With REKS, that doesn’t change — but the process becomes significantly faster and more efficient. Instead of manually configuring every panel, input, and output — a traditionally time-consuming task — REKS enables integrators to use natural language commands to streamline setup and adjustments, says Groom. This eliminates tedious steps and dramatically improves operational efficiency, allowing integrators to deploy and fine-tune systems with greater speed and accuracy, ultimately enhancing both productivity and customer satisfaction, he adds. Cloud-enabled ecosystems “We are committed to helping organisations modernise their security infrastructure by transitioning from legacy systems to cloud-enabled ecosystems at their own pace — ensuring minimal disruption while maximising value,” says Groom. “By integrating AI-driven capabilities, we enhance usability and deliver deeper operational insights across all segments.” “Security’s future isn’t about forcing change — it’s about empowering choice,” adds Groom. “Whether staying on-prem, migrating to the cloud, or adopting a hybrid model, we plan to provide a seamless, zero-disruption transition, prioritising interoperability, automation, and security at every stage.” Generic AI tools AI must be purpose-built for security applications because security demands precision, reliability, and context-aware decision-making, which only focused AI offerings like REKS bring to the table, says Groom. In contrast, generic AI tools, like ChatGPT, are designed to perform a wide variety of tasks, like how humans can learn and do many different things. Instead, purpose-built AI is built to do just one specific function. “REKS adds specially designed artificial intelligence to our access control solutions to enhance both intelligence gathering and the user experience,” says Groom. New applications in access control The integration of generative AI into acre's access control platforms and their broader portfolio A new AI development team will lead AI initiatives at acre, driving the integration of generative AI into acre's access control platforms and their broader portfolio. This team will seek to push boundaries in applying AI to new applications in access control, intrusion detection, and beyond, empowering security professionals to interact with their systems in a smarter, more intuitive way. But don’t worry, AI will not take the human element out of security entirely. AI human capabilities “The reality is that AI will improve upon human capabilities because it is a versatile tool that supports and strengthens security operations, not a replacement for human decision-making,” comments Groom. “It helps operators process large amounts of data quickly and detect patterns that might be missed otherwise.” Rather than removing the human element, AI allows security teams to work more efficiently by automating repetitive tasks and providing actionable data, enabling professionals to focus on critical responsibilities. {##Poll1743085396 - What is the biggest challenge you face with your current access control system?##}
Big news on the mergers and acquisitions (M&A) front is closing out 2024, a year in which several shifts changed the face of the physical security manufacturer community. Announced in December, German giant Bosch Group is selling its Building Technologies division’s product business for security and communications technology to the European investment firm Triton. Bosch division selling to Triton The transaction encompasses three business units – Video, Access and Intrusion, and Communication – and thus the entire product business of Bosch Building Technologies that was offered for sale. All 4,300 associates employed in these units at more than 90 locations worldwide will be taken over. The transaction reflects a growing confidence in the security market among private equity companies such as Triton, Becklar, and Volaris. Sharing best practices Acre Security and Bosch will remain independent, standalone companies under Triton’s ownership Acre Security, previously acquired by Triton, has benefited from Triton’s strategic guidance and expertise, according to the company, which is confident Bosch will experience the same level of support and opportunity to thrive. Acre Security and Bosch will remain independent, standalone companies under Triton’s ownership, but will benefit from the potential to collaborate and share best practices as part of the broader Triton portfolio. Resideo acquires Snap One Earlier in 2024, there were other large M&A transactions. In the spring, Resideo Technologies, Inc., a manufacturer and distributor of technology-driven products and solutions, agreed to acquire Snap One Holdings Corp., a provider of smart-living products, services, and software to professional integrators. The transaction is valued at $1.4 billion, inclusive of net debt. Upon closing, Snap One becomes part of Resideo's ADI Global Distribution business. Honeywell buys Carrier’s Access Solutions In late 2023, Honeywell announced plans to enhance and strengthen its building automation capabilities with the acquisition of Carrier Global Corporation’s Global Access Solutions business for $4.95 billion, in an all-cash transaction. The acquisition, which played out through 2024, includes both hardware and software solutions, adding three respected brands to Honeywell’s portfolio with a focus on life safety and digital access solutions. Acquired brands include LenelS2, commercial and enterprise access solutions; Onity electronic locks; and Supra cloud-based electronic real estate lock boxes. Hirsch reemerges as an iconic brand The Identiv sale was originally announced in April, subject to regulatory approval Identiv announced plans to sell its physical security business and assets to Vitaprotech, the security solutions provider that also acquired British manufacturer, TDSI, in 2019. The Identiv sale was originally announced in April, subject to regulatory approval. As a result of the sale, Hirsch, a global security technology pioneer advancing physical security, video intelligence, cybersecurity, and digital identification solutions, announces the relaunch of its iconic brand and strengthened focus on the industry’s most complete high-security, end-to-end platform. Ease of use security solutions The move seeks to reposition Hirsch as the global pioneer in physical security, video intelligence, and identity solutions, protecting everything from small enterprises to critical national infrastructure. With a 43-year-strong foundation in the industry, Hirsch’s mission has always been empowering a secure, connected world, combining government-grade high security with ease of use. Milestone and Arcules unite Effective July 1, 2024, global video technology company Milestone Systems announced its merger with the cloud-based video surveillance solutions provider, Arcules. Both companies are owned by Japanese multinational Canon Inc. Based in Irvine, Calif., Arcules was spun off from Milestone in 2017. The merger brings together Milestone and Arcules’ best-in-class capabilities within video management software (VMS), video analytics, and video surveillance as a service (VSaaS), providing a complete video technology offering. More M&A stories in 2024 In other M&A moves in 2024, cloud-based workforce management software provider Synerion USA Inc. acquired cloud-based video surveillance and access control solutions platform Qumulex Inc. Also, the global pioneer in airspace awareness and security, Dedrone, became part of the public safety and technology company Axon. The acquisition unites two companies with a shared mission to improve public safety and national security by staying ahead of persistent and escalating threats, enabling faster, more effective responses and ultimately protecting more lives in more places.
Case studies

Genetec Inc, the pioneer in enterprise physical security software, announces Cairo Bank has successfully deployed the Genetec Security Center platform transforming how the financial institution monitors, manages, and optimises operations across one of Egypt’s largest branch networks. Cairo Bank is one of the largest and oldest financial institutions in Egypt, serving over three million customers through more than 230 branches. The security advancement was driven by new regulatory requirements from the Central Bank of Egypt, alongside Cairo Bank’s broader digital transformation agenda aligned with Egypt Vision 2030. Beyond compliance, the bank needed a scalable operational intelligence foundation to strengthen oversight, improve customer experience, and support long-term expansion and financial inclusion. Necessary operational foundation The implementation unifies video surveillance, access control, and intrusion detection into a single platform, allowing operators to centrally manage more than 6,000 cameras across 122 active branches, with deployment across the full network nearing completion. The platform provides the necessary operational foundation for a centralised Command and Control Room, where operators can monitor branch activity, coordinate response, and support decision-making across the institution. The system also separates operational responsibilities. IT and security teams can monitor device health and system status without accessing sensitive video feeds, supporting strict data governance and privacy requirements. “Unification and scalability were just the starting points. From day one, I knew we wanted functionalities that add value to all aspects of our operations. Security Center delivered everything we wanted in one easy-to-use solution,” said Major General Hesham Tawfiq, Head of Security at Cairo Bank. Enhancing operational consistency Beyond traditional surveillance, the platform introduces automation and analytics capabilities that support both security and operational decision-making across its branch network. These capabilities are now embedded across the entire branch network, helping Cairo Bank strengthen compliance reporting, improve risk detection, and enhance operational consistency at scale. The platform also provides insights into branch activity patterns, customer flow, and operational trends, extending the value of security data beyond incident monitoring while keeping governance and operational control central to the deployment. Existing infrastructure investments Security Center’s open architecture allowed Cairo Bank to integrate best-of-breed hardware while preserving existing infrastructure investments. It also enables the bank to add technologies and expand the deployment over time without standardising on a single hardware provider. “We are honoured to work with a forward-thinking institution like Cairo Bank that continuously seeks new ways to leverage technology,” said Firas Jadalla, Regional Director, Middle East & Africa at Genetec Inc. “By unifying systems, the bank is building a consistent operational foundation for its branch network, allowing it to respond to changing regulatory and operational requirements while retaining control over how its environment evolves.” Providing technical support Integrated Technics, the systems integrator responsible for delivering the project, led the proof of concept, system design and implementation. The company continues to provide technical support and system optimisation as the deployment expands. “The Command and Control Room gives Cairo Bank a real-time operational hub built on Security Center, bringing video surveillance, access control and intrusion detection into a single interface. This enables operators to monitor activity across the branch network, coordinate responses and make faster, more informed decisions,” said Walid Alagamy, CEO of Integrated Technics.

Introduction - Lightkeepers of Henry County is a grassroots nonprofit organisation based in New Castle, Indiana. It began informally in 2020 with a community vigil, where organisers realised that local residents wanted more activities centred on culture, diversity, and understanding. Lightkeepers became a registered 501(c)(3) nonprofit in 2023 and soon afterward acquired its own building. Guided by its core values of equity, education, diversity, and empathy, Lightkeepers aims to provide a safe place where everyone in the community feels appreciated and has a sense of belonging. Its programs focus on marginalised communities, including low-income residents, people with disabilities, and the LGBTQIA+ community. The organisation hosted the first Juneteenth celebration in Henry County, organises New Castle Pride, and runs food and blanket drives, festivals, and community meetings. Following historic flooding in the area, it is also hosting home damage assessments for affected residents. Limited police patrols The challenge - Lightkeepers is based in the former Westminster Community Center, a two-story cement building that has long been a staple of the neighbourhood. Over the years, it has served as an elementary school, a community center with after-school programs and classrooms, and most recently a food pantry. The building includes a large gym, several ground-floor rooms, an upstairs kitchen, classroom area, and offices, and an attached garage. Before Lightkeepers took it over, the building had been largely vacant, opening for only a few hours, two days a week, for food distribution. It is located in a low-income area with limited police patrols, and the parking lot was so poorly lit that the team repaired the light themselves. A city park directly behind the building had become a meeting place for illegal and unsafe activity. Limited police patrols Today, the building is in use throughout the day. With no set opening hours, it hosts fundraisers, community meetings, training sessions, birthday parties, and baby showers, with anywhere from four to more than 120 people inside at any one time. Festivals and other events also take place in the parking lot. During summer 2026, Lightkeepers partnered with fellow nonprofit Live Coalition to run the Hangout Hub, a weekday program offering activities and free meals for children aged 10 and over. Lightkeepers needed a way to protect the building and its contents, and to keep children and visitors safe while they were on-site. Board members, who often come and go outside of normal hours, needed to see what was happening in the building and parking lot before arriving or leaving. As an older building with boiler heating, the property was also at risk from problems that could go unnoticed when nobody was there. “After we acquired the building, we knew that we would need to be able to watch what we had, because of the neighbourhood it’s in. We definitely needed some sort of security, and we wanted safety for the kids in the gym,” says Mary Nicholson Tait, President, Lightkeepers of Henry County. Monitored intrusion detection The solution -Lightkeepers worked with 3xLOGIC and SONITROL to install video surveillance and monitored intrusion detection across the building, parking lot, and perimeter. The system was completed in 2024. A mix of 3xLOGIC indoor and outdoor cameras watches the building inside and out. A 360-degree camera mounted in the center of the gym ceiling gives full visibility of the space, while a camera in the entrance lobby covers the main entry point. Outside, cameras cover each side of the building, including edge-based deep learning cameras that, if required, can detect people and vehicles and identify details such as vehicle make, model, and colour. Deep learning analytics A 3xLOGIC VISIX 5MP InterACT camera on the front of the building overlooks the parking lot. The camera combines high-quality video with edge-based deep learning analytics and built-in deterrence features, including sirens, white or red and blue lights, two-way audio for talk-down, and custom messaging. Its analytics can detect loitering, intrusion, and vehicles in prohibited areas, with real-time alerts allowing potential incidents to be addressed early. SONITROL’s patented audio intrusion sensors inside the building provide 24/7 monitored intrusion detection. When a sensor is triggered, SONITROL operators can listen in to verify activity and dispatch police when required. Allowing potential incidents Mary can view live footage remotely using the 3xLOGIC mobile app on her phone and access the cameras from a desktop workstation in her office at the building. The SONITROL app, meanwhile, may be used on-site to arm and disarm the alarm system. “I’ve got the desktop set up in my office at the building, so if we have activities in the gym, we don’t have to go down and see what’s going on. We can just click on the camera and see what’s happening,” explains Mary. Monitored intrusion detection Results gained - Since installation, Lightkeepers can see what’s going on at the building from anywhere. Mary regularly uses the mobile app to keep an eye on the parking lot, and because the team does not keep regular business hours, board members can check the cameras before heading out to their cars at night. “We’ve got a lot of women on our board, and we’re over there at all hours. It’s nice for everybody to be able to see what they’re about to walk into before they leave the building,” says Mary. Late one Sunday night, an intruder forced their way in through the gym door. SONITROL’s monitored intrusion detection picked up the activity, operators called Mary, and police were dispatched. Officers were at the building before Mary, who lives five minutes away, could get there. The intruder fled without taking anything. Low winter temperatures In another incident, during unusually low winter temperatures, copper pipes in the building burst. SONITROL’s sensors detected the noise and alerted the team, and Mary checked the lobby camera on the 3xLOGIC mobile app, where she saw water coming out of the room. This meant the team could get someone to the building quickly and limit the damage. No repainting or structural repairs were needed, and no fittings needed to be thrown away. “Had it not been for the security system, we would not have known about the flooding. I was able to look from my app and see there was water, and we were able to get over there and take care of the problem. It saved us a lot of money in repairs and made a huge difference,” explains Mary. Deter nuisance activity The cameras, the repaired light, and the extra activity on-site have helped deter nuisance activity in the wider area, so the park behind the building is now somewhere local children can play. Residents across the street have welcomed the cameras, reporting fewer people coming into their yards and a decrease in illegal activity. “We were afraid they were going to be so mad at us because there were cameras over here. It was completely the opposite. The neighbours were really happy that they could see the cameras, because it provided safety for their properties. They actually thanked us,” Mary concludes. Additional camera coverage Future plans - Lightkeepers is preparing to partner with the Boys and Girls Club to deliver after-school programs from the building, to bring more young people on-site regularly. The organisation is also working with its integrator to assess additional camera coverage and to make full use of the InterACT camera’s siren, talk-down, and custom alarm features to actively deter unwanted activity in the parking lot.

Gozoki, a French family-owned company and pioneer in the freshly prepared meals market (Maison Briau, Maison Tino and other brands), has taken the step of investing to secure its industrial sites. At its facilities in Agen, the company now benefits from a state-of-the-art video surveillance system deployed by specialist integrator SDP, using Hanwha Vision hardware and software solutions. Production sites in the food manufacturing sector face stringent requirements for security, access control and traceability. Protecting staff, preventing intrusions, monitoring logistics flows and securing sensitive areas all present significant challenges. Present significant challenges As part of its ongoing commitment to improving its infrastructure, Gozoki began modernising its surveillance system in 2025 to enhance reliability, accuracy and responsiveness. “We needed a system capable of operating 24/7 in a demanding environment while delivering outstanding image quality. The Hanwha Vision solution meets these requirements perfectly,” says Nicolas Jeannesson, buildings and energy manager at Gozoki. To deliver the project, Gozoki selected SDP, a company renowned for its expertise in integrating electronic security solutions. SDP carried out the site survey, designed the network architecture, installed the equipment and completed its advanced configuration. The objective was to deliver a robust, scalable solution perfectly suited to the demands of a challenging industrial environment. “Our role is to provide a turnkey solution that is reliable and built to last. Hanwha Vision cameras enable us to deliver high levels of performance while simplifying maintenance,” says Pierre Albanese, managing director of SDP. Video analytics capabilities The cameras SDP and Gozoki chose to install were Hanwha Vision’s, and were selected for their exceptional image quality, even in challenging conditions, thanks to high-resolution sensors and WDR technologies. Advanced video analytics capabilities that enable intrusion detection, intelligent management of sensitive areas, and behavioural analysis, were also key features that Gozoki required. The reliability and durability of Hanwha Vision’s cameras are essential in industrial environments that are subject to fluctuations in temperature, humidity or lighting, such as Gozoki’s sites. Enhanced cybersecurity - a critical factor in preventing the risk of cyber attacks on connected systems - was also a vital element of the project’s requirements. The installed cameras cover all strategic areas, including vehicle entrances, loading bays, storage areas, internal traffic routes and external perimeters. “The integrated video analytics allow us to go far beyond simple monitoring. We now have a decision-support tool capable of anticipating risk situations,” adds Nicolas Jeannesson of Gozoki. Future regulatory requirements With the planned deployment of nearly 200 cameras across multiple sites around Agen, Gozoki now benefits from a modern video surveillance system that supports the company’s growth while meeting current and future regulatory requirements. “This project perfectly illustrates our commitment to supporting our customers over the long term with reliable, scalable technologies,” concludes Pierre Albanese. Together, SDP and Hanwha Vision delivered Gozoki a cohesive, high-performance and scalable solution, providing a clear, centralised view of security across its facilities.

Genetec Inc., the global pioneer in enterprise physical security software, announces that Lincoln County Schools (LCS) in North Carolina has modernised its district-wide security infrastructure using Genetec™ Security Center, unifying video surveillance, access control, and intrusion systems across its schools and support facilities. Lincoln County Schools serves over 11,000 students across 23 schools, including 13 elementary schools, four middle schools, four high schools, a technology school, and an alternative school. Four additional buildings support district-wide services such as school nutrition, transportation, and maintenance. As its existing security technology began showing its age, the district set out to modernise its systems. Human resources database “Genetec™ Security Center offered us a great option,” said Steven Hoyle, Chief Technology Officer for Lincoln County Schools. “We have the features we need in one solution that’s easy to use and fits our budget.” At the top of LCS’s requirements was an open, unified security platform. The district wanted the flexibility to reuse existing video and access control hardware while upgrading devices as needed. It also sought to manage video, access control, and intrusion systems within a single solution and to connect other school systems, including the human resources database, to improve process automation. Access control systems LCS began upgrading its high schools’ video surveillance and access control systems, now unified as one in Genetec Security Center. They also added Radionix intrusion detection. When complete, hundreds of cameras, doors, and intrusion sensors across district buildings will be connected to the Genetec open architecture platform. This has also allowed the district to retain much of its existing hardware and to migrate to newer devices at its own pace. “Genetec™ Security Center supports a wide range of third-party technologies, and that’s been a huge bonus for us,” explained Hoyle. “We have the freedom to keep some existing hardware, upgrade to newer devices, and integrate other business systems. This helps us find the right balance between enhancing security and managing costs. And we can do it at our own pace, taking our time to re-evaluate needs and make decisions from there.” Reducing false alarms LCS has also digitised processes by connecting Microsoft Active Directory and its Radionix intrusion detection system within Security Center. With Active Directory integration, cardholder privileges are automatically assigned based on job role and location. When employees join or leave the district, door and system access is activated or deactivated automatically. Synchronising cardholders with the intrusion detection system has reduced false alarms. “In the past, intrusion alarms would sometimes be activated when someone was still in the building, resulting in many false alarms,” said Hoyle. “Now, staff can badge in during set hours, and the intrusion system is automatically armed or disarmed. We’re seeing far fewer false alarms and fewer calls to law enforcement and our administrators.” As upgrades continue, Lincoln County Schools is working with Genetec to expand capabilities and connect additional systems to support faster, more coordinated communication across the district.
Round table discussion

Access control, video surveillance, and intrusion detection systems evolved largely independently in the physical security industry. Integrating those systems to the benefit of an enterprise's overall security has traditionally fallen on security integrators working in cooperation with manufacturers. However, today's market has also evolved to include companies that provide "unified platforms,” bringing together various disparate security systems and functions under a single, centralised management interface. We asked our Expert Panel Roundtable: What are the advantages of installing physical security systems as a unified platform?

A software platform designed to centralise and manage various physical security systems within an organisation used to be called a PSIM (physical security information management) system. Generally speaking, however, the PSIM term has fallen out of favour because the systems were seen as expensive and difficult to manage. The phrase has been replaced by command-and-control, referring to software that combines access control, video surveillance, intrusion detection, and other systems into a unified platform. It’s a ripe area for innovation in the physical security space. We asked this week’s Expert Panel Roundtable: What’s new in command-and-control systems, and what is the impact?

There is no shortage of threats facing security professionals, including some that are new and emerging. Understanding various new threats allows individuals and organisations to take proactive steps to protect themselves, but the first step is to identify what those threats are. Early detection of threats can minimise the impact of a successful attack, whatever the vulnerability at issue. We asked this week’s Expert Panel Roundtable: What new and emerging threats will physical security professionals need to be prepared for in the future?
Products






White papers

Access. Intrusion. One estate.
Download
Security technologies promote real-time awareness in K-12 schools
Download
Precision and intelligence: LiDAR's role in modern security ecosystems
Download
The top 4 reasons to upgrade physical security with the Cloud
Download
11 advantages of a combined system for access control and intrusion
Download
Optimise your business with analytics and AI
Download
How end-to-end video security solutions can help your organisation with social distancing
Download
Schooling the market on education security
Download
How to catch shoplifters with thermal imaging
Download
What Do I Need to Know to Successfully Deploy Mobile Access?
Download


Intrusion detection: Manufacturers & Suppliers
- Bosch Intrusion detection
- Dahua Technology Intrusion detection
- OPTEX Intrusion detection
- Hikvision Intrusion detection
- DSC Intrusion detection
- Honeywell Security Intrusion detection
- Climax Technology Intrusion detection
- Visonic Intrusion detection
- Vanderbilt Intrusion detection
- Senstar Intrusion detection
- Pyronix Intrusion detection
- NetworX Intrusion detection
- Verkada Intrusion detection
- RISCO Group Intrusion detection
- Texecom Intrusion detection
- Software House Intrusion detection
- Axis Communications Intrusion detection
- Ajax Intrusion detection
- Gallagher Intrusion detection
- Enforcer Intrusion detection


