Institute security - News

As artificial intelligence, geopolitical tensions and emerging quantum computing capabilities reshape the global cyber threat landscape, organisations are rethinking how they protect critical infrastructure, safeguard digital assets and prepare for the emerging cyber risks. GISEC Global 2026, the biggest and most influential cybersecurity event in the MENA, organised by inD, will bring together governments, critical infrastructure operators, technology innovators and cybersecurity leaders at Du...

Allied Universal®, the world’s pioneer security and facility services provider, announces that Charles Orgbon, Jr. has joined the company as vice president of corporate security. Orgbon will support the company’s sales and growth initiatives leveraging his law enforcement experience, industry expertise and professional relationships to identify opportunities and strengthen client engagement. He joins Allied Universal following a distinguished career with the Federal Bureau of In...
Johnson Controls, a global pioneer in thermal management, mission-critical building systems, energy efficiency, and decarbonisation, is returning to exhibit at Global Security Exchange (GSX) 2026 in Atlanta from Sept. 14-16. At Booth 1633, Johnson Controls will showcase new innovations and Managed Services designed to help organisations improve visibility across facilities, accelerate incident response, strengthen operational resilience and maintain continuity across increasingly connected and m...

Gallagher Security is strengthening its leadership bench across the Americas as the business continues a clear growth trajectory, with more than 30 percent growth forecast for the current financial year across the region. “Planning for strategic expansion has been a key focus for our team this year. We are incredibly excited about the opportunity ahead, and it is crucial that we set our teams up for success - not just in capability, but in the culture we build along the way," says Matt Bu...

The pace of technological progress is best described as relentless. Cyber attacks have evolved from opportunistic strikes into highly automated, intelligent campaigns that move at faster than ever. Traditional security operations centres, built for a slower and more predictable threat landscape, are struggling to keep up. This is where the AI-native Security Operations Centre (SOC) enters the scene, not as a luxury, but as a necessity. An AI-native SOC reimagines security operations from the gr...
Security operations centres of the past were pictured as quiet control room filled with blinking dashboards with constant surveillance from human analysts. Today, cyber security teams utilise high-speed decision engines; constantly interpreting signals, filtering noise, and responding to threats that evolve by the minute. In this environment, terms like AI SOC, SIEM, and SOAR are often used interchangeably, yet each plays a distinct role. In this article, users will learn what sets these three...
As the pace of progress quickens, organisations face a growing volume of alerts and increasingly sophisticated attacks. Security teams are expected to detect and respond to threats quickly, often with limited resources. This is where an AI-native Security Operations Centre (SOC) becomes essential to improve visibility, detection accuracy, and response times. Alerts rain down, attackers adapt in real time, and defenders are expected to see patterns in the chaos. A SOC is fuelled not just by algor...
Cyber threats are evolving at a pace that bewilder even seasoned security analysts. Attackers used to be easy to detect; with their reliance on phishing emails riddled with spelling mistakes or predictable malware signatures. Today’s threat actors are harnessing artificial intelligence to automate reconnaissance, generate convincing social engineering campaigns, evade detection, and adapt their attacks in real time. Against this backdrop, many traditional Security Operations Centre, or SOC...
Cybersecurity teams face a difficult reality. Organisations are collecting more security data than ever before, yet many still struggle to detect threats quickly, respond efficiently, or keep pace with increasingly sophisticated attacks. Traditional Security Operations Centre (SOC), once considered the backbone of enterprise defence, are under pressure from alert overload, analyst burnout, and attackers who now use automation and artificial intelligence themselves. As a result, AI-driven SOC is...
Cybersecurity teams are experiencing a shift in their scope of work. Attack surfaces are expanding, threat actors are becoming more sophisticated, and the speed of modern attacks is outpacing traditional security operations. At the same time, organisations are facing off a spike in alerts, struggling with analyst burnout, and dealing with an ongoing shortage of skilled cybersecurity professionals. Against this backdrop, Artificial Intelligence has emerged as one of the most transformative techn...
Cybersecurity operations are evolving at the speed of a fibre-optic lightning storm. Security teams are dealing with cyberattacks, increasingly complex IT environments, and a flood of alerts that can bury analysts beneath digital noise. In response, many organisations are turning to AI-powered Security Operations Centre (SOC) to improve threat detection, automate response processes, and strengthen resilience. Yet one important question remains: can AI-powered SOC meet strict regulatory and comp...

Matrix has been conferred with the FIST Awards 2026 in the category - Product of the Year Access Control (Vehicle and Pedestrian) - organised by the Fire and Security Association of India (FSAI). The recognition was presented at the awards ceremony held at the Jio World Convention Centre, Mumbai. Connected operational environment For Matrix, the recognition represents the outcome of practices developed and strengthened consistently over the years. At the core of these practices is complete ow...
Pressure is increasing on modern Security Operations Centre (SOC). Cyber threats are growing in volume, sophistication, and speed, while security teams face increasing workloads, talent shortages, and alert fatigue. Many SOC analysts spend a significant portion of their day investigating alerts that ultimately turn out to be false positives, leaving less time to focus on genuine threats. Artificial intelligence (AI) is helping organisations address this challenge by transforming one of the most...

NETSCOUT®, a provider of observability, AIOps, cybersecurity, and DDoS attack protection solutions, expands its data platform to provide the trusted operational context required to build the foundation for enterprise AI. The NETSCOUT data platform observes digital interactions, converts packets into high-fidelity, compact, contextualised evidence in real time, and curates that evidence at scale for observability, service assurance, cybersecurity, and AI. This addresses a growing barrier to...

Artificial intelligence is transforming the global cybersecurity landscape, strengthening cyber defences while simultaneously enabling faster, more sophisticated attacks. According to the World Economic Forum's Global Cybersecurity Outlook 2026, 94% of organisations expect AI to be the biggest driver of cybersecurity change over the coming year, while 87% identify AI-related vulnerabilities as the fastest-growing cyber risk. Against this backdrop, GISEC Global 2026, organised by inD, a joint ve...

Mercury Security, a pioneer in open architecture access control hardware and a HID brand, announces its Mercury S4 I/O Module family. The new generation of intelligent modules is designed to help organisations modernise and expand physical access control infrastructure, building on the infrastructure they already have in place. As organisations expand facilities, adopt cloud and mobile technologies, and respond to evolving cybersecurity requirements, many are also looking for ways to modernise...

Suprema, a pioneer in intelligent access control and physical security solutions, will showcase BioStation 3, its best-selling biometric terminal to date, and debut its newest flagship terminal, BioStation 3 Max, in India for the first time, at the Fire & Security India Expo (FSIE) 2026. Suprema will also present its access control platforms, BioStar X and BioStar Air. The event will take place September 3–5, 2026, at the Jio World Convention Centre in Mumbai, where Suprema will exhibi...
To meet the challenge of detecting, investigating and responding to increasingly quick threats, organisations are investing in advanced security technologies that can strengthen their security operations and improve resilience against cyber attacks. Two technologies that are often discussed together are Extended Detection and Response (XDR) and AI-powered Security Operations Centres (AI SOCs). While both play critical roles in modern cyber defence, they serve different purposes and deliver valu...
Attackers are using automation, artificial intelligence, and increasingly sophisticated techniques to evade traditional security controls, turning malicious actors into a moving target for security teams. In this environment, organisations can no longer rely solely on reactive security measures that respond to threats after they have already caused damage. Instead, they need proactive security operations that actively search for hidden threats before they escalate into major incidents. This is...
Traditional security tools generate enormous volumes of alerts, making it increasingly difficult for Security Operations Centre (SOC) teams to distinguish genuine threats from harmless activity. As organisations face growing attack surfaces and increasingly complex IT environments, effective threat detection has become one of the most important capabilities in modern cyber security. Detection engineering has emerged as a critical discipline that enables organisations to identify malicious activ...

Cyber threats are becoming faster, more sophisticated, and increasingly difficult to detect using traditional security operations alone. As organisations adopt AI-powered Security Operations Centre (AI SOC), measuring success requires more than simply counting alerts or incidents. The real value of an AI SOC lies in how effectively it improves detection, accelerates response, enhances analyst productivity, and strengthens business resilience. In this article, you will learn which AI SOC metrics...

Matrix Comsec, a technology company delivering enterprise-grade solutions in security and telecommunications, has been recognised among Gujarat's Top 50 SMEs and named a winner in the Best Manufacturing SMEs category at the inaugural Top 50 SME Awards - Gujarat, an initiative of Axis Bank and India SME Forum. For Matrix, the recognition is not the culmination of a single initiative. It acknowledges an operating philosophy built over time: create original technology, retain ownership across the...

inforcer, a provider of Microsoft 365 multi-tenant management software for Managed Service Providers (MSPs), has announces the general availability of its Threat Detection and Response solution, inforcer TDR. Built specifically for MSPs, inforcer TDR goes beyond traditional identity detection to reduce noise, rapidly identify threats, automate breach containment, and continually strengthen protection across every Microsoft 365 tenant. Providing consistent feedback Chief Product Officer at inf...

RecFaces, a global developer of enterprise-grade facial biometric software, will participate in FIRE & SECURITY INDIA EXPO 2026 (FSIE 2026), taking place September 3–5 at Jio World Convention Centre in Mumbai, India. Visitors will be able to meet the RecFaces team and explore three of the company’s flagship products — Id-Time, Id-Guard and Id-Gate — at the stand of its partner, Startologic Technologies (A9). At FSIE 2026, RecFaces will demonstrate how facial biometri...

Iris ID, announces its successful completion of its SOC 2 examination as of October 24, 2025. The SOC 2 audit was conducted by A-LIGN, the provider in cybersecurity compliance trusted by more than 4,000 global organisations to help mitigate cybersecurity risks. Mitigating cybersecurity risks Established by the American Institute of Certified Public Accountants (AICPA), the SOC 2 examination is designed for organisations of any size, regardless of industry and scope, to ensure the personal ass...
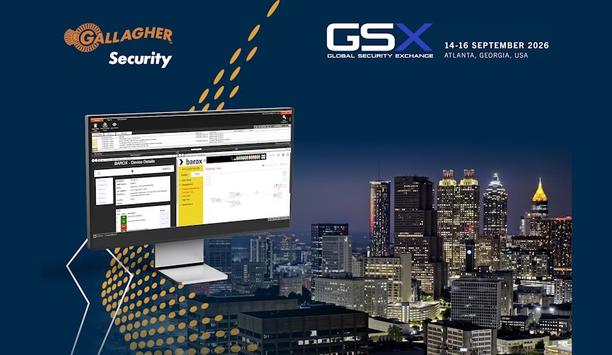
Showcasing the power of partnerships, barox and Gallagher will highlight their joint value proposition at GSX, booth #3433, 14-16 September, Georgia World Congress Center, Atlanta. Revealing seamless integration with Gallagher Security’s award-winning Command Centre site management platform, at the show, a range of barox Ethernet switches will demonstrate how an unparalleled level of monitoring and diagnostics capability can be achieved in just a single integrated platform, covering every...

BuzzFeed, Inc. is one of the most recognisable names in digital media, with 500+ employees, a newsroom and operations across Los Angeles and New York, and a brand built on being fast, scrappy, and ahead of the curve. Their physical security program was trying to keep pace. BuzzFeed was spending more on physical security, not technology, to manage security. In-person guards. Long shifts. Weekend coverage. Manual paper reports. The model was expensive. It wasn’t scalable. And it was overdue...
Cribl, the AI Platform for Telemetry, announces it has acquired technology assets from Radiant Security’s AI-native security operations centre product including intellectual property to autonomously triage, investigate, and resolve security alerts. With this acquisition, Cribl moves further into security and is adapting this AI SOC technology to run as an application on its telemetry data platform, giving security teams peace of mind that AI is making high-quality decisions over the right...

DigiCert, a global pioneer in intelligent trust, today announced the speaker lineup for its third annual World Quantum Readiness Day, taking place virtually on September 17, 2026. Bringing together experts from across cryptography, cybersecurity, and technology, the event will focus on how organisations can move from quantum readiness planning to action. This year’s theme, “From Blueprint to Build,” covers practical approaches to PQC migration, changes in global regulations an...
NETSCOUT®, a provider of observability, AIOps, cybersecurity, and DDoS attack protection solutions, announces enhancements to its Arbor Edge Defense (AED) solution that helps enterprises maintain the availability of revenue-generating and mission-critical applications against sophisticated DDoS attacks that evade or bypass content delivery network (CDN) DDoS defences. The enhancements identify malicious sources concealed behind shared CDN infrastructure and apply precise, service-specific c...

Technology's role in securing banks and financial institutions
Download
Security technologies promote real-time awareness in K-12 schools
Download
Integrated systems enable critical and compliant security for transportation
Download
Modernising physical access control
Download
Access. Intrusion. One estate.
Download
