HackerOne - Experts & Thought Leaders


Latest HackerOne news & announcements

HackerOne, a global pioneer in Continuous Threat Exposure Management (CTEM), announces a partnership with OpenAI to make frontier GPT cyber models available in select H1 Platform products, H1 Code Security Audit, H1 Code, and H1 Remediation, to help teams find and fix vulnerabilities faster. GPT cyber models use is optional and enabled by the customer. The partnership addresses a growing challenge facing security leaders applying increasingly capable AI across the exposure management lifecycle to find vulnerabilities and exposures, validate which ones pose real risk, and help teams prioritise and remediate them. As frontier AI increases the speed and depth of discovery, the H1 Platform helps organisations turn that capability into measurable risk reduction. Exposure management lifecycle “AI is making complex attack paths increasingly discoverable, changing the risk calculation for every security leader,” said Kara Sprague, Chief Executive Officer at HackerOne. “Defenders have to assume that if an exposure exists, it will be found, and act before attackers do. That means building security programmes that continuously discover, validate, and eliminate risk, so organisations can move from reacting to threats to staying ahead of them.” Addressing that new risk requires connecting expanded discovery capabilities to the rest of the security lifecycle. “Frontier AI can significantly expand what defenders can discover, but findings must still be validated, prioritised, and translated into action,” said Nidhi Aggarwal, Chief Product Officer at HackerOne. “The H1 Platform can put frontier AI to work across the security lifecycle, finding and validating the exposures that pose real risk, tracing them to root cause, and giving teams a clear path to remediation.” Multi-model harness The H1 Platform multi-model harness can use OpenAI’s frontier cyber models through the Daybreak Defence Network to broaden coverage, validate outputs, and trace findings to root cause. Security teams receive each finding with a developer-ready fix plan designed to cut overall time to remediate. Frontier cyber AI is one layer of coverage. An elite community of security researchers provides another, bringing creativity, contextual understanding, and real-world adversarial expertise to complex attack chains, business logic flaws, and novel exploitation paths. Together, frontier cyber AI and human expertise provide complementary layers of continuous security. Improving generative AI models HackerOne does not use or permit use of confidential researcher submissions or customer vulnerability data to train, fine-tune, or otherwise improve generative AI models. The partnership builds on HackerOne and OpenAI’s work to strengthen cyber defense. HackerOne recently signed OpenAI’s “A call for collective action on cyber defence,” an open letter from organisations around the world calling for collective action to expand access to advanced defensive capabilities, share practical security expertise, and accelerate verified fixes. HackerOne is also a launch partner in Patch the Planet, an OpenAI initiative focused on using AI-assisted security research and human expertise to identify and remediate vulnerabilities in critical open-source software. To learn how frontier cyber AI is transforming Continuous Threat Exposure Management, register for their upcoming webinar, Outpacing the Attacker, on Friday, September 11, 2026, at 18:30 BST.
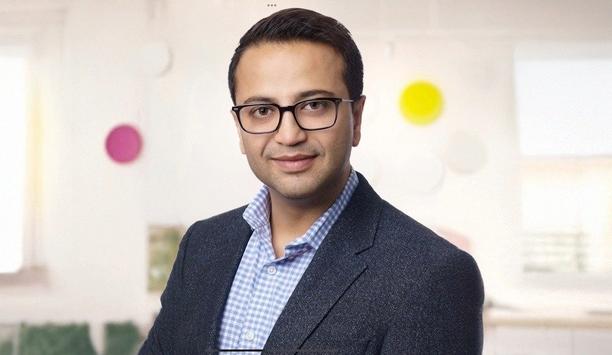
HackerOne, a pioneer in Continuous Threat Exposure Management (CTEM), announces the appointment of Naveen Bhateja as Chief People Officer. Bhateja joins the executive leadership team to lead the company's people strategy, leadership development and culture. Bhateja brings more than 25 years of experience building leadership and talent in global technology companies through periods of fast growth and change. At HackerOne, he will focus on developing the company's leaders, deepening its bench and helping employees grow as the business scales, strengthening the foundation beneath everything HackerOne builds for its customers and the researcher community. Strengthened executive capabilities "The pace of change in security has never been higher, and the organisations pulling ahead are the ones that invest as much in their people as they do in their technology," said Kara Sprague, CEO of HackerOne. "Naveen has spent his career guiding high-performing teams through exactly this kind of change. We're building an AI-native company where exceptional people grow together and shape the future of security." Bhateja has held senior people leadership roles at companies including Medidata, Juniper Networks, Amazon and JPMorgan Chase, where he shaped enterprise-wide talent and leadership strategies, organisational effectiveness, and strengthened executive capabilities during periods of significant business growth and change. “I have always believed talent is one of the greatest differentiators between good and great organisations because it unlocks everything else,” said Bhateja. “What drew me to HackerOne is that the company has built something genuinely difficult: a model where AI and human expertise make each other stronger. My role is to help build an AI-native organisation that equips our people to move faster, innovate and deliver greater customer impact.”
HackerOne, a global pioneer in Continuous Threat Exposure Management (CTEM), has joined Project Glasswing, Anthropic's controlled-access program for Claude Mythos 5. HackerOne will share what it learns about applying frontier AI to real-world exposure management to advance cyber defense at scale. Consistent with Project Glasswing’s mandate, HackerOne is using Mythos to strengthen its defenses. While doing so, HackerOne will benchmark Mythos’ performance in use cases beyond discovery: confirming exploitability with evidence, prioritising findings by business impact, and generating developer-ready fixes that integrate directly into engineering workflows. Different vantage point “Attackers are already using frontier AI to find and weaponise vulnerabilities faster than defenders can respond. The only viable answer is for defenders to operate on better models, faster. HackerOne's mission is to empower the world to build a safer internet. Anthropic's is safer software at scale. Same goal, different vantage point. Project Glasswing lets us put the most capable model available to work on our infrastructure and share what we learn across the full CTEM workflow," said Kara Sprague, Chief Executive Officer, HackerOne. "Building more resilient software requires continuous innovation in how we identify, understand, and remediate risk," said Nidhi Aggarwal, Chief Product Officer, HackerOne. "We are excited to use Claude Mythos to strengthen the security of our internal systems, explore how frontier AI can strengthen every stage of the CTEM workflow from discovery to remediation, and contribute insights that help the security industry move toward continuous cyber defence." HackerOne's participation in Project Glasswing is scoped exclusively to improve the security of its infrastructure and solutions. Claude Mythos 5 is not being applied to customer programs or external-facing agentic use cases.

Technology's role in securing banks and financial institutions
Download
Security technologies promote real-time awareness in K-12 schools
Download
Integrated systems enable critical and compliant security for transportation
Download
Modernising physical access control
Download
Access. Intrusion. One estate.
Download
