CommVault - Experts & Thought Leaders






Latest CommVault news & announcements

Commvault, a pioneer in unified resilience at enterprise scale, today announced Commvault Active Directory Pre Recover. This new solution, which utilises existing Commvault technologies – including Commvault Cleanroom and Threat Scan – to reduce the time it takes to cleanly recover Active Directory (“AD”) from hours to minutes. About Active Directory Pre Recover Active Directory Pre Recover creates a clean, standby copy of AD in an isolated, air-gapped Cleanroom environment. When disaster or disruption strikes, rather than waiting for a full forest recovery, or relying on complicated identity synchronisation, organisations can fail over in minutes to this clean copy and keep the business running. Commvault also utilises Threat Scan to continuously scan AD backups so the standby copy is free of malicious content. This innovation comes as identity systems have become a primary target for attackers and organisations are facing increased pressure to restore rapidly and without risk of re-infection. Cyber recovery “Identity is foundational to every enterprise application, user, and business process,” said Rajiv Kottomtharayil, Chief Products Officer, Commvault. “Commvault has already made significant progress reducing identity recovery times from weeks to hours, and now we are extending that progress toward near-real-time availability. The result is faster access to critical business systems and greater confidence during cyber recovery.” Additional benefits of Commvault Active Directory Pre Recover Keep critical operations running during a cyber incident: With the AD standby copy stored in Cleanroom, organisations can have peace of mind that, in the event production identity services are unavailable, trusted access to critical systems can continue. Minimise application and infrastructure disruption: Applications can continue authenticating against trusted identity services without requiring complicated replication of accounts in alternate Identity and Access Management Systems or waiting for a full forest restore to complete. Availability Commvault Active Directory Pre Recover will be available for early access in the coming months, delivered as part of Commvault's Identity Resilience portfolio. All enterprise AD customers will receive Active Directory Pre Recover as part of their existing license, including a lite version of Cleanroom. This offering will be available globally through Commvault's partner ecosystem.
Commvault, a pioneer in unified resilience at enterprise scale, announced a new integration with CrowdStrike that makes Commvault cyber recovery actions available as native steps within Charlotte Agentic SOAR workflows. The integration enables joint customers to automate Commvault recovery actions as part of security workflows, helping accelerate response and forensic investigations while reducing manual coordination between security and recovery teams. AI-driven automation is helping organisations detect, investigate, and respond to threats at machine speed, yet fragmented tools and workflows can slow security teams at critical moments. The new purpose-built connector enables security teams to incorporate Commvault cyber recovery actions directly into workflows orchestrated by Charlotte Agentic SOAR and rapidly accelerate investigation, response, and recovery. Without disrupting production systems Key capabilities include: Restrict access in Commvault to help prevent unauthorised changes during an active incident. Preserve clean recovery options by automatically suspending Commvault backup data ageing policies to retain viable recovery points during active incidents. Accelerate forensic investigations by restoring potentially compromised assets into Commvault Cleanroom, enabling investigators to begin analysis without disrupting production systems. Automated security workflows “Security and recovery teams need to move quickly and in coordination during an incident,” said Vidya Shankaran, Field CTO, Commvault. “Our integration with CrowdStrike Charlotte Agentic SOAR makes Commvault cyber recovery actions available directly within security workflows, helping joint customers reduce manual handoffs and accelerate investigation and response. This strengthens cyber resilience and simplifies how security and recovery teams work together seamlessly.” Today’s news is the latest in a series of integrations with CrowdStrike: Falcon Insight XDR brought CrowdStrike threat intelligence into Commvault Cloud; Falcon Next-Gen SIEM extended visibility; and the new Charlotte Agentic SOAR integration enables Commvault cyber recovery actions to be incorporated directly into automated security workflows. The integration between Commvault and Charlotte Agentic SOAR is generally available for joint Commvault and CrowdStrike customers. The integration is also available through the CrowdStrike Marketplace.
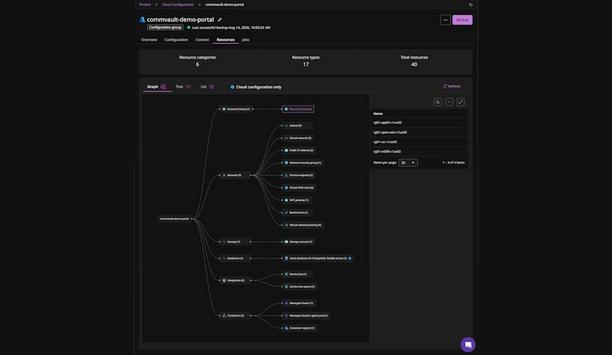
Commvault, a pioneer in unified resilience at enterprise scale, announces advancements to Cloud Rewind, expanding Microsoft Azure resource coverage for configuration protection and recovery. Through this expansion, Commvault is helping organisations more rapidly restore cloud applications and the resources that support them. Manually rebuilding environments is often slow, complex, and error-prone. According to Absolute Security's 2026 State of Enterprise Cyber Resilience report, 57% of enterprises said recovery from a cyberattack took more than 4.5 days on average. Discovering cloud resources Cloud Rewind addresses this by continuously discovering cloud resources, mapping application dependencies, and orchestrating the recovery and rebuild of cloud applications, including the infrastructure, configurations, and dependencies they need to operate, from a single platform. This expansion broadens Azure protection by 3X – now covering 62% of enterprise-relevant Azure resource types available in the market. Organisations can also validate recovery readiness through application recovery simulations, including within isolated, air-gapped environments, before an incident occurs. “In global logistics, every minute of downtime can disrupt supply chains and impact customer trust. Data is critical, but it needs the right cloud infrastructure to stay actionable,” said Venkata Sudhakar Nagandla, SVP & Global Head-IT Infrastructure & Cloud, Allcargo Group Companies. “With Cloud Rewind, we don’t just recover files — we restore our operational environment in hours, ensuring our customers experience continuity without compromise.” Multiple cloud environments Additional enhancements include: Deeper integration into Commvault backup and recovery: Protection Groups unite application data and cloud configuration into a single, air-gapped recovery experience, so teams can plan and execute recovery from one place instead of stitching together separate tools. More advanced policies for dynamic at-scale protection: Policy-based protection automatically enrols discovered resources by tag, region, and type across multiple cloud environments, using a single workflow, so teams can protect resources at cloud scale instead of onboarding them one at a time. Protected cloud resources “Modern applications depend on interconnected cloud services, infrastructure, and configurations that must be recovered together,” said Pranay Ahlawat, Chief Technology and AI Officer, Commvault. “Cloud Rewind helps organisations recover cloud applications through a unified experience in Commvault Cloud, increasing customers’ confidence in their ability to recover following a cyberattack or outage.” “Many organisations discover their recovery plan is incomplete only after an incident has occurred,” said Melinda Marks, Senior Research Director and Chief Analyst, Omdia. “As applications and their associated cloud resources become more complex, organisations need an effective way to rapidly recover, with restoration capabilities across configurations, dependencies, and multiple cloud platforms.” Cloud Rewind, available today, is delivered as an add-on workload within Commvault Cloud for cloud application protection and app-centric recovery. Expanded Azure protection is targeted for availability in the coming months. Pricing is metered based on protected cloud resources.
Insights & Opinions from thought leaders at CommVault

Every day, millions of people worldwide use their personal credentials to prove their identity and access a range of services, from databases in their workplace to the banking app on their smartphone. But while this ensures only authorised people have access to certain systems, the use of this personal data opens users up to cyber risks, primarily in the form of identity theft. On Identity Management Day, Source Security spoke to seven IT and cybersecurity experts to discuss their experiences and advice on identity management, including James Brodhurst, Principal Consultant at Resistant AI, who reinforces that: “Securing identities is more important than ever, as fraud and identity theft has impacts for businesses as much as for individuals.” Effective identity management He recommends that businesses and other organisations that use consumer identities as an integral part of operations must address the significant challenges of managing identities and recognise that there is no single solution to all possible cyber threats. Effective identity management is only achieved through a broad range of technologies and data. Businesses have a critical role to play in mitigating cyber threats, as does society as a whole" This is an important first step for organisations to know who they are interacting with, and subsequently distinguish between genuine or illicit actions. “Businesses have a critical role to play in mitigating cyber threats, as does society as a whole. Initiatives such as Identity Management Day serve to increase our collective awareness of the issues and threats we’re facing, and also safeguard sensitive data.” External cyber defences “Why is identity theft so common?” ponders Andy Swift, Technical Director of Offensive Security at Six Degrees. “Well, the simple answer is stealing account credentials is big business. There is a massive industry out there of people stealing and selling credentials on the dark web. I don't suggest you venture to the marketplaces through which stolen credentials are sold on the dark web, but if you did you'd find lists of credentials with different attributes – whether they've been tested, whether they have access to financial data – that dictate price.” “Most stolen credentials are sold to people looking to launch phishing and onward phishing attacks, giving them access to compromised mailboxes to send emails from. Secondly, there are hackers who want to launch attacks – ransomware, more than likely – from within a network without having to navigate its external cyber defences while also evading the long wait for brute force attacks, phishing attacks and other noisy activities to pay off.” Access sensitive data Credential stuffing is one of the most common forms of attack and corporate credentials are usually the target" “And thirdly, there are people who want to simply target external administration interfaces they have identified (RDP for example) which they can in turn use to pivot through to internal networks, or even just target the external host directly.” Gregg Mearing, Chief Technology Officer at Node4, adds: “Credential stuffing is one of the most common forms of attack and corporate credentials are usually the target. In 2020 alone there were 193 billion credential stuffing attacks globally. Attacks commonly start with a database of stolen credentials, usually with usernames, emails and passwords – although phishing emails and suspicious websites are also used to steal corporate credentials. Once they have gained entry into the organisation's system, the attacker can move laterally, completely unnoticed, to access sensitive data, remove files or plant malware.” Most common threats “Despite the ubiquity of this style of attack and a wide understanding of the importance of password hygiene, 65% of people still reuse passwords across multiple accounts. There can be no doubt that employees are the first line of defence for an organisation against a cyber attack. If trained properly, they can act as a human firewall. However, poor cyber hygiene, a lack of best practice when it comes to managing credentials, and a limited understanding of the most common threats can make an organisation’s employees its greatest weakness.” Despite the ubiquity of this style of attack and a wide understanding of the importance of password hygiene" Alongside credential stuffing and phishing, Liad Bokovsky, Senior Director of Solutions Engineering at Axway, explains how API attacks are yet another way criminals are executing identity theft: “In fact, last year API attacks increased 348%, and companies affected included some of the largest corporations – Facebook, Instagram, and Microsoft.” Protecting customers’ data “Companies need to do a better job at protecting their customers’ data. In a recent survey, 82% of UK consumers confirmed they would stop doing business with a company if it suffered a data breach that exposed their personal information.” “Thriving and surviving in today’s hyper-connected economy increasingly depends on having sufficient API maturity in place to ensure that anything connecting to an organisation’s servers – devices, apps, customers – is managed appropriately to keep APIs, customer data and the company’s reputation safe. This means having technology and processes in place to make sure that API design, implementation, and management are done properly.” Owning smart devices This needs to change and with the UK no longer required to adhere to EU-GDPR legislation" Michael Queenan, CEO, and Co-Founder of Nephos Technologies, explains how the huge volumes of personal data being created every day are putting consumers at risk: “Whether shopping online, setting up a social media account or simply reading a news article, we are regularly being asked for our identifiable information. With 10% of UK homes now owning smart devices – e.g. an Alexa or a Ring doorbell – our data is constantly being collected, even within our own homes. Should it fall into the wrong hands, it could be used for identity theft or fraud.” “This needs to change and with the UK no longer required to adhere to EU-GDPR legislation, it presents an opportunity to rectify how personal data can be shared. Ultimately, I believe individuals should be responsible for their own data and how it is used.” Ensure data privacy “A possible way of achieving this is through identity-centric blockchain, whereby everyone has a national email address associated with their blockchain identity that permits access to their personal data. This would ensure that only you get to decide who has access – your data, your choice!” This would ensure that only you get to decide who has access – your data, your choice" Steve Young, UKI Sales Engineering Director at Commvault also comments on how identity management is vital for meeting data regulations, thereby supporting data management throughout the business: “In the world of data management, you’d be forgiven for thinking that the focus is all on backups and recovery. But while these are absolutely crucial elements, another key aspect of data management is identity management – only through understanding it will businesses be able to drive their data management to the next level. Identity management is necessary to ensure data privacy.” Latest data regulations “Many people will be most familiar with its function as a way to restrict access of employees to certain files and resources that may hold sensitive or classified information. But what is becoming more important today is how identity management also helps prevent cybercriminals entirely outside an organisation from gaining unauthorised access to a system and initiating a ransomware attack, for example. Because of this, identity management helps businesses be compliant with the latest data regulations, as it ensures that any customer data collected and stored is kept secure.” So, what solutions should IT leaders be prioritising to strengthen their identity management measures? Six Degrees’ Andy Swift recommends multi-factor authentication (MFA): “MFA provides great defence against identify theft, but it's also a reactive technology: for it to be effective, an attacker must already have obtained stolen credentials.” Cyber security training Credential-driven attacks are largely exacerbated by a ‘set it and forget it’ approach to identity management" “That's why comprehensive cyber security training and education on best practices is quite possibly more important than any technology could ever be alone. There's no silver bullet when it comes to achieving strong identity management, but the importance of threat awareness and training cannot be overstated.” “We advocate for the best practices that ensure cyber hygiene and protect personal and professional identities and credentials to prevent credential-based attacks from continuing,” concludes Tyler Farrar, CISO at Exabeam. “Credential-driven attacks are largely exacerbated by a ‘set it and forget it’ approach to identity management, but organisations must build a security stack that is consistently monitoring for potential compromise." "Organisations across industries can invest in data-driven behavioural analytics solutions to help detect malicious activity. These analytics tools can immediately flag when a legitimate user account is exhibiting anomalous behaviour indicative of credential theft, providing greater insights to SOC analysts about both the compromised and the malicious user, which results in a faster response time.”

Security technologies promote real-time awareness in K-12 schools
Download
Technology's role in securing banks and financial institutions
Download
Integrated systems enable critical and compliant security for transportation
Download
Modernising physical access control
Download
Access. Intrusion. One estate.
Download
