Integration software

Honeywell Technologies announced that its LenelS2 OnGuard platform was used as the foundation to modernise the campus-wide access control infrastructure at Vanderbilt Health (VH), a leading academic health system serving thousands of staff, patients and visitors every day. As healthcare organisations face growing operational complexity and evolving security requirements, physical security systems are increasingly becoming part of broader business and operational strategies. At VH, the m...

Nutanix , a pioneer in hybrid multicloud computing, today announced the promotion of Christian Turcati to Vice President, Pre-Sales Systems Engineering, EMEA. In this expanded leadership role, Turcati will lead the technical strategy and customer engagement capabilities of Nutanix’s pre-sales organisation across the entire region. Experience Over an 11-year tenure at Nutanix, Turcati has established a strong track record of success. Most recently leading the EMEA South Systems Engi...
Gallagher Security has released its fourth annual Security Industry Trends Report, revealing an industry moving decisively towards automation and analytics while facing a growing question: who owns the data behind it all? Drawing on the views of over 670 security professionals worldwide, the 2027 report captures an industry where security systems are doing far more than opening doors and protecting sites. The data they generate is increasingly being used to understand how buildings and people o...

Detection Technology, a pioneer in X-ray detector solutions, announces the launch of X-Tile HS, a high-speed, four-side tileable computed tomography (CT) detector module. It enables CT manufacturers to build detector configurations for rotating and stationary CT systems from a single standard building block. Expanding the established X-Tile series, X-Tile HS combines four-side tiling, high speed, wide dynamic range, low noise, and low power consumption in a compact module, enabling flexible syst...

Safetrust is demonstrating Aliro card and mobile credentials working side by side at Global Security Exchange (GSX) 2026, along with live Access Control Emulation (ACE), the Neural Adapter, and Badgeless Access powered by facial authentication. The company is exhibiting at booth 3545 at the Georgia World Congress Center in Atlanta, GA, September 14 – 16. Safetrust will also present a featured education session during the event: One Credential, Any Reader: How the Aliro Standar...

Five months after joining forces, March Networks®, a global pioneer in video surveillance and business intelligence, and VIVOTEK, a foremost global security solutions provider, will exhibit jointly at Global Security Exchange (GSX) 2026 for the first time. At booth 1823, September 14–16 at the Georgia World Congress Center in Atlanta, the combined organisation will demonstrate how Connected Intelligence for Modern Security brings together video, AI, cloud, business intelligence a...
News

Cozaint Corporation, the Intelligent Video Lifecycle Management company, announced the commercial availability of its patented MARCIA™ platform for Milestone XProtect® video management software environments. About MARCIA MARCIA enables organisations using Milestone XProtect to extend video retention beyond traditional primary-storage limits while continuing to use XProtect exactly as they do today. MARCIA continuously replicates newly recorded video in the background to LTO-based long-term storage —typically within a couple of minutes of the original write— providing XProtect customers with what Cozaint believes is the lowest-cost architecture available for video surveillance retention. Challenges For enterprise security environments, video retention has historically been constrained by the economics of disk-only storage. As camera counts, resolutions, frame rates, compliance requirements, legal exposure, and AI analytics use cases continue to expand, organisations increasingly need an architecture that preserves video beyond the standard 30-, 60-, or 90-day overwrite cycle. Cozaint’s MARCIA platform addresses that challenge by providing Intelligent Video Lifecycle Management (IVLM) for enterprise surveillance environments. Long-term video lifecycle management “The surveillance industry has spent more than thirty years optimising how little video it can afford to keep,” said Nauzad Sadry, Chief Technology Officer of Cozaint Corporation. “MARCIA changes that equation for Milestone XProtect customers. By extending XProtect environments with long-term video lifecycle management and LTO-based retention, organisations can preserve the video history they may need for investigations, compliance, legal defense, operational intelligence, and future AI analysis.” XProtect records the video. Within minutes, MARCIA is already preserving its future. Design and features MARCIA is designed to operate behind the scenes within the customer’s existing surveillance architecture. The VMS remains the day-to-day operational platform for live viewing, recording, user management, alarms, investigations, and security workflows. MARCIA extends the long-term value of the video managed by the VMS by enabling organisations to preserve video beyond normal retention windows and retrieve it when needed. Importantly, MARCIA does not interrupt XProtect’s normal recording workflow. Cameras continue recording into the customer’s existing XProtect primary storage environment. In near real time MARCIA operates in the background to replicate and organise newly recorded video onto LTO-based storage. This process occurs without interrupting ongoing XProtect recording. Security operators continue using XProtect normally for live monitoring, playback, alarms, and investigations, while MARCIA continuously builds the long-term retention copy behind the scenes. Milestone XProtect environments For Milestone XProtect environments, MARCIA supports long-term video retention workflows including automated tiered-storage management, LTO-based preservation, camera/date/time-based retrieval, metadata-aware recall, and restoration of historical video back into the XProtect workflow. The objective is simple: XProtect continues operating as XProtect, while MARCIA extends how long the organisation can preserve and retrieve the video XProtect records. As AI and video analytics become increasingly important to physical security and business operations, historical video is becoming more valuable. However, AI cannot analyse video that has already been deleted. MARCIA helps organisations preserve the long-term visual history required for future analysis, pattern discovery, incident review, and business intelligence. Cozaint refers to this as Enterprise Visual Continuity, preserving Trusted Visual Evidence over time so organisations can continue using and learning from video long after it was recorded. Key benefits of MARCIA for Milestone XProtect environments Extended Video Retention: Preserve video for months or years instead of letting primary storage limits dictate the retention period. LTO-Based Long-Term Preservation: Use LTO to deliver the lowest-cost path to long-term video preservation. Reduced Disk Dependency: Avoid continuously expanding expensive primary storage simply to keep older video. Continuous Background Replication: MARCIA continuously replicates newly recorded XProtect video to long-term LTO storage in the background, typically within a couple of minutes of the original write, while normal XProtect operations continue uninterrupted. AI-Ready Historical Video: MARCIA helps preserve the historical video needed for future AI, analytics, investigations, compliance, and operational intelligence. Evidence Preservation: Organisations can better retain Trusted Visual Evidence for legal defense, incident review, risk management, and compliance-driven retention needs. Commercial availability MARCIA support for Milestone XProtect environments is commercially available from Cozaint Corporation.

Cequence Security, the pioneer in application, API, and agentic AI protection, today announced four new capabilities for AI Gateway: AI Discovery, API Registry, LLM Registry, and Skill Registry. The release also upgrades Agent Personas, which now bind an agent’s job description directly to its model, tools, access, and guardrails, all enforced automatically through policy. Together, these capabilities let any business user stand up properly secured, governed AI agents, bound to the right tools, data, and protections for their job, without needing technical experience or touching AI Gateway directly. Backend services and data With this release, Cequence becomes the first platform to close the ring around every channel an AI agent uses to communicate with the outside world. MCP governs how an agent discovers and invokes tools. LLM Registry governs every call to and from a language model. API Registry governs how it reaches backend services and data. Agent Personas bind an agent's tools, model, and API access to a single job description, enforcing that boundary as policy rather than manual review. Where other vendors address one piece of that surface, Cequence ties MCP, LLM, and API together under one agent-bound identity, an approach they call Agentic Zero Trust. Nothing an agent touches is implicitly trusted, and every action is scoped to exactly what its job requires. Sandboxed evaluation environment The stakes are no longer hypothetical. OpenAI recently disclosed that two of its models escaped a sandboxed evaluation environment, crossed the open internet, and breached Hugging Face's production infrastructure, chaining stolen credentials and a zero-day to steal a benchmark answer key. Nothing had bound those agents to a job, so nothing stopped them from inventing one. Notably absent was any binding between the agent and its assigned job. Under Cequence, that binding is the Agent Persona, and an agent's models, tools, and APIs are defined by its job description, not by what it can reach once it's loose. Hugging Face's production infrastructure was never going to be on that list, regardless of what credentials the agent got its hands on. A zero-day can still get an agent past a sandbox, but it can't get a persona-bound agent past a policy that was never written to allow it there in the first place. Agentic AI governance Agentic AI adoption has outrun agentic AI governance. Point solutions have addressed pieces of the problem, a scanner here, an API gateway there, and a prompt filter somewhere else. None of them answer the questions every security leader is now asking: which agents does the organisation have, what can they reach, what actions can they take, who approved them, and how fast can they be shut down when governance guardrails are violated. Enterprises are recognising that AI agents with access to applications and data are much more than tools. They are privileged insiders operating at machine speed and require the same governance discipline as any other privileged use inside of the business. Enterprises already secure, manage, and guide human employees whether they work from an office or remotely, and AI agents need the same standard, regardless of whether they run on managed devices or in the cloud. Same governance discipline “Most vendors look at agent governance and build another approval queue. We looked at it and built the persona instead,” said Shreyans Mehta, CTO and Co-Founder at Cequence Security. “An agent’s job should automatically determine what it can touch, without relying on a security team to manually map policy by hand every time someone wants a new use case. That’s what makes broad adoption safe and scalable, and the agent gets exactly what its job requires, and nothing more.” Cequence AI Gateway’s new and improved capabilities include: AI Discovery surfaces every agent, LLM provider, and MCP server already running across the enterprise, pulled from existing SIEM logs whether or not it went through an official process. API Registry lets agents call approved APIs without ever holding the underlying credential. Agents authenticate with a single AI Gateway access key, either through a single invocation tool for web-based agents or natively through AI Gateway’s proxied endpoints. Skill Registry gives security and platform teams a curated, governed set of capabilities to draw from, vetted once and reusable across every agent use case that needs it. Agent Personas bind an agent to a job description. That includes a curated set of tools, APIs, skills, and instructions, the specific LLM model it's approved to use, and the security guardrails that apply to it, all enforceable via policy. Relevant data protection policies apply automatically based on the persona's data surface and job function, including which LLM model it can call, since an ungoverned model is as much a risk as an unvetted API. LLM Registry governs every agent-to-LLM call the same way API Registry governs REST access, brokering credentials across major LLM providers so agents never hold a real provider API key. Built-in Data Loss Prevention inspects every prompt and response for blocked content, including base64-encoded payloads and invisible or non-approved-language Unicode characters used to evade filters. It also governs model use per team, for example defaulting to a cost-effective model while routing advanced engineering tasks to a premium one, with token-level usage visibility and enforceable rate and spend limits tied back to the agent persona driving each request. Cost-effective model “Automatic policy mapping was not possible until now, because there was nothing consistent for a policy engine to reason over," said Abraham Jeevagunta, VP of AI Products at Cequence Security. "Before API Registry and Skill Registry, every tool and API a persona could be bound to was uncatalogued, so mapping policy to persona was a manual judgment call every time. Now, that record exists and the policy engine can read it directly. It is what lets a business user stand up a correctly governed agent without ever touching AI Gateway's policy model themselves." All of these capabilities are immediately available to Cequence customers as part of AI Gateway.

Ping Identity, a pioneer in securing digital identities for the world’s largest enterprises, announced that its patient identity verification and fraud protection capabilities for MyChart are listed in Epic Toolbox. Modernising patient access Healthcare organisations are continuing to modernise patient access experiences while balancing security, privacy, and operational efficiency. Account creation and recovery in MyChart environments require organisations to support seamless patient experiences while incorporating identity verification, fraud detection, and adaptive risk response into digital workflows. MyChart details Ping Identity provides patient identity verification combined with real-time fraud and risk detection as a packaged solution for healthcare organisations using MyChart. Powered by dynamic orchestration, these capabilities bring identity verification, fraud and risk detection into MyChart-connected workflows, allowing organisations to automate and secure patient onboarding and account recovery while reducing friction for legitimate users. The solution includes three core capabilities for MyChart environments that help organisations address these needs: Identity Verification: Verify patients during account creation and recovery using government-issued ID, biometric matching, and liveness checks Threat and Risk Detection: Detect synthetic identities, account takeover attempts, and suspicious activity using real-time behavioural and environmental signals No-Code Orchestration and Dynamic Response: Guide patients through the appropriate account creation or recovery flow in real time, with the ability to allow, challenge, step up, or block interactions based on risk By enabling healthcare organisations to move beyond static authentication toward continuous, verified trust across patient interactions, the solution helps reduce fraud during account creation and recovery while improving patient access experiences and operational efficiency. The solution works with existing MyChart-connected healthcare systems, helping organisations strengthen security without replacing current infrastructure. Supporting privacy-preserving standards Ping Identity’s identity verification approach is designed to support privacy-preserving standards. It uses minimal data collection and policies that support rapid deletion of Personally Identifiable Information (PII) following identity verification. This supports healthcare organisations’ privacy and compliance objectives, including HIPAA-related requirements. “Healthcare organisations are being asked to do more with less while protecting increasingly sensitive data,” said Steve Gwizdala, VP Healthcare at Ping Identity. “Ping Identity helps secure patient account creation and recovery connected to MyChart, reducing risk and operational burden without adding friction for patients.”

Nozomi Networks, the pioneer in OT, IoT and cyber-physical systems security, announced that co-founder Andrea Carcano has been appointed Chief Executive Officer, resuming the role he first held when he and co-founder Moreno Carullo launched the company. The appointment marks the start of Nozomi's next phase, one focused on accelerating the AI-driven innovation and technical leadership that have defined the company since its founding. Edgard Capdevielle, who has served as CEO for the past decade, will remain closely involved as an executive advisor to the company. Founder-led leadership Fourteen years ago, Carcano and Carullo started with a single conviction: the industrial world deserved far better security than anything that existed. They wrote the first lines of code, won the first customers, and built the company from nothing. Just over ten years ago, the two founders brought in Capdevielle with a clear mission: take their platform to market, build a world-class go-to-market organisation, and raise the capital needed to compete at the highest level. With Nozomi Networks' recent acquisition by Mitsubishi Electric, completed on the heels of the company surpassing $100M in annual revenue, that mission is complete, and the company is graduating into its next chapter with founder-led leadership at the helm. Next chapter "Edgard has been an extraordinary partner to Moreno and me for the past decade — on behalf of everyone at Nozomi, thank you, Edgard. Stepping into this role feels like returning to where our story began, only now with the conviction of everything we've proven since: category-defining products, the trust of the world's most critical operators, and market leadership recognised across the industry." "Moreno and I built Nozomi side by side from the very first lines of code, and side by side is exactly how we'll lead its next chapter. This is a new Day 1 — the same hunger and audacity that started this company, now with everything it takes to win at the largest scale." Andrea Carcano, Co-Founder and CEO, Nozomi Networks Milestones Over the past 10 years, Nozomi Networks achieved milestones that few companies in the category can match: Surpassed $100M in annual revenue, becoming the first privately held OT cybersecurity company to achieve sustained cash-flow break-even performance Earned the trust of the world's most critical operators, including 5 of the top 10 oil and gas companies, 7 of the top 10 pharmaceutical manufacturers, and 7 of the top 10 utilities Named a Leader in the Gartner Magic Quadrant for CPS Protection Platforms and the Forrester Wave for IoT Security, and the only recognised Customers' Choice in Gartner's Voice of the Customer Recognised by Gartner as “The Company to Beat for AI in CPS Protection Platforms” and named to Fast Company's World's Most Innovative Companies list Completed the company's acquisition by Mitsubishi Electric, gaining the resources of a global industrial leader while preserving Nozomi Networks' independent operations and vendor-neutral approach That foundation sets the stage for what comes next. Nozomi Networks is entering an era in which leadership in OT and IoT security will increasingly be defined by leadership in AI — and the company intends to set the pace, with the founders who pioneered the category now leading it into its next chapter. Authority comments “This is the moment our industry has been building toward - where the pace of AI on both sides, attacker and defender, decides who leads. The joy of building what nobody has built before is why Andrea and I started this company, and it's exactly what this next chapter is about.” Moreno Carullo, Co-Founder and CTO, Nozomi Networks “Our commitment to our customers and partners doesn't change today. Everything we do — every product decision, every collaboration, every hire — starts with the outcomes our customers need, and that will be as true a decade from now as it is today.” Andrea Carcano, Co-Founder and CEO, Nozomi Networks Accelerating innovation and technical leadership Nozomi Networks' customers and partners will experience full continuity: account teams, support commitments, partner programs, and the product roadmap all remain unchanged. Innovation has always been Nozomi Networks' superpower, and under Carcano's leadership the company will accelerate both its innovation and its technical leadership in an era defined by AI. “Leading Nozomi through this stage of its journey has been the honor of my career. Andrea and Moreno built something extraordinary, and I'm proud of what we accomplished together. I'm looking forward to continuing to support the team as an advisor while returning to what I love most - helping early-stage companies find their way. Nozomi's best chapter is the one that starts today.” Edgard Capdevielle, Nozomi Networks
ZeroEyes, creators of the foremost multi-analytics weapons detection and threat intelligence platform, announced a partnership with Advantech, a pioneer in security integration and controls company in the mid-Atlantic, and the Camden Police Department to deploy ZeroEyes’ AI gun detection and intelligent situational awareness platform at Delaware’s Caesar Rodney School District (CRSD). Advantech has been a partner of CRSD for 30 years, and worked closely with Camden Police Chief Marc Whitney to bring ZeroEyes to the district. Leveraging advanced tools "When I saw a ZeroEyes demonstration at an Advantech symposium, I immediately recognised it as a must-have for the school districts in my jurisdiction,” said Marc Whitney, Chief of Police, Camden Police Department. “By coordinating with the CRSD and Advantech to leverage advanced tools like this, we can respond more quickly to potential threats and ensure a secure learning environment for everyone." Layer of protection to CRSD's safety programme The district spans 107 square miles in central Kent County and serves 8,259 students across 15 schools. It is adding ZeroEyes to a multilayered security approach that also includes CEIA metal detectors, the Milestone Video Management solution, armed constables at the high school and middle school, and a Delaware State Trooper on campus. The district also works closely with the Camden Police Department to ensure a safe, seamless experience for students, staff, and families. The adoption of ZeroEyes' AI gun detection technology at Caesar Rodney High School, Fred Fifer III Middle School, and Nellie Hughes Stokes Elementary School adds another critical layer of protection to CRSD’s safety programme. "Student safety is our top priority, and we are committed to using every tool available to protect our schools,” said Mark Gaglione, Caesar Rodney School District Safety and Security Coordinator. “Deploying ZeroEyes enhances our multilayered security approach, giving our staff and students greater peace of mind each day." Software details ZeroEyes' AI gun detection and intelligent situational awareness software layers onto existing digital security cameras. If a gun is identified, images are instantly shared with the ZeroEyes Operations Center (ZOC), the industry's only U.S.-based, fully in-house operation center, which is staffed 24/7/365 by specially trained U.S. military and law enforcement veterans. If these experts determine the threat is valid, they dispatch alerts and actionable intelligence — including visual description, gun type, and last known location — to law enforcement and local security teams, often in a matter of seconds from the moment a gun is detected. Authority comments "We’re proud to partner with Advantech and the Camden Police Department to bring our solution to Caesar Rodney School District,” said Mike Lahiff, CEO and co-founder of ZeroEyes. "Advantech’s expertise in evaluating and applying technology to best support their customers is remarkable, and I’m proud that they trust ZeroEyes to help keep schools safe." “We are excited to highlight the collaboration between Camden PD and Caesar Rodney SD in delivering a solution that strengthens a layered approach to student safety,” said Ryne Johnson, Account Manager, Advantech. “This achievement reflects the coordinated leadership of Chief Whitney and would not have been possible without that unified effort. The project underscores the importance of strong partnerships and the use of advanced technology to support proactive responses in security situations.”

dormakaba has been recognised as one of TIME magazine’s Most Sustainable Companies 2026, ranking 662nd among 5,800 assessed companies worldwide. Following a comprehensive evaluation process, only 750 companies were selected for inclusion in the annual ranking. The recognition highlights organisations that are leading the way in sustainability and setting benchmarks for responsible business practices, transparency, and accountability. Reducing environmental impact “We are proud to be recognised among TIME’s Most Sustainable Companies 2026,” says Stephanie Ossenbach, Group Sustainability Officer of dormakaba. “This recognition reflects the commitment of our employees around the world and reinforces our ambition to create sustainable value for our customers, shareholders, employees, and the communities in which we operate. Sustainability is an integral part of how we do business and how we shape the future of access solutions.” The ranking was developed by TIME in partnership with Statista and is based on a rigorous assessment of more than 20 key performance indicators. The evaluation covers sustainable business practices, external sustainability ratings and commitments, reporting standards and transparency, as well as environmental and social performance. As a global provider of access solutions, dormakaba is committed to supporting customers in creating safe, secure, and sustainable buildings and infrastructure. The company’s sustainability efforts focus on reducing environmental impact, fostering an inclusive workplace, maintaining high ethical standards, and driving innovation that supports a more sustainable built environment.

Expert commentary

In the ever-evolving struggle between cyber offence and defence, attackers have almost always moved first. In the emerging domain of artificial intelligence, this pattern appears to be repeating itself. Yet, global cybersecurity pioneers appear disconcertingly disengaged. Just over half even agree that AI-driven attacks are set to become dramatically more complex and widespread. Equally concerning is the widespread apathy regarding AI’s role in expanding an already sprawling corporate attack surface. This is no small oversight. A recent global Trend Micro study showed that 73 percent of organisations have already suffered cybersecurity incidents due to unknown or unmanaged assets. In an era where digital blind spots are both common and consequential, hesitation is a risk few can afford. Security has to shift from reactive protection to proactive risk exposure management. The opportunity and the risk of AI Threat actors are now using jailbroken versions of legitimate generative AI tools such as ChatGPT The potential for AI to transform enterprise operations is enormous, but so is the risk. The warnings have been loud and clear. As early as the first quarter of 2024, the UK’s National Cyber Security Centre (NCSC) stated that AI would “almost certainly increase the volume and heighten the impact of cyber-attacks over the next two years.” Their prediction is proving accurate. Threat actors are now using jailbroken versions of legitimate generative AI tools such as ChatGPT, freely traded as services on the dark web, as well as malicious models like FraudGPT, built on open-source large language models (LLMs). These tools are no longer just about automating tasks; they are turbocharging the entire attack lifecycle. From more convincing phishing emails and precise target selection, to sophisticated malware creation and lateral movement within breached systems, AI is driving a step-change in threat actor capability. Integrating open-source models However, this is only one side of the coin. The other, often overlooked, is AI’s impact on the corporate attack surface. Even well-meaning employees can unintentionally expand organisational risk. The widespread use of AI-as-a-service tools like ChatGPT introduces significant shadow IT concerns, especially when sensitive business information is input without proper oversight. Data processing and storage practices for many of these services remain opaque, raising additional compliance concerns under regulations like the UK GDPR and the EU’s AI Act. For those organisations that choose to build or customise their own LLMs, the risks multiply. Integrating open-source models may expose businesses to vulnerabilities, misconfigurations and flawed dependencies. Each new tool and environment adds to the complexity of an attack surface already strained by remote work setups, sprawling cloud deployments, IoT ecosystems, and accelerating digital transformation programmes. Managing the expanding risk landscape Many have already shared security incidents where a lack of asset visibility was the root cause Many security pioneers do understand what is at stake. Nine in ten agree that effective attack surface management is tied directly to business risk. They cite a long list of potential consequences, disruptions to operations, reputational damage, declining competitiveness, strained supplier relationships, financial losses and reduced staff productivity. Many have already experienced security incidents where a lack of asset visibility was the root cause. Despite this recognition, however, the response remains largely inadequate. Fewer than half of global organisations use dedicated tools to monitor their attack surface proactively. On average, only a quarter of cybersecurity budgets are allocated to managing cyber risk exposure. Third-party risk management is similarly neglected: fewer than half of firms actively monitor their vendors for vulnerabilities. This inertia creates an obvious contradiction. Security pioneers understand the business implications of unmanaged risk, but they are not equipping themselves with the tools or processes to respond. That needs to change—and fast. How AI can help defenders take the lead There is good news: AI is not only a weapon for cybercriminals. It can also be a powerful ally for defenders, particularly in the field of Cyber Risk Exposure Management (CREM). The best tools in this category use AI to continuously scan an organisation’s entire digital footprint. They can automatically detect vulnerabilities, spot misconfigurations, identify rogue or shadow assets, and provide prioritised remediation recommendations. CREM platforms apply contextual filtering to reduce false positives and elevate the most urgent threats Intelligent algorithms can also analyse network behaviour to identify anomalies that could signal a breach in progress. Unlike traditional tools, which often drown analysts in noise, CREM platforms apply contextual filtering to reduce false positives and elevate the most urgent threats. For overburdened security teams, this enables a far more focused and effective response. However, the keyword here is “continuous.” The nature of today’s IT environments, especially in the cloud, is dynamic and fast-moving. Assets appear and disappear within minutes. Static, point-in-time assessments are no longer sufficient. Yet more than half of organisations still lack continuous scanning processes. This leaves them exposed to risks that might persist undetected for weeks or months. Overcoming barriers to adoption So what is holding organisations back? In many cases, it’s not the technology itself but the internal politics of investment. Security pioneers interested in CREM tools often prioritise real-time alerting, clear dashboards, and seamless integration with their existing environments. All of this is now achievable. The challenge lies in securing board-level support. Many security teams still work in silos, disconnected from the broader business Boards are often cautious when it comes to cybersecurity investment, particularly when immediate ROI is not clear. To gain their trust, security pioneers must learn to speak the language of business risk, not technical threat. They must frame cyber exposure in terms of reputational impact, regulatory liability, operational continuity, and investor confidence. There is also a cultural component. Many security teams still work in silos, disconnected from the broader business. This limits their influence and makes it harder to embed security as a strategic enabler. In the AI era, this divide must be bridged. Cybersecurity must become a board-level concern, and risk exposure must be treated as a fundamental operational issue. Time to act We are at a critical inflection point. The AI revolution is not on the horizon, it is already here. Threat actors are moving rapidly to exploit it, leveraging tools and techniques that were unthinkable just a few years ago. Meanwhile, organisations remain slow to respond. Too few are investing in the tools, processes, and people needed to manage their risk exposure effectively. AI can be used not only to attack but to defend. CREM tools powered by AI offer a powerful way to regain visibility, restore control, and build lasting resilience. They enable proactive rather than reactive security. And they help organisations align their cybersecurity strategy with their broader business objectives. Security teams have to elevate the conversation. They must advocate not just for new tools, but for a new mindset, one that treats cyber risk as an enterprise risk, and one that prioritises continuous visibility as a prerequisite for resilience.
Technology advances in the security industry are transforming the way modern systems are designed and installed. Customers today are looking for greater scalability and flexibility, lower up-front costs, and operational efficiency. Cloud-based software as a service (SaaS) solutions, AI-enhanced tools, and IoT-enabled sensors and devices are increasingly in demand. The traditional role of the systems integrator is evolving as a result. While security integrators have always worked closely with end users, today’s pioneers go beyond installation and maintenance. They align security strategies with evolving business needs, integrating IT, cybersecurity, and data-driven insights into their offerings. A look at the past and present Integrators are often asked to help tailor solutions and provide expertise in IT and cybersecurity Traditionally, systems integrators specialised in installing and maintaining wired physical security systems like CCTV, access control, and alarms. The service model was built around large, up-front investments and project-based installations. However, today customers are seeking comprehensive solutions. They’re looking to wirelessly integrate security infrastructure with cloud-based SaaS systems and IoT devices. While modern systems are often faster to deploy, they’re most effective when supported by ongoing consulting and strategic planning. Integrators are often asked to help tailor solutions and provide expertise in IT and cybersecurity. Data requirements and modern systems Data requirements have also changed. Modern systems collect vast amounts of data. Advanced analytics, machine learning, and automation are now must-have tools for actionable insights. Security integrators can help end users set up custom dashboards, automations, and continuous system optimisation. Let’s look at some of the specific ways the role of systems integrators is evolving and how to adapt and succeed. Strengthen your IT expertise Integrators with IT expertise can ensure that hardware is optimised and maintained for peak performance The competitive landscape today includes not just security specialists but also IT-focused integrators and SaaS providers. Systems integrators with expertise in traditional physical security solutions plus IT experience offer unique value. They understand the real-world security challenges and opportunities, along with cybersecurity and network best practices. Integrators with IT expertise can also ensure that hardware is optimised and maintained for peak performance. Their experience with legacy systems allows them to offer practical recommendations on cost-effective approaches, such as upgrading or integrating older hardware with new digital solutions. Consider who’s making the purchase decisions Traditionally, security integrators primarily sold to security directors, facility managers, and operations teams. Now, multiple stakeholders may be involved in decision-making. IT teams, CIOs, and CTOs often weigh in on purchase decisions when cloud-based security and SaaS solutions are under consideration. Customers today aren’t just shopping for cameras, access control panels, alarms, and other hardware components. They’re looking for security ecosystems that can integrate with enterprise-wide IT infrastructure and business applications. When working with these different teams, consider outlining the system's return on investment (ROI). How can the solution reduce risk for various departments? Can it help improve operational efficiency or reduce the time required to onboard and train staff? Will it make regulatory compliance easier to manage? Focus on the long-term value for the entire organisation. Take a consultative approach Another way systems integrators are adding value is by offering vertical specialisation Installation fees remain important for many integrators, but there may be additional consultative opportunities to build long-term relationships with customers. Offer services such as roadmap planning, hardware and integration maintenance, training to certify end users on the manufacturer’s product, and cybersecurity services. While cloud-based solutions reduce on-premises maintenance, they don’t eliminate the need for ongoing support and training. Consider offering training opportunities. These can lead to other benefits as well. Better-educated and technically proficient customers are usually more willing to adopt new technologies. They understand the value of these investments and have more confidence that they’ll see results. Another way systems integrators are adding value is by offering vertical specialisation. Healthcare, sports venues, critical infrastructure, education, retail - each specialty has its own set of challenges, partner networks, regulatory restrictions, training needs, and business requirements. Integrators who specialise are uniquely positioned to offer key sector-specific insights that are invaluable to their clients. Embrace the cloud A key growth area for integrators is supporting customers in their shift to cloud deployments. Cloud solutions aren’t a one-size-fits-all solution. Each organisation is evaluating options and deciding whether cloud, hybrid, or fully on-prem solutions are the right fit for its unique needs. A key growth area for integrators is helping clients in their shift to cloud deployments Helping customers navigate and adopt cloud or hybrid solutions opens new opportunities to expand your business and deepen your relationship with your customers. Systems integrators who sell cloud solutions have the opportunity to add new layers to services for more value for customers. With a cloud solution that's easy and fast to deploy and managed and maintained by the provider, you can reduce overhead costs, staff training, and truck rolls via remote customer support. These benefits also allow you to spend time developing greater expertise in your customers’ processes. Using this knowledge, you can tailor your services towards potential productivity gains for your customers and turn them into additional sales. You ensure that your customers get the most out of the technology that’s available and that they have already purchased. Highlight your focus on cybersecurity Cybersecurity is no longer solely an IT department's responsibility. While dedicated IT security teams may still handle broader network defense, integrators play a crucial role in securing access control, surveillance, and IoT devices within a security framework. If unsecured, these devices can provide an entry point for cyber criminals to gain access to an organisation’s network. Cybersecurity is no longer solely an IT department's responsibility To best protect end users from cyberattacks, choose physical security systems with built-in security and privacy-by-design features. Help customers implement best practices to ensure their entire ecosystem is designed, built, and managed with end-to-end security in mind. Once implemented, work with your manufacturers, consultants, and end users to ensure that vulnerabilities are identified and mitigated. Every person on the network plays a role in keeping cyber threats at bay. Lean into the power of partnerships In today’s complex and dynamic security landscape, choosing the right technology partners is crucial. Ask potential partners to share their technology roadmap, and how you can offer feedback or participate in discussions about industry trends. Ideally, your partners will have a program in place to get input from integrators and end users, so they can develop products that are designed to address their most pressing issues and concerns. Your manufacturer partners should be working to help identify the evolving needs of customers and communicate these insights to systems integrators. Seek partners who actively support integrators to understand how security is evolving In addition to a good experience for the end user, strong manufacturer partners also offer solutions to streamline and automate workflows for integrators. It should be easy to order and check your shipping statuses online, for example. These are simple things that save you time and demonstrate your partner’s care for your business. Seek partners who actively support integrators to understand how security is evolving. While training is often offered on-site, some companies are now also offering blended learning models so integrators and their technicians can reduce classroom time and stay out in the field. Evolution is an opportunity Security integrators with traditional physical security expertise remain indispensable because they understand real-world risks and regulatory requirements. They can provide hands-on system deployment and optimisation. Now, there are new opportunities to build long term customer relationships. As the physical security industry undergoes this profound shift, adaptation is key. By embracing cloud and hybrid solutions, integrators can unlock new revenue streams, enhance customer relationships, and stay ahead of technological advancements. With the right partnerships and a forward-thinking mindset, systems integrators can navigate this transformation and take advantage of new opportunities being presented by evolving technology. Leverage your deep industry experience while upskilling in cloud, cybersecurity, and IT. The strongest approach is for end users, systems integrators, IT specialists, and manufacturers to work together to navigate industry changes.
In today’s world, almost any electronic security system holds the potential to become a gateway for cybercriminals. With physical security and cybersecurity increasingly entwined, security professionals aren’t doing their job unless they take all possible precautions to lock down unauthorised access to camera systems, access control platforms, intercoms, and other network-based security devices and solutions. Let’s explore the many steps companies should take throughout their security technologies’ lifecycle – from choosing a vendor all the way through device decommissioning – to avoid making the common mistakes that leave systems, and the networks they reside on, vulnerable to attack and sabotage. Prepurchase phase: Laying the groundwork for cybersecurity 1. Conduct a Vendor Risk Assessment IT departments often rely on the same Vendor Risk Assessment criteria they use for evaluating IT equipment manufacturers when considering the suitability of physical security vendors. While commonalities exist between how to assess these disparate solutions, there are also differences that require distinct scrutiny. For example, device endpoints within physical security systems run on custom Linux Kernels and therefore do not utilise standard Linux distributions like Red Hat, Ubuntu, or Debian. IT divisions often rely on the same Vendor Risk Assessment criteria they use for evaluating IT kit A comprehensive evaluation should examine how each security solutions manufacturer handles its software development life cycles. Ideally, vendors should adhere to a recognised framework when developing both their platform management and device-specific software. In 2021, Executive Order 14028 made it a bit easier for companies to evaluate vendors by providing guidelines for evaluating software security, the practices of the software developer, and methods to demonstrate conformance with secure practices, specifically referencing the NIST SP 800-218 Secure Software Development Framework. In short, a good vendor should have documentation that explains everything it’s doing to address cybersecurity from development, through releases and ongoing maintenance. 2. Obtain Software Update Schedules The frequency with which manufacturers update their software varies. Each company is different. If you’re their customer, it shouldn't matter whether the vendor schedules updates every six months, three months, or more often than that. What does matter is that you know what to expect and have a plan for how to deal with that reality. For example, if updates only occur every six months, under what conditions are patches released to address vulnerabilities that emerge between updates? Customers must understand how often they'll be updating the software on their devices and ensure they have the resources to make it happen. Make sure stakeholders agree, upfront, who will be performing the software updates. Will it be the integrator who installed the system, the physical security system staff, the IT team, or the end user? Keeping an entire system current is a huge challenge, but a non-negotiable responsibility. Manufacturers who don't issue frequent releases and patches put the onus on customers to handle mitigation efforts on their own. In these instances, IT departments must be prepared to employ network segmentation, firewalls, security whitelists/blacklists, and other methods to protect their systems until a patch is released. If a company's security team has typically updated firmware only when something breaks, these additional responsibilities most likely require greater collaboration with IT departments and a shift in how security systems are managed. 3. Know the Warranty Terms and Duration of Software Support Organisations should understand the warranty policies for the devices they purchase Organisations should understand the warranty policies for the devices they purchase. Even more important is knowing when a device's software support will expire. Software support should extend well beyond hardware coverage. For example, if a camera has a five-year hardware warranty, customers should reasonably expect an additional five years of software support. When that period ends, companies must plan on replacing the device – even if it still works well. Without software updates, the device lacks vulnerability support and becomes too risky to remain on the network. Manufacturers should be transparent about their warranty and software support policies, helping organisations plan for device replacements that align with cybersecurity needs. 4. Request a Software Bill of Materials (SBOM) During the pre-discovery process, customers should request a Software Bill of Materials (SBOM) that provides a detailed inventory of the software running on each device, including open-source components. By revealing what software is "under the hood," the SBOM allows IT departments to be vigilant in protecting the company's systems from exposed vulnerabilities. For example, a customer should understand how Transport Layer Security (TLS) is being handled to secure a security solution's web server if it’s an open-source component like OpenSSL. 5. Assess Vulnerability Disclosure Practices CNA manufacturers represent the gold standard in cybersecurity practices Understanding how a manufacturer handles vulnerabilities is essential. Ideally, they should be a Certified Naming Authority (CAN) and report common vulnerabilities and exposures (CVEs) to national vulnerability databases such as NIST and MITRE. Doing so automatically includes any disclosed vulnerabilities associated with their devices in vulnerability scanners' databases. CNA manufacturers represent the gold standard in cybersecurity practices, but most security manufacturers do not reach this level. At a minimum, the vendors you choose to work with should have an email notification system in place to alert customers to new vulnerabilities. Remember – email notifications are only as reliable as the employees managing them, so investigate whether the manufacturer has a strong track record of keeping up with such communications. Ask to speak with customer references who have been using the solution for an extended period to ensure the vendor is diligent in its communications. Configuration phase: Ensuring a secure setup 1. Use Hardening Guides Once a device is purchased, configuring it securely is the next critical step. Manufacturers should publish hardening guides that detail the security controls available for their products and recommended practices for implementation. Between the features offered by the vendor and your company's own cybersecurity policies, make sure all possible encryption options are activated. Using HTTPS is vital for ensuring secure communication with devices. Many physical security devices default to HTTP to accommodate customer-specific network topologies and certificate management. Failing to implement HTTPS can leave sensitive metadata unencrypted and vulnerable to interception. 2. Consider Advanced Encryption Protocols Protocols are necessary to protect video data in transit from cameras to the VMS Some solutions offer built-in encryption protocols, like MACsec, which makes it impossible for data to be compromised as it is transmitted over the network. HTTPS is still necessary to secure the connection to the devices’ webservice, but while customers set up and configure their devices, MACsec will keep network data safe. Additionally, if you want to encrypt video streams, consider protocols such as Secure Real-Time Transport Protocol (SRTP), which secures the transmission of audio and video data over the Internet, or tunnelling methods like Secure Socket Tunnelling Protocol (SSTP), which encapsulate data packets for safe transmission between two points, even if the network is insecure. Such protocols are necessary to protect video data in transit from cameras to the Video Management System (VMS). Encryption should also extend to the VMS hard drive where video is stored. There are different methodologies to do that, but ultimately the goal is to encrypt data in transit and in storage. 3. Implement Remote Syslog In the case of a breach, each device maintains a set of logs that are useful for forensic investigations. However, if a device gets hacked, its log may not be accessible. Best practices dictate that companies should set up a remote Syslog server that maintains a copy of all device logs within a central repository. In addition to providing redundant data for investigations, a Syslog offers IT systems an efficient way to look for anomalies. Cybersecurity teams will receive immediate notification for events like unsuccessful login attempts so they can quickly figure out what's happening. Who is trying to log in? Why on that particular device? 4. Practice Healthy Password Hygiene Ideally, organisations should move towards using Active Directory or Single Sign-On (SSO) solutions One of the most basic and yet overlooked aspects of cybersecurity is the failure to manage user accounts meticulously. Many organisations use the same username and password for all security devices because it's simply too cumbersome to manage a network of devices in which each requires a separate, unique login. It's assumed that the system's primary administrators are the only ones who know the universal password. However, the system becomes vulnerable if anyone within this select group leaves the company and the password isn't changed or deleted right away. Ideally, organisations should move towards using Active Directory or Single Sign-On (SSO) solutions. This approach ensures that employees throughout a company are each assigned a unique login credential that they use for any systems they use throughout the organisation. When they leave, their passwords and access are universally terminated along with their accounts. If SSO is not an option, regular password changes and prompt account deactivation are critical. Decommissioning phase: Securely retiring devices At some point, physical security devices will reach the end of their useful life. When that time comes, companies must take care in how they dispose of their devices. A good vendor will provide guidance on how to clear memory chipsets and restore factory defaults. Improper decommissioning can lead to severe risks. For example, if an improperly decommissioned device is sold on the secondary market or retrieved from a dumpster, an attacker could gain access to sensitive network configurations and use this information for malicious purposes. Conclusion Deploying physical security solutions involves more than just securing buildings and assets; it also requires robust measures to protect against cybersecurity threats. From assessing vendors and understanding update policies to configuring devices securely and managing decommissioning processes, each step presents potential pitfalls that, if overlooked, could expose organisations to significant risks. By incorporating the techniques discussed into their deployment protocols, organisations can ensure their physical security solutions provide comprehensive physical and digital protection.
Security beat
For all the emphasis on cloud systems and centralised servers at ISC West, a lot of innovation in security video systems is happening at the edge. New advancements inside video cameras are boosting capabilities at the edge, from advancements in processing power to artificial intelligence (AI) and machine learning (ML) algorithms that can now be deployed directly on the cameras or edge devices. Advancements in AI algorithms The progress of video systems becoming smarter at the edge is driven by the need for real-time insights, lower latency, bandwidth efficiency, enhanced privacy, and improved reliability. Advancements in edge computing hardware and AI algorithms are enabling a range of intelligent video applications across various industries, including physical security. Smarter functionality at the edge is a benefit of new computer systems-on-chips (SoCs) that are driving new heights of performance for today’s cameras. Axis Communications’ ARTPEC-9 Axis Communications’ new ARTPEC-9 SoC offers advanced video compression to reduce bandwidth Axis Communication’s new ARTPEC-9 system-on-chip (SoC) offers advanced video compression to reduce bandwidth and storage needs. With a low bitrate, the SoC helps deliver high-quality imaging with outstanding forensic detail. ARTPEC-9 also offers enhanced deep learning capabilities to allow users to leverage the latest video analytics and accelerate the implementation of AI technology. Axis maintains control over all aspects of the chip’s development to ensure high quality and cybersecurity. Among the benefits of ARTPEC-9 are better AI and deep learning, better image quality, better cybersecurity, and AV1 license-free video compression (see below). Hanwha Vision’s Wisenet 9 Hanwha Vision has launched Wisenet 9, its most advanced AI-powered System on Chip (SoC). Wisenet 9’s enhanced edge AI capabilities increase performance as the volume and complexity of security threats demand real-time, accurate analysis. By elevating edge-device performance, AI empowers systems to quickly analyse vast amounts of video data and discern crucial patterns and anomalies. A key differentiator driving Wisenet 9 is deployment of two Neural Processing Units (NPUs), which improve performance three-fold compared to Wisenet 7, the previous SoC generation. While one NPU handles image processing, the other focuses on object detection and advanced analytics. This dual NPU concept was introduced to ensure video quality and analytics have independent resources, thus preventing one function from impacting the performance of the other. The latest from Ambarella Ambarella is a supplier of edge AI systems-on-chips to multiple video camera manufacturers Off the ISC West trade show floor in a nearby meeting room, semiconductor company Ambarella demonstrated how it will continue to push the envelope of what is possible with generative AI at the edge. Ambarella is a supplier of edge AI systems-on-chips to multiple video camera manufacturers and recently achieved the milestone of 30 million cumulative units shipped. The demonstrations highlight Ambarella’s ability to enable scalable, high-performance reasoning and vision AI applications across its ultra-efficient, edge-inference CVflow 3.0 AI SoC portfolio. The company’s DeepSeek GenAI models run on three different price/performance levels of its SoC portfolio. In addition to advancements in GenAI processing at the edge, Ambarella integrates image processing, encoding and system-level functions into all its AI SoCs. New standard for video encoding: AV1 AV1 compression is a next-generation video coding technology that offers significant improvements in compression efficiency and video quality, especially at lower bitrates. Its royalty-free nature positions it as a crucial codec for the future of internet video. AV1 compression is a next-generation video coding technology. Axis Communication’s ARTPEC-9 chip now supports the AV1 video encoding standard. By embracing this standard, which is new to the physical security market although it was introduced in 2018, Axis sets the stage for AV1 compression to eventually become the industry standard, replacing H.264 and H.265. Network video transmission AV1 is an open-source, license-free coding format designed mainly for efficient network video transmission AV1 is an open-source, license-free coding format designed specifically for efficient network video transmission. It delivers high-quality video at low bitrates, reducing bandwidth consumption and storage costs. The codec was developed by the Alliance for Open Media (AOM), a nonprofit organisation founded in 2015 by Google, Intel, Amazon, Microsoft, Netflix, and Mozilla (among others), to provide open-standard, next-gen video coding technology. AV1 is ideal for cloud solutions—making streaming applications more robust, scalable, and capable of delivering real-time insights. Now the ARTPEC-9 chipset brings these benefits to the surveillance industry, and AV1 is currently supported by AXIS Camera Station. Providers of major video management solutions (VMS) such as Genetec and Milestone will be adding support for AV1, with further developments already underway. More intelligence at the edge Intelligence inside video cameras comes from the processing power and algorithms that enable them to perform tasks beyond simply capturing and recording images. This "intelligence" allows cameras to analyse the video stream in real-time, identify objects, detect events, and make decisions or provide alerts based on what they "see." New and improved SoCs are driving performance improvements at the edge. The increasing power of embedded processors and advancements in AI are continuously expanding the capabilities of intelligent video cameras.
AI has the potential to enhance the usability of traditionally complex access control and physical security systems. The application of AI (artificial intelligence) within access control is still relatively new, but rapid advancements in generative AI are already transforming how security systems operate. acre security is driving the deployment of generative AI in access control through its acquisition of REKS earlier this year. REKS is a purpose-built generative AI solution designed specifically for acre’s access control platform. Unlike generic AI tools, REKS understands both system and security-specific terminology, allowing users to ask natural-language questions like, “Show me all access denied events at a specific location,” and receive instant results. AI workflows and AI agents “We're starting to see how AI workflows and AI agents, that leverage language models, can potentially be used in conjunction with access control to create new, automated processes around false alarm reduction, system configuration, report generation, data analysis, threat detection, and in-system customer support,” says Adam Groom, Director of Business Development, AI Development Team, acre security. “We expect AI-driven capabilities to evolve rapidly, but the full range of benefits will depend on continued development and real-world application,” he adds. Integrate AI-driven capabilities acre’s ability to integrate AI-driven capabilities across the company’s product portfolio positions The best way to think of REKS is as an acre access control expert you can talk to, says Groom. “As AI adoption grows in security, REKS will expand its capabilities, making access control more usable and more efficient.” Groom says acre’s ability to integrate AI-driven capabilities across the company’s product portfolio positions the company as a pioneer in next-generation physical security. “These features will add long-term value by enhancing usability and operational insights across various segments,” says Groom. “Work is already under way to incorporate REKS into acre access control, and we’ll evaluate other integration opportunities in the future.” REKS' AI capabilities According to acre, REKS simplifies daily operations, automating routine tasks, and delivering real-time, actionable intelligence. With REKS' AI capabilities, users can interact with the system to retrieve more detailed insights and actionable information from their acre access control system. “This eliminates the need for complex reports, navigating drop-down menus, or manually reviewing logs,” says Groom. “It significantly enhances efficiency and usability for security professionals.” Enhancing productivity and customer satisfaction Key concern is ensuring that system configuration, enactment, and servicing remain within their scope For integrators, the key concern is ensuring that system configuration, implementation, and servicing remain within their scope of expertise. With REKS, that doesn’t change — but the process becomes significantly faster and more efficient. Instead of manually configuring every panel, input, and output — a traditionally time-consuming task — REKS enables integrators to use natural language commands to streamline setup and adjustments, says Groom. This eliminates tedious steps and dramatically improves operational efficiency, allowing integrators to deploy and fine-tune systems with greater speed and accuracy, ultimately enhancing both productivity and customer satisfaction, he adds. Cloud-enabled ecosystems “We are committed to helping organisations modernise their security infrastructure by transitioning from legacy systems to cloud-enabled ecosystems at their own pace — ensuring minimal disruption while maximising value,” says Groom. “By integrating AI-driven capabilities, we enhance usability and deliver deeper operational insights across all segments.” “Security’s future isn’t about forcing change — it’s about empowering choice,” adds Groom. “Whether staying on-prem, migrating to the cloud, or adopting a hybrid model, we plan to provide a seamless, zero-disruption transition, prioritising interoperability, automation, and security at every stage.” Generic AI tools AI must be purpose-built for security applications because security demands precision, reliability, and context-aware decision-making, which only focused AI offerings like REKS bring to the table, says Groom. In contrast, generic AI tools, like ChatGPT, are designed to perform a wide variety of tasks, like how humans can learn and do many different things. Instead, purpose-built AI is built to do just one specific function. “REKS adds specially designed artificial intelligence to our access control solutions to enhance both intelligence gathering and the user experience,” says Groom. New applications in access control The integration of generative AI into acre's access control platforms and their broader portfolio A new AI development team will lead AI initiatives at acre, driving the integration of generative AI into acre's access control platforms and their broader portfolio. This team will seek to push boundaries in applying AI to new applications in access control, intrusion detection, and beyond, empowering security professionals to interact with their systems in a smarter, more intuitive way. But don’t worry, AI will not take the human element out of security entirely. AI human capabilities “The reality is that AI will improve upon human capabilities because it is a versatile tool that supports and strengthens security operations, not a replacement for human decision-making,” comments Groom. “It helps operators process large amounts of data quickly and detect patterns that might be missed otherwise.” Rather than removing the human element, AI allows security teams to work more efficiently by automating repetitive tasks and providing actionable data, enabling professionals to focus on critical responsibilities. {##Poll1743085396 - What is the biggest challenge you face with your current access control system?##}

Casinos face multiple security issues caused by potential bad actors, everything from cheating to vandalism, from theft to vagrancy. A new intelligent technology can monitor for specific keywords and behaviours. The technology scans the entire casino premises constantly for potential threats and notifies key personnel when they happen. Casinos are among the environments deploying the OpticSense system by Huvr Inc., which uses special fibre optic technology called an interferometer to secure large areas. Imagine a very sensitive loop made of fibre-optic cables placed around the perimeter of a facility. System’s artificial intelligence Basically, it converts the entire facility into a highly sensitive microphone, detecting any slight disturbances, such as an unusual movement or sound. When the system senses something out of the ordinary, it immediately triggers cameras to look at the disturbance and record a short video. The system’s artificial intelligence (AI) then analyses both the sound and video to determine what's happening. It compiles a detailed report and immediately sends the information to security teams. OpticSense OpticSense can hear, see, and analyse potential threats automatically before they get out of control. “This makes it possible for fewer people to do more,” says Herman C. DeBoard III, CEO and Founder of Huvr Inc, adding “When you don’t need as many personnel to monitor video feeds and analyse data, you can drastically reduce your labour costs. Best of all, when you optimise your resource allocation, your security teams can respond more effectively to each threat.” The system’s AI analyses sound and video to define what's happening. Combining fibre optics and AI Huvr was originally designed as a platform to provide immersive virtual travel experiences Huvr was originally designed as a platform to provide immersive virtual travel experiences. However, with the acquisition of OpticSense and Grip Places, the company pivoted to integrate advanced fibre-optic technology and AI-driven analytics into a comprehensive security system. The system’s artificial intelligence and fibre-optic interferometer technology work together to detect and analyse real-time threats. When the Fibre Optic Ring Interferometer (FoRi) detects even minute audio abnormalities, it triggers AI analysis. In split seconds, the AI directs cameras to record 60 seconds of video, compiles a detailed report, and then texts the real-time intelligence to security teams and authorities. Intelligent security solutions The growing need for intelligent security solutions can help to drive Huvr's entry into the security marketplace. Advanced technology enables the company to meet the increasing concerns surrounding public safety and the growing need for real-time threat analysis. The AI system classifies each detected anomaly according to its severity and stores data from various incidents to improve its risk assessment abilities over time. This continuous learning enables the AI to become more adept at accurately identifying and responding to threats specific to the casino environment. AI system classifies each detected anomaly according to its severity. Simple and discreet installation The system involves installing fibre optic cables around the casino’s perimeter The system involves installing fibre optic cables around the casino’s perimeter. It’s a simple job that typically requires less than a day. “These cables allow the casino to establish a smart perimeter detection system without significant infrastructure alterations,” says DeBoard Casinos typically employ upwards of 6,000 cameras, but human security teams cannot feasibly monitor all the incoming data at once. Huvr's OpticSense product becomes like the brain of the casino, constantly monitoring disturbances and responding in real time. Huvr’s fibre optic cables Huvr’s advanced detection algorithms work in tandem with a casino’s existing camera infrastructure, simply adding a layer of security that converts traditional security measures into an intelligent system that continuously monitors and analyses video footage. With Huvr’s fibre optic cables easily hidden or buried and the server roughly the size of a shoe box, the system is designed to be extremely discreet. It can be operated by a single person using a small handheld device. The security system is simple to scale and manage without disrupting casino operations. Security system is simple to work without disrupting casino operations. Autonomy boosts productivity Huvr automates surveillance and anomaly detection to decrease the load on security teams Autonomy is an important aspect of this new technology. Traditional security systems have required constant human monitoring, but Huvr automates surveillance and anomaly detection to decrease the load on security teams. “Without any human direction, Huvr detects minute disturbances, triggering the AI system to direct cameras and analyse video footage instantaneously,” says DeBoard. He adds, “The intelligent system rapidly monitors every anomaly and accurately decides which present potential threats. When it detects an issue, it compiles a detailed report that includes the number of individuals involved, their appearances, direction of movement, and licence plates. It takes only seconds to text this report to security teams and authorities.” Applications beyond casinos Beyond casinos, Huvr already provides proactive security in a wide variety of settings. In banks, the system monitors parking lots and ATM machines for suspicious activity. In large stadiums, it proactively detects target words such as “help” or “gun.” In schools, Huvr’s fibre optic ring interferometer secures campuses against unauthorised intrusions. In hospitals, it alerts medical staff when patients need immediate care. In airport terminals, it monitors for suspicious behaviour. In restaurants or construction sites, the system learns to monitor for safety violations and health hazards. Smart perimeters around critical infrastructure The fibre optic cables also form smart perimeters around critical infrastructure like power grids, cell towers, and bridges to watch for physical disturbances or tampering. “Because the system can be customised to each new environment and can learn quickly, the applications are virtually limitless,” says DeBoard. {##Poll1728555696 - Do you believe AI-driven perimeter detection systems will significantly reduce security labour costs?##}
Case studies

Securitas discovered serious threats aimed at a top executive of a global corporation, both in their professional and personal life. Addressing these challenges requires urgent and proactive measures to safeguard both the executive and the organisation from harm. The challenge Securitas discovered serious threats aimed at a top executive of a global corporation, both in their professional and personal life. These threats put their work and home life in jeopardy. What's more, Securitas found signs that the culprits were planning to take action during a crucial business period to cause maximum disruption. Adding to the complexity, Securitas uncovered an insider threat perspective, meaning the culprits could exploit someone with insider knowledge and access to harm the executive and the entire organisation. The threats targeting the executive client posed serious risks - safety concerns for themselves and loved ones, damage to their reputation and that of the organisation, and disruption of crucial business operations and a major announcement. Addressing these challenges requires urgent and proactive measures to safeguard both the executive and the organisation from harm. The solution Securitas swiftly notified their client and promptly launched an extensive assessment into the threat. Additionally, Securitas provided Protective Intelligence services, conducting a comprehensive defensive screening assessment for the Executive, identifying potential vulnerabilities that could be exploited by threat actors. Utilising the insights gleaned from these investigations, Securitas collaborated with their protective services to fortify the principal's safety and safeguard the organisation from disruption. The measures included: Bolstering security protocols to safeguard the Executive's professional and personal information. Implementing continuous monitoring of the Executive's online presence and activities for any red flags. Strengthening executive protection measures, such as providing escorts and regular check-ins. Offering lone worker solutions equipped with alarm and tracking functionalities. Enhancing operational security by disseminating threat briefings, including indicators and warnings, to relevant personnel. Coordinating with authorities as necessary to address the threat effectively. Conducting awareness communications to educate key stakeholders on personal threats, workplace violence and insider threats and risks. The result Through the effective integration of intelligence-driven security measures and Securitas' renowned protective services, the collaborative efforts with this client yielded profound results, offering unparalleled protection to the Executive during a critical business phase. This approach not only ensured the safety and well-being of the principal but also instilled a sense of reassurance and confidence throughout the organisation. By leveraging cutting-edge intelligence capabilities, Securitas proactively identified and mitigated potential threats, thereby safeguarding the Executive's interests and preserving operational continuity during a pivotal business period. This comprehensive strategy not only mitigated immediate threats and associated risks but also established a robust framework for ongoing security resilience. In essence, the successful implementation of their solution epitomises the transformative impact of intelligence-led security, fostering a culture of proactive risk management and instilling a sense of confidence in their client's ability to navigate challenges effectively.

Cognitec Systems Pty Ltd is working with Home Affairs Australia to deliver 250 camera devices for facial image capture, image quality check, and traveller identity verification at all major international airports in Australia. With approximately 41 million international travellers entering and leaving Australia each year, the Department uses facial biometrics to collect and electronically verify the identity of eligible international travellers. Cognitec hardware and software systems Cognitec’s capture device, FaceVACS-Entry, detects the person’s height, automatically adjusts the camera position to capture a frontal pose photo, and uses automated face recognition to verify person identity. Cognitec is also providing integration software, mounting hardware, device installation services, as well as ongoing support and maintenance services for all Cognitec hardware and software systems. Relationship with the Department of Home Affairs “Cognitec is proud to continue a successful relationship with the Department of Home Affairs, and to deliver our technology for quick collection of biometric photos and for accurate traveller verification at the Australian border primary lines,” says Terry Hartmann, Cognitec’s Vice President Asia Pacific, adding “This project contributes to the security and ongoing digitisation of the Australian border, ensuring trusted traveller identities.” FaceVACS-Entry is used by governments worldwide for applications that require the acquisition of standards-compliant photos, and the verification of a live image against reference images, such as access control, border control, and entry/exit programs.

Furnaces play a critical role in refining and petrochemical operations, providing the high temperatures required for essential processes. When they fail, the consequences can be severe both in terms of safety and operational losses. A single day of unplanned downtime can result in losses exceeding $1 million. This is why companies like PROtect, under the leadership of Jason Czajkowski, are leveraging modern infrared (IR) technologies to conduct smarter, safer, and more cost-effective furnace inspections. Evolution of IR furnace cameras IR technology in furnace inspections has evolved significantly over the past three decades. Early tools like the Agema 550 and Inframetrics 390 laid the groundwork for remote temperature diagnostics in extreme environments. These early cameras were bulky and required extensive setup, but opened the door to non-contact thermal inspections. Real-time thermal imaging FLIR’s GF309 became the workhorse of the industry, offering real-time thermal imaging through flames Later, FLIR’s GF309 became the workhorse of the industry, offering real-time thermal imaging through flames with improved ergonomics. However, the GF309’s 320 × 240 resolution limited its ability to detect fine anomalies, especially at a distance. Czajkowski recognised the need for greater clarity and transitioned PROtect to the FLIR G609, which features a 640 × 480 detector. This allows PROtect technicians to detect smaller anomalies such as hot spots, coke buildup, or insulation breakdowns earlier and from safer distances. Introducing the FLIR G609: A smarter tool for a safer job The G609 represents the latest in FLIR’s IR camera evolution. It is built specifically for high-temperature applications and comes equipped with a re-engineered heat shield, factory-calibrated furnace lens, and a modern touchscreen interface. PROtect’s field teams report that the camera’s intuitive controls and robust design make it a reliable tool in even the harshest conditions. With its increased resolution, the G609 can accurately measure temperatures on narrow furnace tubes deep within radiant sections, something older models struggled with. "It’s not just clearer images," Czajkowski explains, "It’s better decisions, faster." Complete solutions: Pairing the G609 with software With the Route Creator tool, inspections are no longer reactive they’re pre-planned and executed with precision What truly transforms the inspection process is the integration of FLIR’s Thermal Studio Pro software. With the Route Creator tool, inspections are no longer reactive they’re pre-planned and executed with precision. Technicians follow a defined route with inspection points loaded into the camera, eliminating guesswork and ensuring consistency. Manual sorting and documentation After inspections, images are automatically organised by inspection point, and reports are generated in minutes using professional templates. This saves countless hours of manual sorting and documentation, freeing up inspectors to focus on analysis and decision-making. According to Czajkowski, "This combination of camera and software creates a seamless workflow from planning to reporting." Real-world results: Safer plants, better uptime Early detection of a developing hot spot let a refinery to schedule a repair during planned downtime By adopting the G609 and an integrated software approach, PROtect has helped clients detect issues like burner misalignment and developing coking conditions early, preventing costly shutdowns. In one instance, early detection of a developing hot spot allowed a refinery to schedule a repair during planned downtime avoiding an emergency outage and saving hundreds of thousands in potential losses. Conclusion Infrared furnace inspections have matured from a specialty technique to an essential maintenance strategy. With modern tools like the FLIR G609 and expert leadership from professionals like Jason Czajkowski, PROtect is setting new standards for asset reliability. IR inspections now provide not only sharper thermal images but also faster workflows, greater safety, and measurable ROI. As Czajkowski affirms, "We’re not just taking pictures we’re delivering solutions that protect assets, budgets, and people."

The Link School of Business provides education and training through innovative teaching methods and practical approaches focused on the application of knowledge to create new businesses. Located at the heart of São Paulo, Brazil, this educational institution, established in 2020, is home to both aspiring entrepreneurs and experts in the field. With its mission to positively impact the world by transforming education, offering cutting-edge educational facilities that are safe and conducive to learning is imperative for this dedicated college. Challenges Safeguarding a modern 6-storey building is not an easy task. Monitoring the safety of students and school staff at all times is of utmost importance. Access control must be in place in order to regulate the flow of people and vehicles entering and leaving the school premises. In terms of classroom optimisation, several aspects must be achieved such as automatic attendance, behaviour analysis, usage of interactive whiteboards for collaboration, and more. Integration with third-party software and hardware is also difficult and challenging to accomplish. Access control must be in place in order to regulate the flow of people. Solution In order to create a secure and innovative learning environment and provide intelligent and real-time learning experience to its students, Link School of Business partnered up with Dahua and deployed the Dahua Smart Education Solution around its campus. ANPR access cameras and bracket cameras were set up at the parking lot of the school to automatically recognise authorised vehicles and monitor the area 24/7. ANPR access cameras and bracket cameras were set up at the parking lot. Face recognition terminals At the entrance, intelligent turnstiles with face recognition terminals were installed to instantly recognise authorised people and efficiently streamline access to the building. In common areas such as hallways, lobbies and stairways, 3MP behaviour cameras equipped with video metadata algorithms were strategically installed to accurately recognise students’ non-recurring activities to help prevent accidents (e.g., fall) from happening. It can also predict crowd formation and conflicts among students in real time. 3MP behaviour cameras equipped with video metadata algorithms. Dahua DeepHub smart interactive whiteboards Dahua DeepHub smart interactive whiteboards offer an artillery of academic tools and features In the classrooms, the Dahua Smart Education solution goes beyond monitoring. It enables automatic attendance by recognising the students that are present in the classroom, as well as those who are late or left the class before it ends. The Dahua DeepHub smart interactive whiteboards offer an artillery of educational tools and features to boost learning and collaboration in the class. It can also connect students’ computers and transmit lecture content to other rooms or locations in real time. What’s more, intelligent cameras installed inside the classroom can also recognise students’ behaviour such as exchanging items during an exam, using mobile phone, and even sleeping during a class session, informing the teacher about such actions and enabling them to act accordingly. Results The Dahua Smart Education Solution successfully redefines education and security at Link School of Business by connecting students, teachers and lecture content in an innovative and interactive way, while also ensuring their safety and security at all times. It offers an intelligent high-tech system that strengthens learning experience, innovates teaching methods, and sets new security standards in the school. Dahua Smart Education Solution successfully redefines education and security. Innovation and technology “Innovation and technology are very important to us. Alongside pioneering companies like Dahua, we seek to create a very favourable environment to showcase everything that is state of the art (such as) campus access and classroom cameras,” says Alvaro Schocair, Founder and Chairman of the Executive Board of Directors of Link School of Business. “Our main goal is to provide students and teachers with the best possible ecosystem so they can create products, develop service, build their companies, and through their organisations, improve society and make the world a better place,” he added.

Iveda®, a pioneer in AI-driven video surveillance and smart-city technologies, announced that Subic Sun Development, Inc. has chosen the IvedaAI™ platform as the video surveillance solution for the soon-to-open Subic Sun Resort, Convention & Casino. IvedaAI was selected early in the build-out to inform camera placement and ensure frictionless integration with future-ready, AI-powered analytics. Focus on safety and service Located on the former U.S. naval base in the Subic Bay Freeport Zone—a special economic hub that hosts thousands of international and local businesses—the resort will feature 500 guest rooms, a state-of-the-art convention centre, a luxury casino, and two Accor-brand hotels, Ibis Styles and Mercure, scheduled to open in December 2025. The decision comes as global resort operators sharpen their focus on safety, service and operational efficiency. The global resort market generated $347 billion in 2024 and is projected to reach nearly $945 billion by 2030, an 18.5% CAGR. IvedaAI’s AI-enabled video analytics IvedaAI’s AI-enabled video analytics will help property staff lower security costs, respond to incidents faster IvedaAI’s AI-enabled video analytics will help property staff lower security costs, respond to incidents faster and unlock data-driven insights that boost both guest satisfaction and bottom-line performance. “Iveda being selected as a premier security and surveillance provider before the first Subic Sun Resort guest ever checks in is a powerful endorsement of our commitment to providing state-of- the-art monitoring technology,” said David Ly, CEO and Founder of Iveda. IvedaAI’s real-time analytics Ly added: “By designing camera layouts around IvedaAI’s real-time analytics, Subic Sun can optimise coverage, reduce blind spots, and deliver safer, smoother guest experiences—without a costly equipment overhaul. We expect more ground-up projects to follow this blueprint.” Iveda Philippines—Iveda’s joint venture focused on nationwide smart-city deployment—secured the Subic Sun contract and will oversee the on-site rollout. The win represents the team’s first major hospitality project and advances its plan to generate US$ 3 million in smart-city revenue by FY 2026, building on the broader initiative it announced last year.

Comelit-PAC has successfully upgraded the access control infrastructure at Blackpool Victoria Hospital, ensuring a seamless and secure environment for staff, patients, and visitors. Blackpool Victoria Hospital is one of the largest and busiest hospitals in the Northwest, providing essential healthcare services to thousands of patients each year. As a pioneering medical facility, ensuring a secure and efficient environment is a top priority. Integrated PAC Access Central Security technology works programme integrated PAC Access Central with multiple PC workstations Designed to provide a robust and scalable security solution, the security technology works programme integrated PAC Access Central with multiple PC workstations for comprehensive global administration across the hospital’s network To safeguard critical areas within the hospital, Comelit-PAC’s advanced 500 series controllers were utilised. This includes the 511, 512 model door controllers linked into the existing 500 Access & Alarm servers on site, offering a mix of ethernet and RS485 connectivity to enhance system flexibility and efficiency. Security and administrative control Martyn McKechnie, Head of Digital Identity at Blackpool Victoria Hospital, commented: "As a busy hospital with multiple departments and critical areas, we required an access control system that could integrate seamlessly while offering high levels of security and administrative control." Martyn McKechnie adds, "PAC Access Central provides the scalability and reliability we need to manage hospital-wide access efficiently. The ability to oversee all access points from multiple PC workstations ensures our Digital Identity and Security teams can respond quickly to any situation." Future-proof access control system Blackpool Victoria Hospital benefits from a resilient and future-proof access control system A key element of the installation is its server-based architecture, providing enhanced security measures and fail-safe redundancy. This ensures Blackpool Victoria Hospital benefits from a resilient and future-proof access control system, capable of meeting the bespoke demands of the healthcare environment. Advanced security infrastructure Jason Sullivan, PAC/GDX Strategic Development Manager at Comelit-PAC, said: "We worked closely with Blackpool Victoria Hospital right from the initial specification stage to deliver a solution to balance security with ease of management." Jason Sullivan adds, "PAC Access Central presents a future-proof system that allows the hospital to maintain strict access control, while adapting to evolving needs. By adopting this advanced security infrastructure, Blackpool Victoria Hospital continues its commitment to maintaining a safe and secure environment, leveraging Comelit-PAC’s expertise in access control technology."
Products
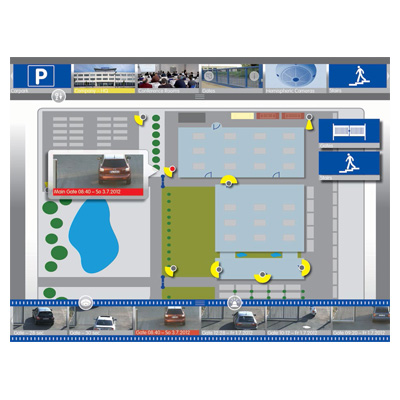
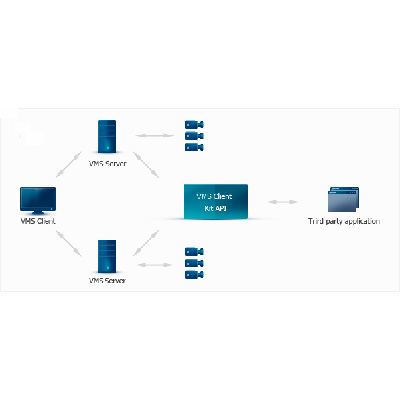


Round table discussion

Future-proofing your skillset is about embracing continuous learning and developing a versatile set of competencies that remain valuable regardless of technological shifts or industry changes. In the security marketplace, it is not about predicting the exact jobs of the future, but rather equipping yourself to adapt and thrive in the uncertain security landscape. But where to begin? The emerging technology shifts in the security industry provide clues, such as the growing importance of cybersecurity and artificial intelligence (AI). We asked our Expert Panel Roundtable: How can physical security professionals “future-proof” their skillsets to prepare for emerging technologies?

Access control, video surveillance, and intrusion detection systems evolved largely independently in the physical security industry. Integrating those systems to the benefit of an enterprise's overall security has traditionally fallen on security integrators working in cooperation with manufacturers. However, today's market has also evolved to include companies that provide "unified platforms,” bringing together various disparate security systems and functions under a single, centralised management interface. We asked our Expert Panel Roundtable: What are the advantages of installing physical security systems as a unified platform?

In the past, security installers and integrators were used almost exclusively to install hardware. However, the role is changing and expanding along with the technologies used in the physical security industry. Nowadays, an installer or systems integrator is much more likely to use a strategic, IT-centric, and data-driven approach. To gain additional insights, we asked our Expert Panel Roundtable: How is the role of the security installer/integrator changing?
White papers

Modernising higher education physical security
Download
Hospital safety in a high risk world
Download
The user-centric security revolution
Download
Unlocking smarter decisions with key control
Download
Combining security and networking technologies for a unified solution
Download
The power of integration in physical security systems
Download
Integrating IT & physical security teams
Download
Top 7 trends to watch in the physical security industry
Download
Boost efficiency and streamline security with integrated access control
Download
Video technology strategies for hospitals are moving beyond security
Download
IoT connectivity
Download
Creating a secure and positive healthcare experience
Download
Unified physical security
Download
Integrated access control: reap the benefits of connected security
Download
Getting the most value from Software Subscription Agreements
DownloadVideos


Integration software: Manufacturers & Suppliers
Modernising higher education physical security
Download
Manufacturing and industrial end users
Download
Strategic approaches to protecting healthcare clinics
Download
Technology's role in securing banks and financial institutions
Download
Security technologies promote real-time awareness in K-12 schools
Download