SwiftConnect - Experts & Thought Leaders


Latest SwiftConnect news & announcements

SwiftConnect, the connected access network for places and spaces, announces that international law firm Watson Farley & Williams (WFW) has launched company badges across major digital wallets for mobile-only access at its new London office at 25 Moorgate. As WFW prepared to relocate, more than 450 of their lawyers and staff were provisioned with a mobile credential ahead of their move-in. “Using mobile access at 25 Moorgate from day one is another example of how Watson Farley & Williams is investing in forward-thinking technology across the firm,” said Steven Bridger, Global Head of IT Projects and Change at WFW. “Working with SwiftConnect meant we could give our people an easy and secure way to access the building using their Apple and Android devices versus fumbling for a plastic badge at the turnstile, office doors, smart lockers and printers.” Access control system SwiftConnect’s connected access network integrates the firm’s IT and access control systems, HID credentials and readers, and the mobile app for an effortless Street-to-Seat® experience: WFW employees can now access everything from the base building lobby turnstiles to office spaces and lockers with Vecos Adaptive Workplace Storage technology–all using their mobile devices. Phoenix Trescray led the installation and configuration of the firm’s access control system in their new building. “Watson Farley & Williams wanted a mobile wallet and Street-to-Seat access experience done properly, and we are glad they turned to SwiftConnect, putting WFW among other security-conscious enterprises who look to us to deliver intuitive and modern solutions,” said Brandon Arcement, Vice Chairman at SwiftConnect. Self-service access experience “Our connected access network enables an on-demand, self-service access experience that removes friction for employees and frees security administrators from time-consuming, manual processes.” The deployment contributes to the firm’s vision to create a technology-first, experience-driven workplace, while advancing their sustainability goals–empowering them to remotely issue and revoke digital passes versus printing and manually managing plastic cards.

SwiftConnect, the connected access network for places and spaces, announces that international law firm Watson Farley & Williams (WFW) has launched company badges across major digital wallets for mobile-only access at its new London office at 25 Moorgate. As WFW prepared to relocate, more than 450 of their lawyers and staff were provisioned with a mobile credential ahead of their move-in. “Using mobile access at 25 Moorgate from day one is another example of how Watson Farley & Williams is investing in forward-thinking technology across the firm,” said Steven Bridger, Global Head of IT Projects and Change at WFW. “Working with SwiftConnect meant we could give our people an easy and secure way to access the building using their Apple and Android devices versus fumbling for a plastic badge at the turnstile, office doors, smart lockers and printers.” Manually managing plastic cards SwiftConnect’s connected access network integrates the firm’s IT and access control systems, HID credentials and readers, and the mobile app for an effortless Street-to-Seat® experience: WFW employees can now access everything from the base building lobby turnstiles to office spaces and lockers with Vecos Adaptive Workplace Storage technology–all using their mobile devices. Phoenix Trescray led the installation and configuration of the firm’s access control system in their new building. “Watson Farley & Williams wanted a mobile wallet and Street-to-Seat access experience done properly, and we are glad they turned to SwiftConnect, putting WFW among other security-conscious enterprises who look to us to deliver intuitive and modern solutions,” said Brandon Arcement, Vice Chairman at SwiftConnect. “Our connected access network enables an on-demand, self-service access experience that removes friction for employees and frees security administrators from time-consuming, manual processes.” The deployment contributes to the firm’s vision to create a technology-first, experience-driven workplace, while advancing their sustainability goals–empowering them to remotely issue and revoke digital passes versus printing and manually managing plastic cards.
SwiftConnect, provider of the connected access network for places and spaces, announces the acquisition of HID’s Workforce Business Unit, including HID SAFE, the platform for automating identity lifecycle management in the physical world. The combination addresses a problem every large organisation faces. When someone joins a company, changes roles, or leaves, their physical access permissions should update automatically, everywhere, in real time. In most organisations today, that process is manual, fragmented, and unreliable because IT manages digital access while a separate team manages physical access, and the two systems rarely communicate. The result is friction, audit exposure, and access that persists long after it should have been revoked. Physical access governance SwiftConnect's AccessCloud platform connects identity providers, mobile credentials, and access control systems across buildings, campuses, and portfolios. HID SAFE manages the governance layer, automating access requests, approvals, policy enforcement, and revocation based on changes in HR, IT, and security systems. Together, they deliver a single platform for physical access governance that covers the full arc: who someone is, what they are authorised to access, how they access it, and what happens when their role changes. "Access should be invisible for users. They are easily credentialed, they walk in, and nothing gets in their way. The addition of HID SAFE enables governance that makes this possible. The policies, approvals, and compliance requirements will now all live in the same platform as the experience,” said Matt Kopel and Chip Kruger, Co-CEOs of SwiftConnect. “Every person will get exactly the access they are entitled to, and just tapping to access buildings, doors, floors, and resources will be effortless.” Security-driven organisations “HID SAFE has earned the trust of the world’s most security-driven organisations for more than two decades. Great technology deserves the space to reach its full potential, and SwiftConnect is the right partner to take it there,” said Björn Lidefelt, EVP and Head of HID. For existing SwiftConnect customers, the acquisition delivers enterprise-grade physical access governance capabilities natively integrated with AccessCloud. For existing HID SAFE customers, their governance platform is now backed by SwiftConnect’s cloud-first, connected access infrastructure that networks existing physical access systems with cloud, identity, and mobile technologies. Connected access network Shane Butler, EVP of Identity at SwiftConnect, has recently joined the company to lead the SAFE business and drive the evolution in physical access governance. "This acquisition accelerates the modernisation of SAFE by delivering it via our connected access network so organisations can manage physical and digital access through the same governance, risk, and compliance lens. This is the moment when these two worlds will finally speak the same language, and being a part of this industry transformation is precisely why I joined SwiftConnect,” Butler said. The transaction builds on HID’s prior participation in SwiftConnect’s Series B funding round. HID will hold a minority, non-controlling interest in SwiftConnect following close. SwiftConnect is an independent company, controlled and managed by its existing leadership team.
Insights & Opinions from thought leaders at SwiftConnect

Most organisations operating at enterprise scale have more or less solved digital identity, consolidating directories, adopting single sign-on, and automating the workflows that govern application access, so that provisioning follows role changes and access revokes when employment ends. It is, by any measure, one of the more quietly impressive feats of enterprise IT over the past decade. Physical access has generally not followed, which creates exposure that rarely surfaces until an audit or an incident forces the issue. Also, it is fragmented across buildings, running on different access and identity systems that do not connect to each other. Visitor management platforms The friction that arises from the different approaches to physical and digital access shows up in predictable places: an employee who joins on Monday and waits days for a badge, and a contractor whose data centre access depends on someone manually emailing building security. Additionally, visitor management platforms do not always link to the access control systems that allow visitors through the door. Every link in that chain for employee or temporary access adds coordination work that falls between IT, HR, facilities and security teams with no clear owner. Most of these organisations have already invested heavily in the identity systems that could close this gap, but only ever applied them to digital access. Why the obvious fix doesn't work The usual answer to physical access fragmentation is standardising on a single vendor The usual answer to physical access fragmentation is standardising on a single vendor, which is unrealistic as users rely more on their own mobile devices for access, and ripping and replacing access infrastructure is simply too expensive and disruptive to day-to-day operations for most organisations. This puts physical security at the crossroads IT faced a decade or more ago, where neither standardising nor replacing systems is a realistic option. The result is an infrastructure that is vendor-dependent at every layer and disconnected from the identity and IT systems managing every other enterprise resource. Mergers and acquisitions complicate this further, since a company that has standardised on one access control platform can acquire an organisation that is using entirely different solutions and technologies across numerous properties. Enterprise tenants face a version of the same problem when leasing office space in a commercial real estate property, given that the offices, doors and floors they manage sit inside the landlord's base building infrastructure that controls access to lobby turnstiles, lifts, and shared spaces. Access control platform The result of all this fragmentation is manual provisioning, fractured audit trails and a poor user experience. For example, when an employee moves between offices, provisioning falls to administrators at each site, who often don't have visibility into the access that person already has elsewhere. The employee doesn't know who to contact, and security teams usually have to check several databases to answer basic audit questions. Information such as who currently has access to a given facility and which doors a specific employee can actually open exists across systems with no consolidated view. Contractor access occupies its own complicated middle ground that can create gaps in governance Contractor access occupies its own complicated middle ground that can create gaps in governance, with some contractor data residing in corporate directories that do not assign expiration dates. In other cases, contractors may be operating entirely outside identity systems while holding long-term credentials that are supposed to activate and deactivate based on when they are actually on site (but in practice they rarely do). The integration layer physical security was missing What resolved this kind of fragmentation in the IT space was a neutral technology layer capable of enforcing consistent identity logic across disparate systems. A connected access network applies that same principle to physical security, integrating access control systems, readers, mobile technologies, workplace applications and identity platforms, allowing access permissions to follow identity. Because the network is vendor-neutral, organisations can use physical cards, mobile wallets and visitor credentials side by side without becoming locked into proprietary infrastructure. Users wanted to adopt it, since streamlining authentication removes friction they noticed every day Like single sign-on (SSO) for applications, the network enables a consistent experience without requiring organisations to replace existing readers, systems, and technologies. The user experience is a main reason for SSO becoming so popular for digital access. Users wanted to adopt it, since streamlining authentication removes friction they noticed every day. For security teams, the single authentication layer also meant that when someone leaves the organisation, their access ends across every connected system at the same moment. Physical access infrastructure The same logic extends to physical security, where identity governance determines access to doors, floors, spaces and resources, with entitlements added, updated or revoked as joiner, mover and leaver status changes. Where an organisation's physical access infrastructure spans multiple vendors and buildings, the network handles permissions, credentials and policy enforcement centrally, without requiring costly replacement. Such an approach fits the reality of most deployments, which depend on leveraging systems that are already installed. It is also especially important in the UK and broader EMEA, where reader certification processes and the interoperability burden of managing multiple access control systems have, in some cases, contributed to slower wallet adoption. Beyond physical access, the value of the network grows when it connects to the platforms that enterprises already rely on for identity and workplace management. Enterprise service management platforms ServiceNow as a proof point: access requests in the same workflow as everything else Many large organisations already run enterprise service management platforms like ServiceNow across workplace operations and employee experience, handling everything from desk reservations, ticketing, and equipment requests to facilities management and identity lifecycle workflows. Yet physical access, arguably the most fundamental workplace requirement, has traditionally remained outside those workflows. The same employee who requests access to software or orders new hardware through ServiceNow still has to email the building security team to get through a door. When a connected access network integrates with ServiceNow, the physical access request enters the same workflow used for everything else. The employee submits through the portal, the request routes to the right approver based on rules the organisation defines, and access provisions automatically to the employee's credential on approval. Permissions revoke at the end of the approved period without manual follow-up, all within the governance frameworks already in place for digital resources. Dedicated request form The workflow doesn't have to originate from a dedicated request form, since meeting invitations The workflow doesn't have to originate from a dedicated request form, since meeting invitations, desk bookings, and travel itineraries can all trigger the same provisioning process in the background. As a result, access is already in place for the employee based on their activity, without the need for separate requests. With ServiceNow's Action Fabric now opening the platform to any AI agent through a generally available MCP server, that request can equally come from Now Assist, Claude, Copilot, or an agent the organisation has built itself. For security and compliance teams, the value extends well beyond provisioning, with the connection between access control systems and ServiceNow enabling a broader set of capabilities that include: Anomaly detection across physical and digital behaviour, surfacing events like a laptop authenticated in New York while a badge is used in London Occupancy analytics drawn from actual access events, giving facilities teams reliable data to support space planning and return-to-office decisions Automated recertification on a defined schedule, helping prevent privilege creep and overly broad birthright access, with every decision logged in ServiceNow for an audit-ready trail under standards including ISO 27001 Where the industry is heading Physical and digital access workflows have been converging gradually for years, driven by employee expectations shaped by digital-first experiences in every other area of working life. The organisations furthest along in addressing the gap are those that connected their physical and digital environments through a unified identity layer, allowing existing systems to keep controlling doors, floors, spaces and shared resources while one identity works across every building. Workplace systems and AI assistants can increasingly drive permissions in the background As workplace applications, identity platforms and physical infrastructure become more closely connected, access is likely to become less about badges and individual systems and more about identity following people automatically. Workplace systems and AI assistants can increasingly drive permissions in the background, with credentials delivered to employee and visitor devices before they even arrive to create seamless experiences across buildings, devices and applications regardless of the underlying infrastructure. Creating seamless experiences This is also where physical access starts to meet the zero trust principles already governing enterprise IT, where trust is never implicit and permissions are verified continuously against role, location and time. Employees, contractors and visitors get access only to areas they need, and because those entitlements adjust automatically, access is effortless for users and oversight is continuous for security teams. The conditions driving this shift are already in place: multiple systems and technologies across numerous locations have made managing access building by building untenable, while scrutiny around governance continues to tighten. Organisations throughout the UK and Europe know these pressures well, and large enterprises everywhere are arriving at the same place — physical access is finally becoming part of the same identity infrastructure that manages IT resources across the enterprise.
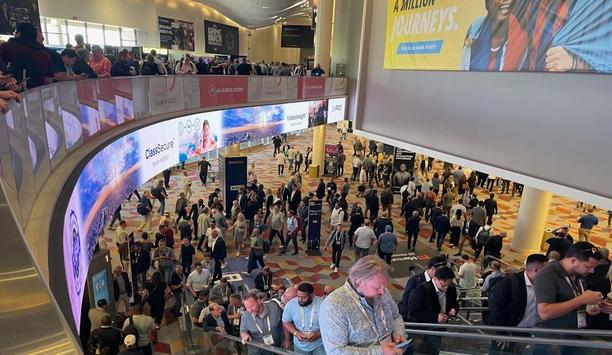
The security landscape is undergoing a profound transformation, as evidenced by the innovations showcased at the ISC West Expo 2026. From dismantling of silos between physical and digital security to the ongoing transition to cloud and hybrid platforms, much of the discussion on the show floor was familiar, if somehow more urgent than ever. Clearly the industry is moving toward unified, cloud-native, and highly automated ecosystems. In a series of deep-dive meetings and demonstrations at the recent show, I got a first-hand glimpse of the future of the physical security marketplace. Spoiler alert: The future is now! HID Global: Tearing down the silos HID Global is addressing the long-requested convergence of physical and digital security. Recognising that the industry has historically operated in silos, HID is now leading with a combined implementation team to leverage the power of both sides. HID is supporting the transition by combining its logical and physical security teams to help end users design secure, end-to-end journeys for their employees. By leveraging its massive existing footprint in physical access, HID is uniquely positioned to help organisations upgrade their cybersecurity posture without a total "rip and replace" of their hardware. HID is seeing a surge in demand for converged credentials that unite building access with digital identity. On the digital front, HID has implemented FIDO (Fast Identity Online) and passkeys to replace traditional passwords with more secure, biometric-backed authentication methods. Acre Security: Bridging the gap to the cloud Acre Security previewed a cloud-native video solution, reinforcing its cloud-first security strategyAcre Security is currently consolidating brands, bringing established names like Feenics and AccessIt under a single corporate umbrella. A primary theme for the company at ISC West is the migration of legacy systems to modern infrastructure. To facilitate the transition, they are launching "The Bridge," a technology designed to help on-premise customers transition to the cloud at a pace that suits their operational needs. The company is also expanding its portfolio into video. Attendees at the show received a preview of a new cloud-native video solution slated for release later this year, signaling Acre’s commitment to a holistic, cloud-first security suite. Acoem: Real-time acoustic threat detection With a 35-year foundation in vibration and acoustics—including military sniper detection—Acoem is providing gunshot detection through edge processing. Unlike systems that rely on the cloud and may suffer from latency, Acoem’s technology processes data at the sensor level for instant alerts. Their sensors are engineered for massive outdoor spaces, covering a 500-foot radius (roughly 11 football fields) and can detect high-powered rifle shots from up to half a mile away. The system provides critical intelligence by distinguishing between muzzle blasts and "mach noise" from bullet travel, delivering an audio file to the end-user that maps the location and direction of the threat. They use AI to filter out environmental false positives, such as skateboards hitting metal rails. Alarm.com: The all-in-one dealer ecosystem Beyond hardware, Alarm.com is leveraging AI to streamline the sales process Alarm.com is doubling down on "giving tools to dealers to help them be successful," with a focus on unified commercial solutions. A highlight at ISC West is their new fire communicator, which integrates fire monitoring into their single app, completing what they call the "fourth leg of the stool." The product allows fire systems to benefit from the same real-time customer engagement and push notifications that have long been available for intrusion and video. The key products, such as commercial-grade hardware, are now available for immediate purchase. Beyond hardware, Alarm.com is leveraging AI to streamline the sales process. Their new AI Proposal Builder uses customer meeting notes to automatically generate customised, value-driven sales proposals for dealers. Allegion: A global shift in credentialing Following the acquisition of ELATEC, Allegion is adopting a more global market approach and expanding its OEM business. The company is involved in the development of Aliro, the newly unveiled mobile credentialing standard. Allegion’s strategy is built on versatility: While Aliro serves the burgeoning mobile market, they also offer PKOC for plastic cards, allowing them to provide solutions regardless of the user's preferred credential type. The ELATEC acquisition has effectively filled previous gaps in their use-case portfolio, positioning them as a comprehensive provider for both physical and digital access needs. AtlasIED: Engineering for life safety Transitioning from audio to a fully automated threat detection company, AtlasIED showcased its new IPX line at ISC West. This modular platform uses a single PoE++ port to power various "plug-and-play" modules, allowing for easy system upgrades. Their gun detection technology achieves a 99% confidence rating by "stacking" AI models; it cross-references audio data with infrared signatures to detect muzzle flashes and air quality sensors for particulates. With systems already running in 80% of U.S. international airports, the company maintains 24/7 domestic engineering support to manage these "life-safety adjacent" environments. Axis Communications: Unifying connectivity Axis Communications is advancing network video with 4G/5G surveillance, reducing cabling needs Axis Communications continues to lead in network video, with a new focus on offering surveillance through 4G and 5G networks to eliminate the need for extensive cabling in long-range applications. Axis also introduced several specialised hardware pieces, including the P1486-LE global shutter camera for high-speed traffic monitoring and the Q2802-TE, which integrates thermal and visual monitoring into a single unit. To assist technicians, they launched a new installer app that uses Bluetooth for easier camera pairing and management directly from a mobile device. Axon: De-escalation through enterprise wearables Focusing on frontline safety, Axon is expanding from law enforcement into the enterprise sector with its retail and healthcare-focused body camera. Weighing only 0.25 lb, these cameras are designed to be less intimidating, using colorful designs and acting as a primary de-escalator for aggressive behavior. A clear front display signals when recording is active, striking a balance between safety and a non-intimidating appearance. These devices feature live-streaming and panic alarms that connect workers to a Global Security Operations Center (GSOC). To ensure the footage is legally viable, Axon maintains a rigorous audit trail that authenticates every action recorded. Genetec: The value of the unified platform Genetec is advocating for unified platforms that reduce the time between incident detection and resolution. They argue that AI is becoming a commodity and that the true value lies in unified platforms that reduce the time from incident to resolution. Their approach emphasises the "outcomes" customers need, such as allowing security teams to coalesce around an investigation quickly. Genetec remains a strong supporter of open systems for enterprise customers, ensuring they have the choice to integrate diverse technologies rather than being locked into a manufacturer’s “walled garden.” This flexibility is critical for high-end security environments that require tailored, responsive systems. Johnson Controls: Large-scale enterprise solutions Johnson Controls has made a significant push into the enterprise video market with C-Cure IQ, a standalone VMS designed for major hubs like airports and large campuses. Through a partnership with Scylla, they have integrated 11 advanced analytics—including facial recognition and weapons detection—directly into their cameras. They also showcased new multi-sensor panoramic cameras capable of "stitching" multiple images into a single 360-degree view. While innovating in video, Johnson Controls also confirmed modern upgrades to their intrusion line, including their legacy DSC Neo line. The new DSC PowerSeries Neo 5, a high-end residential and commercial platform, features an all-new user interface and built-in PowerG+. They have also begun shipping the IQ5 family lineup, which is powered by a Qualcomm DragonWing processor. ONVIF: Standardising the future of AI and cloud ONVIF continues to lead the charge in establishing common languages for the security industry. A major focus is their new "Cloud Profile," which enables cameras to connect directly to the cloud through a standardised protocol. They are also expanding into audio standards to ensure IP-based speakers can seamlessly connect to Video Management Systems (VMS). To combat the rise of sophisticated digital manipulation, ONVIF is developing "video signing" standards. ONVIF is actively seeking more diverse enterprise participation to help shape these emerging AI standardsThis feature protects the integrity of video for evidentiary purposes by embedding a digital signature and timestamp directly into the footage at the camera level. Additionally, the organisation has formed an AI Working Group to develop common communication methods for "AI agents" within physical security systems. ONVIF is actively seeking more diverse enterprise participation to help shape these emerging AI standards. Roberto Licari is the new ONVIF Ambassador, seeking to attract new companies (even outside the security sector) to ONVIF as they look to expand their offerings. SwiftConnect: Bridging digital and physical identity SwiftConnect is redefining access control by shifting the focus from physical cards to digital identity. As a cloud-based "connected access network," the platform bridges the gap between IT identity providers (like Okta or Azure AD) and legacy physical access control systems. At the show's Security Experience Center demonstrations, SwiftConnect showcased its ability to integrate mobile credentials within Apple and Google Wallets across multiple technology platforms. By aligning physical security with Zero Trust principles, they ensure that access is governed by the same rigorous standards as digital networks. Their software-centric approach allows for a more seamless employee experience while simplifying the management of complex, multi-site building security. This emphasises a future where the mobile device becomes the primary tool for navigating the physical workspace. Wasabi Technologies: Redefining cloud storage economics With cloud technology becoming a baseline requirement at every booth, Wasabi Technologies highlighted its "hot cloud storage" as a cost-effective alternative to major hyperscalers. Their model claims to be 80% less expensive than competitors, notably removing hidden fees. Wasabi is increasingly bundled at the "back end" of security solutions through partnerships with integrators and end users. A key feature for law enforcement and high-security sectors is their "Object Lock" capability, which ensures that video evidence remains untampered with and immutable during defined retention periods. By providing high-performance storage without the unpredictable costs typically associated with the cloud, Wasabi is positioning itself as the foundational layer for data-heavy video surveillance applications that require long-term, secure retention. Wasabi is positioning itself as the foundational layer for data-heavy video surveillance applications ZKTeco USA: Versatile and integrated access ZKTeco USA showcased a range of integrated solutions, including turnstiles, visitor management, and access control. Their Atlas access control series offers versatility, supporting everything from traditional readers and keypads to QR codes and fingerprint scanning, with the flexibility to operate on-premise or in the cloud. For tight environments, they introduced the Mars 100 turnstile, which features a compact 2x3-foot footprint. They also highlighted the Omni series, an all-in-one standalone reader-controller that manages access, intercom, and visitor functions in a single device. Innovation in portability was evident in their new walk-through metal detectors, which consist of two poles with an 8-hour battery life—ideal for schools and temporary events. While they offer their own Armatura readers, ZKTeco emphasised that their solutions can integrate with other industry leaders to fit diverse customer needs.

Technology's role in securing banks and financial institutions
Download
Security technologies promote real-time awareness in K-12 schools
Download
Integrated systems enable critical and compliant security for transportation
Download
Modernising physical access control
Download
Access. Intrusion. One estate.
Download
