In today’s increasingly complex cybersecurity landscape, malicious actors employ automation, artificial intelligence, and advanced techniques to bypass traditional security controls, making them elusive targets for security teams.
To address this challenge, organisations must transition from reactive to proactive security operations, actively seeking hidden threats before they escalate into major incidents. This shift is where AI-powered threat hunting is revolutionising the modern Security Operations Centre (SOC), harnessing artificial intelligence in conjunction with human expertise to detect advanced threats that might otherwise linger undetected for extended periods.
Proactive security operations
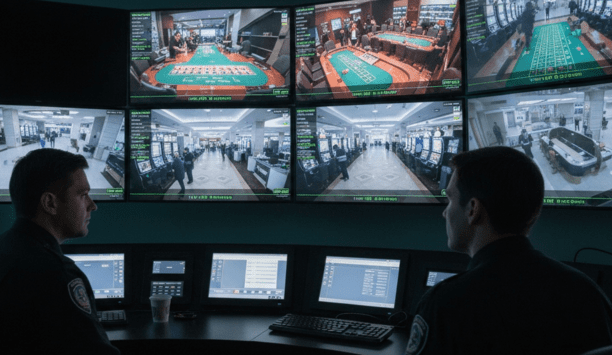
A Security Operations Centre acts as the nerve centre for monitoring, detecting, investigating, and responding to cybersecurity threats throughout an organisation. By integrating people, processes, and technology, it ensures continuous oversight of security events and potential risks. The core mission is to swiftly identify malicious activities, minimising their impact. SOC teams diligently monitor networks, endpoints, cloud systems, applications, and user activities for any indication of compromise.
The core mission is to swiftly identify malicious activities, minimising their impact
SOC analysts are tasked with scrutinising alerts produced by security tools, assessing their severity, verifying genuine threats, and managing response actions accordingly. Their remit extends to threat intelligence analysis, incident response, digital forensics, vulnerability management, and compliance reporting. Modern SOCs, however, exceed these functions, playing a strategic role in bolstering organisational resilience by identifying security weaknesses, enhancing detection capabilities, and consulting with leadership on emerging risks and threats.
Investigating genuine threats
Historically, SOCs operated reactively, relying on alerts to identify suspicious activities. While valuable, this approach often inundated analysts with countless alerts, many of which were false positives, consuming time that could be better spent on genuine threats. As cybercriminals grew more sophisticated, exploiting Advanced Persistent Threats (APTs), insider threats, and other tactics to remain undetected, organisations recognised the need for a proactive security model.
Modern SOCs now prioritise continuous threat hunting, behavioural analytics, attack surface monitoring, and predictive threat detection. This proactive approach involves analysts actively searching for indicators of compromise and suspicious patterns without waiting for security tools to trigger alerts. Artificial intelligence plays a vital role in this evolution, facilitating the proactive exploration of potential threats that evade conventional controls.
Suspicious privilege escalations
AI is pivotal in managing the vast data generated during threat hunting, analysing billions of events
Threat hunting involves security teams formulating hypotheses, utilising threat intelligence and behavioural analysis, and employing investigative techniques to uncover concealed threats. Analysts might scrutinise unusual user behaviour, unexpected network communications, or suspicious privilege escalations that could signify malicious activity. The aim is to unearth threats before they escalate into significant incidents.
AI is pivotal in managing the vast data generated during threat hunting, analysing billions of events in real-time and detecting subtle behavioural patterns that elude human detection. Machine learning models help establish normal activity baselines, identifying deviations suggestive of malicious actions. For example, AI might flag an employee account accessing sensitive systems or outliers in data transfers, connecting these anomalies into a coherent threat narrative for analysts, allowing them to prioritise high-investigation value incidents.
Enriched investigation findings
Rather than displacing security analysts, AI enhances their capabilities as a force multiplier. When suspicious activities are identified, AI systems compile contextual data from various sources, correlate connected events, and provide analysts with comprehensive investigation insights. This process streamlines investigation efforts, reduces response time, and lightens the operational load.
Rather than displacing security analysts, AI enhances their capabilities as a force multiplier
The integration of AI into threat hunting improves detection accuracy, operational efficiency, and scalability, particularly as organisations adapt to cloud services, remote work models, and an expanded data footprint. AI not only curtails alert fatigue but also assists analysts in prioritising investigations effectively, enabling SOC teams to shift from a reactive stance to a more anticipatory approach, capable of disrupting threats early in their cycle.
Providing contextual understanding
Security analysts bring invaluable contextual understanding, critical thinking, business acumen, and strategic decision-making to security investigations, skills that machines alone cannot replicate. Their expertise in validating findings, deciphering complex attack scenarios, and formulating appropriate responses is essential. A collaborative model leveraging both AI-driven analytics and experienced human analysts delivers an optimal blend of speed and insight.
As adversaries grow more adept, the traditional reactive security models fall short in addressing novel threats. AI-powered threat hunting empowers SOCs to preemptively identify hidden threats, surface advanced attack methods, and expedite investigations, thereby enhancing organisational security. The evolution of security operations relies on the symbiotic relationship between technology and skilled analysts, working in tandem to fortify defence measures more effectively than ever before.
Attackers are using automation, artificial intelligence, and increasingly sophisticated techniques to evade traditional security controls, turning malicious actors into a moving target for security teams. In this environment, organisations can no longer rely solely on reactive security measures that respond to threats after they have already caused damage. Instead, they need proactive security operations that actively search for hidden threats before they escalate into major incidents.
This is where AI-powered threat hunting is transforming modern Security Operations Centre (SOC). By combining the speed and scale of artificial intelligence with the expertise of human analysts, organisations can uncover advanced threats that might otherwise remain undetected for weeks or even months.
Proactive security operations
In this article, you will learn what a SOC does, how modern SOC differ from those of the past, how AI is enhancing threat hunting capabilities, and why proactive security operations have become essential for defending against today's cyber adversaries.
A Security Operations Centre serves as the central hub for monitoring, detecting, investigating, and responding to cybersecurity threats across an organisation's environment. It brings together people, processes, and technology to provide continuous visibility into security events and potential risks. The primary function of a SOC is to identify malicious activity as quickly as possible and minimise its impact on the organisation. To achieve this, SOC teams continuously monitor networks, endpoints, cloud environments, applications, and user activity for signs of compromise.
Traditional security controls
SOC analysts investigate alerts generated by security tools, assess their severity, determine whether they represent genuine threats, and coordinate appropriate response actions. They also perform threat intelligence analysis, incident response, digital forensics, vulnerability management, and compliance reporting.
Beyond responding to alerts, modern SOCs play an increasingly strategic role in strengthening organisational resilience. They help identify security weaknesses, improve detection capabilities, and provide leadership teams with insights into emerging threats and risks.
Investigating genuine threats
Traditional SOC were primarily reactive in nature. Their focus was largely centred on monitoring alerts generated by security tools and responding when suspicious activity was detected.
While this approach provided value, it often created significant challenges. Analysts were overwhelmed by thousands of alerts every day, many of which turned out to be false positives. Valuable time was spent manually reviewing events rather than investigating genuine threats.
At the same time, cybercriminals became more sophisticated. Advanced Persistent Threats (APTs), insider threats, ransomware groups, and state-sponsored attackers learned how to operate quietly within environments for extended periods. Many attacks could bypass conventional detection mechanisms altogether. As a result, organisations began shifting towards a more proactive security model.
Attack surface monitoring
Modern SOCs focus not only on alert response but also on continuous threat hunting, behavioural analytics, attack surface monitoring, and predictive threat detection. Rather than waiting for security tools to raise an alarm, analysts actively search for indicators of compromise and suspicious patterns that may indicate hidden adversary activity. Artificial intelligence has become one of the key technologies enabling this transformation.
Threat hunting is the proactive process of searching for cyber threats that have evaded existing security controls and detection systems. Unlike traditional detection methods, threat hunting does not depend solely on predefined rules or alerts. Instead, security teams use hypotheses, threat intelligence, behavioural analysis, and investigative techniques to identify hidden threats within their environments.
Suspicious privilege escalations
A threat hunter might investigate unusual user behaviour, unexpected network communications, suspicious privilege escalations, or anomalies in system activity that could indicate malicious activity. The goal is to discover threats before they trigger an incident or cause significant harm.
Consider this hypothetical question:
- What if a sophisticated attacker gained access to your network today but deliberately avoided triggering every alert configured in your security tools?
- Without proactive threat hunting, that attacker could potentially remain undetected for months while gathering sensitive information or establishing persistence. This is precisely why modern organisations are investing heavily in advanced threat hunting capabilities.
Accessing sensitive systems
Threat hunting generates enormous amounts of data. Analysts must examine logs, network traffic, endpoint telemetry, user activity, cloud events, and threat intelligence feeds across complex environments.
Artificial intelligence helps make sense of this vast volume of information. AI-powered systems can analyse billions of events in real time, identify subtle behavioural patterns, and surface anomalies that would be nearly impossible for humans to detect manually. Machine learning models can establish baselines for normal activity and identify deviations that may indicate malicious behaviour. These systems continuously learn and adapt as environments evolve.
For example, AI may identify an employee account accessing sensitive systems at unusual times, transferring abnormal volumes of data, or exhibiting behaviours inconsistent with historical patterns. While each activity may appear harmless in isolation, AI can correlate them into a meaningful threat narrative. This enables analysts to focus on high-priority investigations rather than manually sorting through countless low-value alerts.
Enriched investigation findings
AI is not replacing security analysts. Instead, it is acting as a force multiplier that enhances their effectiveness. When suspicious activity is detected, AI can automatically gather contextual information from multiple sources, correlate related events, and present analysts with enriched investigation findings. This significantly reduces investigation time and accelerates decision-making.
For instance, AI can automatically identify affected assets, map attack paths, retrieve threat intelligence, assess potential business impact, and recommend response actions. Rather than spending hours collecting information from various tools, analysts can begin investigating immediately with a comprehensive understanding of the incident. The result is faster threat detection, quicker containment, and reduced operational workload.
AI-powered threat hunting
One of the greatest advantages of AI-powered threat hunting is improved detection accuracy. Advanced analytics can uncover subtle indicators of compromise that traditional tools may overlook. AI also improves operational efficiency by automating repetitive tasks, reducing alert fatigue, and helping analysts prioritise investigations more effectively.
Another significant benefit is scalability. As organisations adopt cloud services, remote work models, and connected devices, security data volumes continue to grow exponentially. AI enables SOC teams to manage this complexity without proportionally increasing staffing requirements.
Perhaps most importantly, AI helps organisations move from a reactive security posture to a proactive one. Instead of responding after an attack occurs, security teams can identify and disrupt threats earlier in the attack lifecycle.
Providing contextual understanding
Security analysts provide contextual understanding, critical thinking, business awareness, and strategic decision-making that machines cannot replicate. They validate findings, investigate complex attack scenarios, interpret nuanced situations, and determine appropriate response actions.
The most effective SOCs combine AI-driven analytics with experienced human analysts who can apply judgement and expertise to security investigations. This collaborative model delivers the best of both worlds: machine speed and human insight.
Overall security posture
The cybersecurity landscape continues to grow more complex, and organisations face increasingly sophisticated adversaries. Traditional reactive security models are no longer sufficient to address modern threats.
AI-powered threat hunting allows modern SOCs to proactively identify hidden threats, uncover advanced attack techniques, and accelerate investigations before significant damage occurs. By combining artificial intelligence with skilled analysts, organisations can improve visibility, reduce response times, and strengthen their overall security posture.
The future of security operations is not about replacing people with machines. It is about enabling people and technology to work together more effectively than ever before.